Skip to content
November 15, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • ADVISORIES
    • Microsoft
    • Fortinet
    • Ivanti
    • Cisco
    • Linux
    • Citrix
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q3 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Malware
  • Vulnerability News
  • Submit Press Release
Light/Dark Button
  • Home
  • News
  • Technology
  • The Great iOS Update: Dual Accounts, AI Magic, and Storage Surgery Finally Hit WhatsApp for iPhone
  • Technology

The Great iOS Update: Dual Accounts, AI Magic, and Storage Surgery Finally Hit WhatsApp for iPhone

Do Son March 30, 2026 3 minutes read
0
WhatsApp iPhone dual account 2026

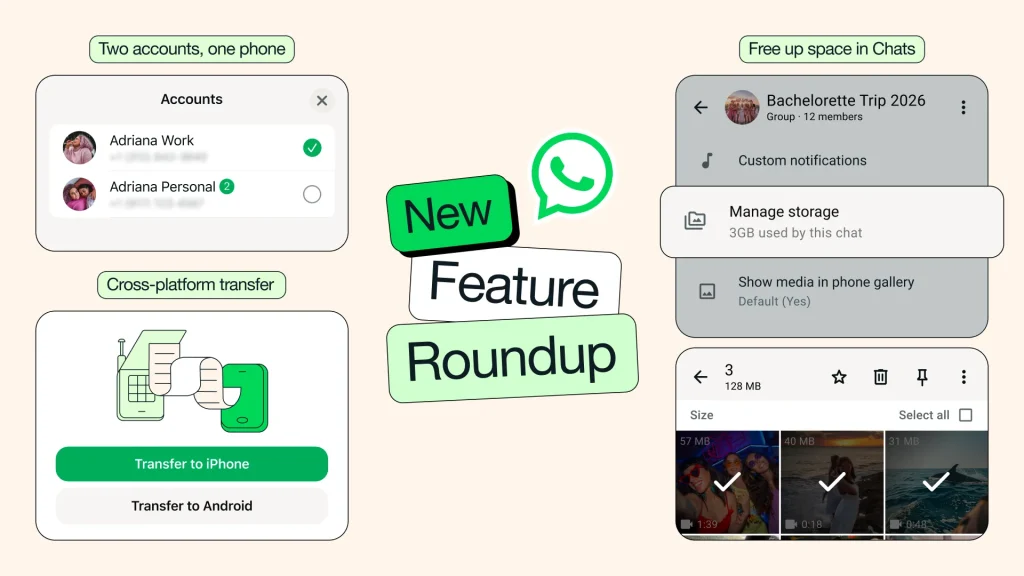
Following an arduous epoch of anticipation, WhatsApp has ultimately bestowed the profoundly coveted “dual account” functionality upon iPhone patrons. Beyond empowering iOS apparatuses to simultaneously harbor twin accounts, Meta has promulgated a constellation of pragmatic enhancements for WhatsApp. This encompasses profoundly more fluid cross-platform migrations of conversational chronicles, exquisitely intuitive governance of storage repositories, and the indispensable integration of the Meta AI steward, provisioning patrons with ethereal image manipulation and eloquent compositional counsel.

For a considerable epoch, Android denizens have effortlessly oscillated between a multitude of WhatsApp accounts upon a solitary apparatus; presently, the denizens of the iOS ecosystem are finally empowered to wield this profoundly convenient capability.

  • Dual Account Ingress: iPhone patrons are now granted the sovereignty to simultaneously authenticate two sovereign WhatsApp accounts. The architecture shall vividly illuminate the currently active avatar within the basal navigation tier, meticulously guiding patrons to perform a dual verification prior to dispatching missives, thereby adroitly circumventing the agonizing mortification of misdirecting professional or intimate correspondence.
  • Ascendant Cross-Platform Migration: To vanquish the profound tribulations associated with transitioning apparatuses, WhatsApp has exquisitely refined the choreography of migrating conversational chronicles. Whether orchestrating an ascension within a singular ecosystem or embarking upon a cross-platform exodus betwixt iOS and Android, this nascent migration paradigm guarantees that the preservation of dialogue remains profoundly steadfast and remarkably effortless.

As the relentless deluge of auditory missives, high-fidelity tapestries, and cinematic recordings perpetually consumes colossal swaths of storage, this encumbrance has long stood as a paramount tribulation for patrons. Consequently, this contemporary rejuvenation bestows a profoundly direct and definitive resolution.

  • Intuitive Spatial Purification: Patrons need merely tap the nomenclature of the conversational sanctum to breach the “Manage Storage” enclave, empowering them to directly excise colossal archives that voraciously devour spatial reserves within that specific domain.
  • Sovereign Multimedia Eradication: The architecture provisions a bespoke prerogative, permitting patrons to orchestrate the wholesale eradication of multimedia artifacts (such as cinematic recordings and photographic tapestries) exclusively within a designated discourse. This meticulous purging leaves the sanctity of the textual narrative entirely unmarred, thereby efficaciously vanquishing the profound anxieties tethered to diminishing apparatus capacity.

Within the technological renaissance of 2026, the omnipresence of generative artificial intelligence is absolute. Through this profound assimilation of Meta AI’s cognitive prowess, WhatsApp has irrevocably transfigured diurnal communication, rendering it exquisitely more elastic and undeniably prolific.

  • Intelligent Somatic Manipulation: The platform now champions ethereal photographic refinement capabilities, encompassing the instantaneous banishment of backgrounds, the transmutation of visual aesthetics, and the deployment of AI to meticulously obliterate undesirable detritus and anomalous elements from the tableau.
  • Compositional Counsel (Writing Help): When a patron finds themselves adrift, uncertain of how to inaugurate or respond to a profoundly formal missive, the AI steward stands ready to meticulously draft the initial manuscript and elegantly polish its overarching tone.
  • The Covenant of Privacy: Meta’s sovereign heralds have explicitly underscored within their corporate chronicles that, even whilst wielding the compositional counsel of the AI, the patron’s intimate discourse shall remain shrouded in absolute, impenetrable privacy, flawlessly preserving the inviolable sanctuary of its End-to-End Encryption.
Add Daily CyberSecurity as a preferred source on Google

Related coverage

  • Chromium Reopens JPEG-XL Debate: Will Google Reinstate Support After Apple Adopted It?
  • Copilot Gets Brains: Microsoft Unveils ‘Work IQ’ & Agent Mode Integration with GPT-5 and Anthropic
  • Did Google’s promotion of HTTPS go astray?
  • The Cloud in Flames: AWS Bahrain Fire Signals a New Era of Kinetic Strikes on Tech Infrastructure
  • OpenAI Launches Project Daybreak and GPT-5.5-Cyber to Counter Anthropic’s Glasswing
  • Most Americans think AI to lead to job losses
Track all actively exploited CVEs →

Support Our Threat Intelligence

Find our tech and OS security coverage helpful? Support our work today and unlock a 100% ad-free reading experience!

Buy Me a Coffee Logo Buy Me a Coffee
Select your plan
Free Pro Team

Hover over a plan to see its benefits.

Get Zero-Hour Vulnerability Alerts

Critical CVEs, CVSS scores, and PoC updates — straight to your inbox every week.

We respect your inbox. Unsubscribe anytime.

SHARE
Share on FacebookShare on XShare on LinkedInShare on TelegramShare on BlueskyShare on Mastodon
Written by
@DdoS · Security Researcher

Do Son

Do Son is the Founder and Editor of Daily CyberSecurity. Working in cybersecurity since 2013, he reports on vulnerabilities, malware, and emerging threats, providing timely analysis to help organizations and individuals stay ahead of evolving risks.

Tags: Cross-Platform Migration Dual Account End-to-End Encryption iOS 2026 iphone Meta AI Photo Editing privacy Storage Management WhatsApp WhatsApp Update

Leave a Reply Cancel reply

You must be logged in to post a comment.

🚨 Active Exploits in the Wild

  • CVE-2024-58406CVSS 8.7
    Huatian Dynamic OA8000 collaborative office system contains an unauthenticated path traversal vulnerability in /OAapp/jsp/trace/ntkodownload.jsp, where the filename request...
    Watchtower Verified📅 Updated: Nov 13, 2026
  • CVE-2026-114713CVSS 8.6
    The labeled-response module in UnrealIRCd 6.0.0 before 6.2.7.1 does not escape the IRCv3 "label" message tag when echoing...
    CISA KEV📅 Added to KEV: Nov 13, 2026
  • CVE-2026-123039CVSS 7.8
    The Gaia OS DynamicCLI daemon runs as root and listens on a world-writable local socket (/tmp/dynamic_socket) without authenticating...
    CISA KEV📅 Added to KEV: Nov 13, 2026
  • CVE-2026-20320CVSS 7.5
    A vulnerability in the Open Client Interface (OCI) XML Parser of Cisco BroadWorks could allow an unauthenticated, remote...
    CISA KEV📅 Added to KEV: Nov 10, 2026
  • CVE-2026-111793CVSS 4.3
    Openwave Webtop Media Transcoder does not enforce administrator-defined file type restrictions to restrict the file-types to be converted....
    CISA KEV📅 Added to KEV: Nov 10, 2026
  • CVE-2026-111560CVSS 8.6
    Improper neutralization of shell metacharacters in the timezone configuration field in certain Barracuda appliance products using common Barracuda...
    CISA KEV📅 Added to KEV: Nov 10, 2026
  • CVE-2026-116606CVSS 9.3
    An authentication bypass in Barracuda Email Security Gateway versions earlier than 9.4.0.030 allows an unauthenticated remote attacker to...
    CISA KEV📅 Added to KEV: Nov 10, 2026
  • CVE-2026-125350
    Use after free in XML. Reported by anonymous on 2026-11-06. Google is aware that an exploit for CVE-2026-125350...
    CISA KEV📅 Added to KEV: Nov 10, 2026
Powered by CVE Watchtower

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Get free CVE alerts Pro from $7/mo

Critical Vulnerabilities

  • CVE-2026-129354CVSS 10.0
    A flaw has been found in D-Link DIR-600L 2.17b02. Affected by this issue is the function hnap_main of...
    📅 Updated: Nov 15, 2026
  • CVE-2026-129353CVSS 10.0
    A vulnerability was detected in D-Link DIR-600L 2.17/2.17b02. Affected by this vulnerability is the function authenticationcgi_main of the...
    📅 Updated: Nov 14, 2026
  • CVE-2026-129352CVSS 9.4
    A vulnerability was detected in TRENDnet TEW-657BRM 1.00.1. This issue affects some unknown processing of the file /usr/sbin/upgrade_flash.cgi....
    📅 Updated: Nov 14, 2026
  • CVE-2026-129351CVSS 10.0
    A security vulnerability has been detected in TRENDnet TEW-657BRM 1.00.1. This vulnerability affects the function sprintf of the...
    📅 Updated: Nov 14, 2026
  • CVE-2026-54831CVSS 9.3
    Improper Neutralization of Special Elements used in an SQL Command ('SQL Injection') vulnerability in AyeCode Ltd GeoDirectory geodirectory...
    📅 Updated: Nov 14, 2026
  • CVE-2026-129261CVSS 9.3
    A vulnerability was found in Kingston FURY CTRL RGB Control Software up to 2.0.66.0. The impacted element is...
    📅 Updated: Nov 14, 2026
  • CVE-2026-59514CVSS 9.3
    Improper Neutralization of Special Elements used in an SQL Command ('SQL Injection') vulnerability in BuddyBoss Buddyboss Platform buddyboss-platform...
    📅 Updated: Nov 14, 2026
  • CVE-2026-62031CVSS 9.3
    Improper Neutralization of Special Elements used in an SQL Command ('SQL Injection') vulnerability in StylemixThemes uListing ulisting allows...
    📅 Updated: Nov 14, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About Daily CyberSecurity
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DMCA
  • Privacy Policy

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.