
 Do Son
Attackers are exploiting a ServiceNow sandbox escape RCE in the wild. Public proof-of-concept details for CVE-2026-6875 pre-auth code execution are out.
Cloudflare deploys emergency WAF rules to block the critical WordPress wp2shell vulnerability. Update your site now to prevent severe RCE security risks.

Microsoft will gradually end OneDrive updates and support for Windows 10 versions 21H2 and 22H2. Discover the complete timeline and alternatives for users.
Ubuntu Pro Client vulnerability CVE-2026-11386 (CVSS 9.0) lets a spoofed contract server inject APT sources and run code with root privileges.
WordPress pre-auth RCE CVE-2026-63030 chains a REST batch bug with SQL injection. Details and a public PoC are out. Update to WordPress 7.0.2 now.
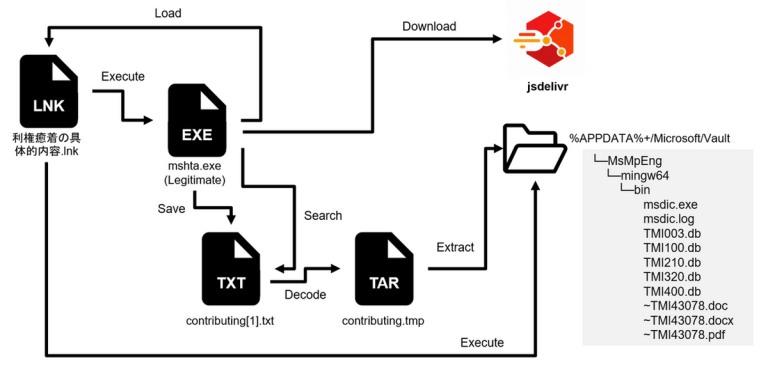
JPCERT/CC details new APT-C-60 attacks on Japan. The group abuses Proton Drive, LNK files, and GitHub to deploy SpyGlace malware.

As cyber threats continue to grow and SSL certificate lifecycles become shorter, businesses need a security provider...

In today’s digital world, protecting websites, applications, users, and sensitive data requires more than simply installing an...
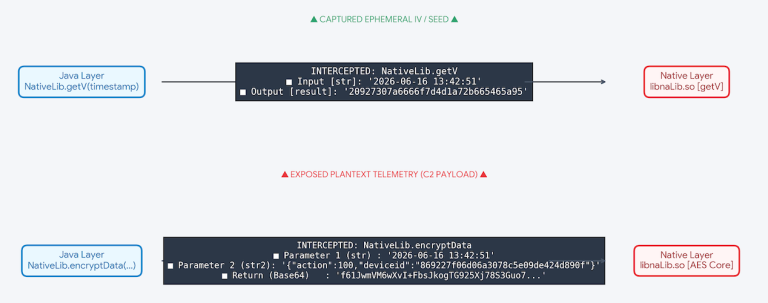
The GoldPickaxe banking Trojan returns, stealing biometric data, SMS, and lock screens from Android users across Asia, Zimperium warns.
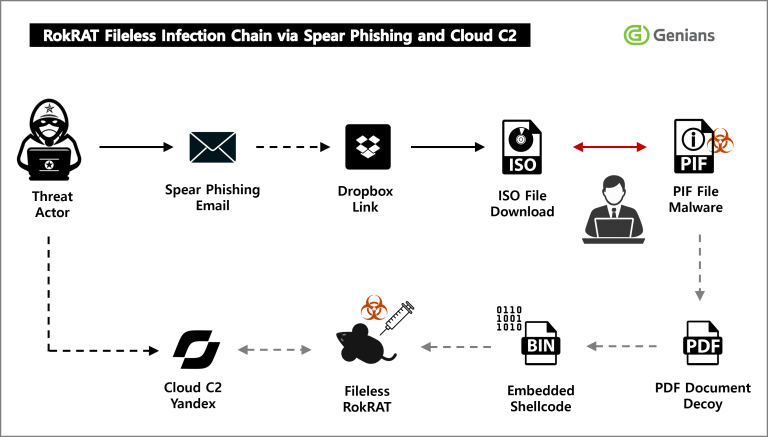
Genians exposed Operation Capsule Vault, an APT37 campaign. The RokRAT malware hides inside a fake PDF to spy on academics and researchers.
Kyverno vulnerability CVE-2026-54523 (CVSS 9.6) is public with PoC exploit code. It lets a tenant gain admin in any namespace. Update to v1.18.2.
Citrix patched CVE-2026-53565, a Citrix Secure Access vulnerability letting local users gain SYSTEM, plus the CVE-2026-53566 out-of-bounds read bug.
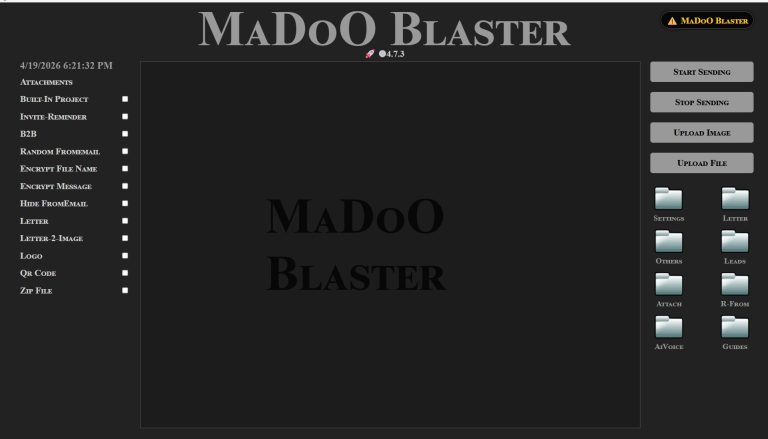
A misconfigured server exposed three AiTM phishing operators running Evilginx MFA bypass and Device Code attacks on Microsoft 365 accounts.
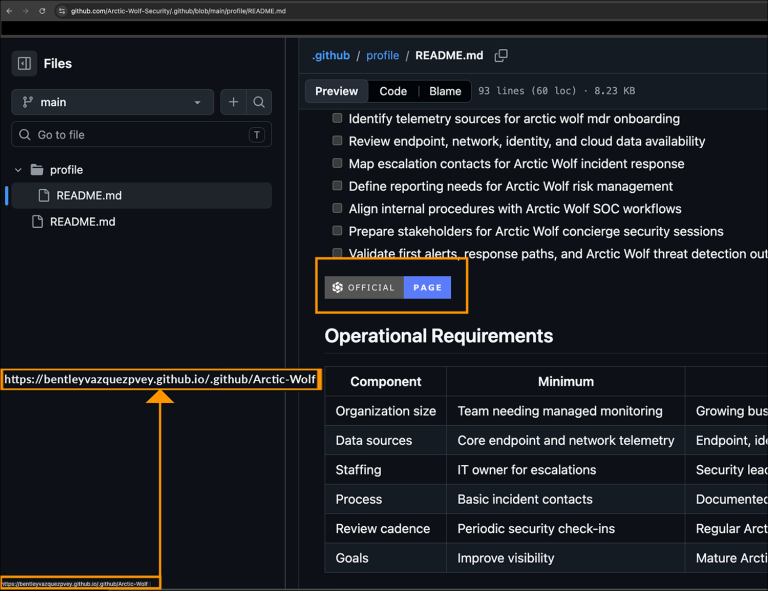
Arctic Wolf found 292 fake GitHub repositories impersonating software vendors to deliver a BoryptGrab-lineage infostealer via DLL side-loading.

The Google DMA ruling forces Android to open core access to rival AI assistants and share search data by 2027, sparking privacy and security warnings.

Google rebrands NotebookLM as Gemini Notebook, adding native code execution, AI Mode integration, and citing over 30 million active users.

Chrome security update 150.0.7871.128 patches 7 flaws, including three critical use-after-free bugs in CameraCapture, GPU, and Network. Update now.

Doctor Web found a supply chain trojan targeting software developers. This developer-targeting malware steals data, crypto wallets, and mines coins.

TP-Link Kasa vulnerability CVE-2026-9770 (CVSS 8.6) lets local attackers intercept admin credentials on EC70 and EC71 cameras. Update firmware now.
CISA KEV catalog adds three actively exploited flaws: FortiSandbox CVE-2026-25089, CVE-2026-39808, and SharePoint CVE-2026-58644. Patch by July 19.
7-Zip vulnerability CVE-2026-14266 (CVSS 7.0) allows remote code execution via crafted XZ data. Update to 7-Zip 26.02. No exploitation confirmed.
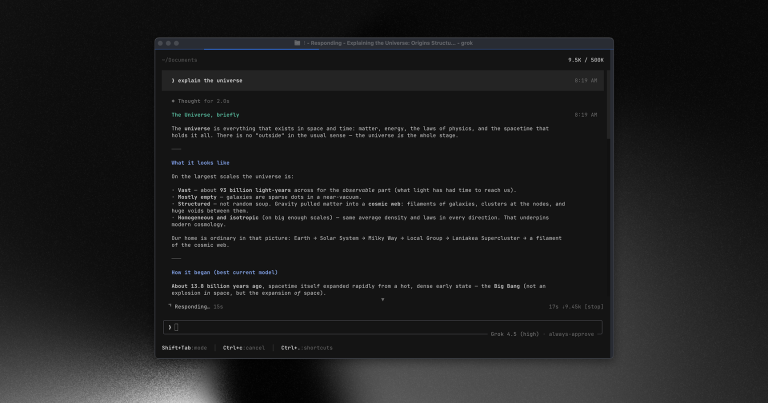
Grok Build open source release lets the community audit the code with data sharing disabled by default, yet GitHub Issues and PRs remain closed.