Skip to content
November 8, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
CVE-2026-15378: Blind SSRF Flaw in Red Hat OpenShift AI Red Hat OpenShift AI blind SSRF flaw CVE-2026-15378 in guardrails-detectors component
  • Vulnerability Report

CVE-2026-15378: Blind SSRF Flaw in Red Hat OpenShift AI

Do Son July 16, 2026 0

CVE-2026-15378 is a blind SSRF in Red Hat OpenShift AI. The guardrails-detectors flaw exposes cloud credentials and Kubernetes secrets.
Microsoft Untangles Its Messy Windows Update Terminology: B Releases, Quality Updates, and More Windows monthly updates terminology explained including B release and quality updates
  • Windows

Microsoft Untangles Its Messy Windows Update Terminology: B Releases, Quality Updates, and More

Do Son July 16, 2026 0

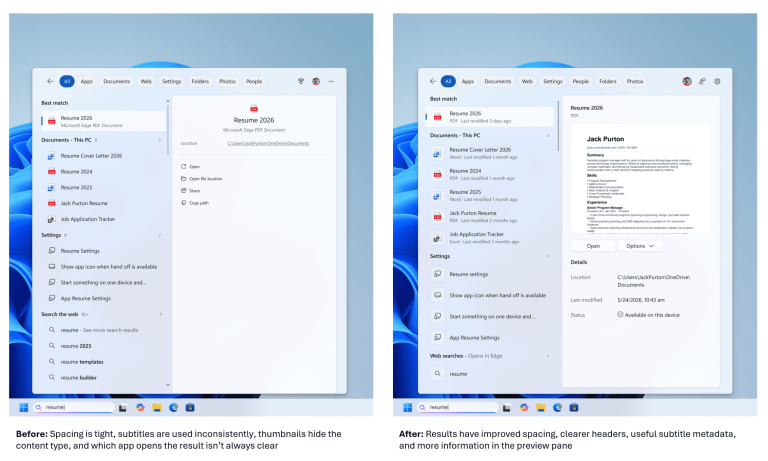
Microsoft explains Windows monthly updates terminology: B releases, quality updates, optional previews, OOB patches, and CFR rollouts clarified.
Metabase Fixes CVE-2026-59827 and CVE-2026-59826 Remote Code Execution Flaws Metabase remote code execution via CVE-2026-59827 unsafe H2 deserialization flaw
  • Vulnerability Report

Metabase Fixes CVE-2026-59827 and CVE-2026-59826 Remote Code Execution Flaws

Do Son July 16, 2026 0

Metabase patched CVE-2026-59827 (CVSS 9.9) and CVE-2026-59826 (CVSS 9.1). These flaws enable remote code execution via unsafe H2 deserialization.
Apache IoTDB Patches Five Security Flaws, Upgrade to 2.0.10 Apache IoTDB time-series database server affected by five patched security vulnerabilities
  • Vulnerability Report

Apache IoTDB Patches Five Security Flaws, Upgrade to 2.0.10

Do Son July 16, 2026 0

Apache IoTDB fixes five flaws in its time-series database, including privilege escalation and an unauthenticated DoS. Upgrade to 2.0.10 now.
SonicWall SMA1000 CVE-2026-15409 (CVSS 10.0) RCE Exploited in the Wild as Public PoC Drops SonicWall SMA1000 vulnerability CVE-2026-15409 remote code execution exploited in the wild
  • Vulnerability Report

SonicWall SMA1000 CVE-2026-15409 (CVSS 10.0) RCE Exploited in the Wild as Public PoC Drops

Do Son July 16, 2026 0

SonicWall SMA1000 vulnerability CVE-2026-15409 (CVSS 10.0) is exploited in the wild. Public PoC enables remote code execution patch now.
Dell PowerFlex Manager Flaw CVE-2026-56688 Allows Root Command Execution Dell PowerFlex command execution via CVE-2026-56688 OS command injection flaw
  • Vulnerability Report

Dell PowerFlex Manager Flaw CVE-2026-56688 Allows Root Command Execution

Do Son July 16, 2026 0

Dell patched CVE-2026-56688, a PowerFlex command execution bug. This OS command injection flaw lets a privileged attacker run code as root.
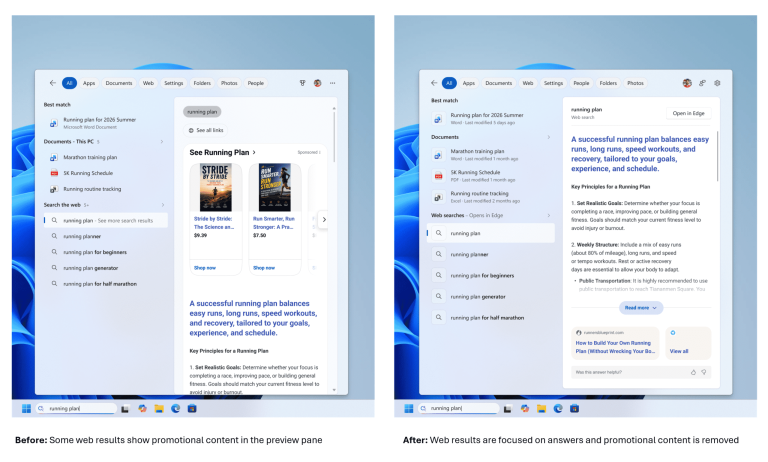
Microsoft Blocks the July 2026 Security Update on Dell Devices Over an Intel Driver Conflict Windows 11 update blocked on Dell devices due to Intel driver compatibility issue
  • Windows

Microsoft Blocks the July 2026 Security Update on Dell Devices Over an Intel Driver Conflict

Do Son July 16, 2026 0

Microsoft has the Windows 11 update blocked on some Dell devices after an Intel driver clashed with the new USB-C Connection Manager from KB5095093.
Elon Musk: X/Twitter Will Fully Open-Source Its Codebase for Public Review X Twitter open source codebase announcement by Elon Musk
  • Technology

Elon Musk: X/Twitter Will Fully Open-Source Its Codebase for Public Review

Do Son July 16, 2026 0

Elon Musk says X Twitter open source plans will cover the entire codebase for review, backed by independent audits but no timeline exists yet.
Age of Empires CVE-2026-50663: High-Risk Lobby Bug Fixed Age of Empires CVE security warning and bug details.
  • Vulnerability Report

Age of Empires CVE-2026-50663: High-Risk Lobby Bug Fixed

Do Son July 16, 2026 0

Microsoft patched a severe Age of Empires CVE. Attackers exploited game lobbies for remote code execution. Update your game immediately to stay safe.
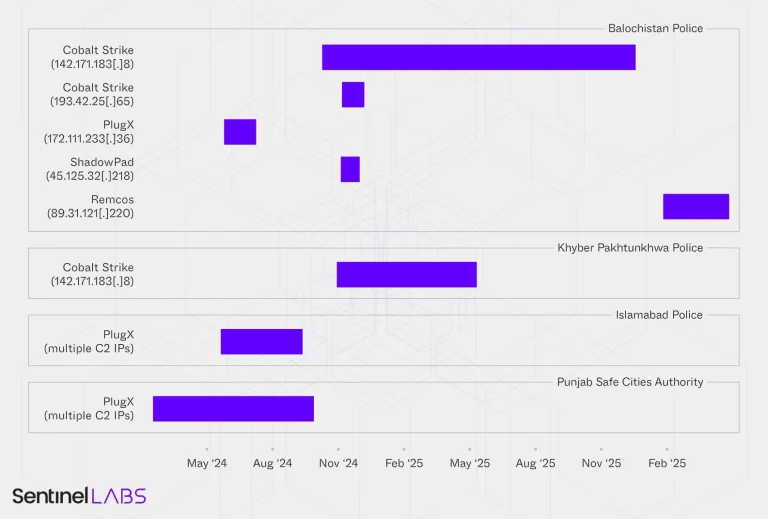
China and India Cyberespionage Converge on Pakistani Law Enforcement Chinese cyberespionage against Pakistani law enforcement targeting Balochistan Police records
  • Cybercriminals

China and India Cyberespionage Converge on Pakistani Law Enforcement

Do Son July 16, 2026 0

SentinelLABS found Chinese cyberespionage and India-nexus actors converging on Pakistani law enforcement, hitting Balochistan Police records and citizens.
Albiriox Android Banking Trojan Spreads Through Fake UniCredit Rewards on Telegram Albiriox malware Android banking trojan spread via fake UniCredit banking rewards and Telegram bot
  • Malware

Albiriox Android Banking Trojan Spreads Through Fake UniCredit Rewards on Telegram

Do Son July 16, 2026 0

Albiriox malware spreads via a fake UniCredit reward and a Telegram bot. The Android banking trojan abuses Accessibility to steal OTPs and hijack devices.
Helix Data Extortion Group Emerges from BlackFile, ReliaQuest Reports Helix data extortion group using device code phishing to exfiltrate data from SharePoint
  • Cybercriminals

Helix Data Extortion Group Emerges from BlackFile, ReliaQuest Reports

Do Son July 16, 2026 0

ReliaQuest links the new Helix data extortion group to BlackFile, using vishing and device code phishing to steal SharePoint data.

GigaWiper Backdoor Bundles Disk Wiping Malware and Fake Ransomware illegal streaming networks complex criminal enterprises UAT-7290 China-nexus Espionage Adversarial Misuse of Generative AI
  • Malware

GigaWiper Backdoor Bundles Disk Wiping Malware and Fake Ransomware

Do Son July 16, 2026 0

Microsoft exposes the GigaWiper backdoor, a destructive tool that bundles disk wiping malware, fake ransomware, and remote control in one implant.
CISA Adds Oracle E-Business Suite and KNX Flaws to KEV Catalog CISA KEV catalog additions CVE-2026-46817 and CVE-2023-4346 illustration
  • Vulnerability Report

CISA Adds Oracle E-Business Suite and KNX Flaws to KEV Catalog

Do Son July 16, 2026 0

CISA KEV catalog now lists CVE-2026-46817, a critical Oracle E-Business Suite flaw, and CVE-2023-4346 in KNX devices. Both are exploited in the wild.
Splunk Fixes Three Splunk Enterprise Vulnerabilities Led by CVE-2026-20296 CSRF Flaw Splunk Enterprise vulnerabilities CVE-2026-20296 security advisory illustration
  • Vulnerability Report

Splunk Fixes Three Splunk Enterprise Vulnerabilities Led by CVE-2026-20296 CSRF Flaw

Do Son July 16, 2026 0

Splunk patched three Splunk Enterprise vulnerabilities: CVE-2026-20296 CSRF, CVE-2026-20297 path traversal, and CVE-2026-20298 credential exposure.
NGINX Code Execution Vulnerability CVE-2026-42533 Patched Alongside Two Memory Flaws NGINX code execution vulnerability CVE-2026-42533 advisory illustration
  • Vulnerability Report

NGINX Code Execution Vulnerability CVE-2026-42533 Patched Alongside Two Memory Flaws

Do Son July 16, 2026 0

F5 patched the NGINX code execution flaw CVE-2026-42533, along with CVE-2026-60005 and CVE-2026-56434. Update NGINX Plus and Open Source builds now.
RabbitMQ Patches Two Critical Authentication Bypass Flaws RabbitMQ authentication bypass via TLS client cert forgery and OAuth2 JWKS flaw
  • Vulnerability Report

RabbitMQ Patches Two Critical Authentication Bypass Flaws

Do Son July 15, 2026 0

Two critical RabbitMQ flaws allow authentication bypass. One forges TLS client certs; the other tricks OAuth2 JWKS to accept any JWT.

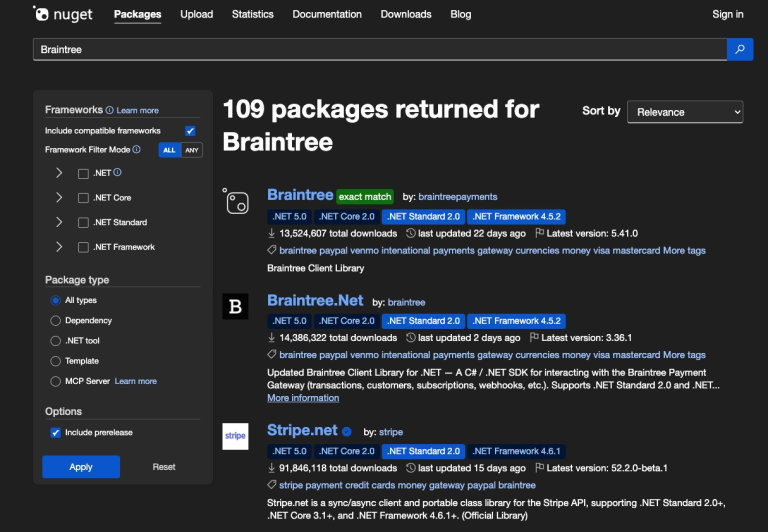
Fake Braintree NuGet Package Skims Credit Cards and Steals Merchant API Keys Braintree NuGet typosquat credit card skimmer stealing payment data and merchant API keys
  • Malware

Fake Braintree NuGet Package Skims Credit Cards and Steals Merchant API Keys

Do Son July 15, 2026 0

A malicious NuGet package, Braintree.Net, acts as a credit card skimmer and steals merchant API keys. The Braintree NuGet typosquat hits .NET devs.

Pulse Security Debuts Operational Management Platform Built for Security Leaders pulse_security_ai_logo_stack_rgb_lightmode_black_t_1784060191DoBnutvtFo
  • Press Release

Pulse Security Debuts Operational Management Platform Built for Security Leaders

cybernewswire July 15, 2026 0
San Francisco, United States, 15th July 2026, CyberNewswire
Read More Read more about Pulse Security Debuts Operational Management Platform Built for Security Leaders
CVE-2026-53412: CVSS 9.8 Zoom Vulnerability Allows Unauthenticated Account Takeover Zoom vulnerability CVE-2026-53412 account takeover flaw in Zoom Workplace for Windows
  • Vulnerability Report

CVE-2026-53412: CVSS 9.8 Zoom Vulnerability Allows Unauthenticated Account Takeover

Do Son July 15, 2026 0

Zoom vulnerability CVE-2026-53412 (CVSS 9.8) allows unauthenticated account takeover over the network. Update Zoom Workplace for Windows to 7.0.0 now.

Clubfoot Wolf Hits Russian Firms With NetSupport Manager exfiltrating AWS credentials - fabrice package
  • Cybercriminals

Clubfoot Wolf Hits Russian Firms With NetSupport Manager

Do Son July 15, 2026 0

Clubfoot Wolf targets Russian companies with phishing that drops NetSupport Manager as a stealthy remote access tool, BI.ZONE reports.
JetBrains Fixes CVSS 10 YouTrack Authentication Bypass and Five More Flaws in IntelliJ IDEA and TeamCity JetBrains vulnerabilities CVE-2026-62422 YouTrack authentication bypass CVSS 10
  • Vulnerability Report

JetBrains Fixes CVSS 10 YouTrack Authentication Bypass and Five More Flaws in IntelliJ IDEA and TeamCity

Do Son July 15, 2026 0

JetBrains vulnerabilities patched: CVE-2026-62422 (CVSS 10) YouTrack authentication bypass, IntelliJ IDEA RCE CVE-2026-59792, and four TeamCity flaws.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-18535CVSS 9.6
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 are vulnerable to a Regular Expression Denial of...
    📅 Updated: Nov 8, 2026
  • CVE-2026-17409CVSS 9.4
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote attacker to execute unauthorized...
    📅 Updated: Nov 8, 2026
  • CVE-2026-123614CVSS 9.3
    imgproxy from 4.0.0 before 4.0.16 contains an integer overflow in the ICO loader that allows remote attackers to...
    📅 Updated: Nov 8, 2026
  • CVE-2026-123550CVSS 9.3
    OpenAM before 16.1.4 contains an authentication bypass vulnerability in its SAML v2.0 service provider that accepts unsigned assertions...
    📅 Updated: Nov 8, 2026
  • CVE-2026-123551CVSS 10.0
    OpenAM from 14.0.0 before 16.1.4 contains an information disclosure vulnerability that allows unauthenticated attackers to read live session...
    📅 Updated: Nov 8, 2026
  • CVE-2026-123549CVSS 9.3
    OpenAM before 16.1.4 fails to enforce the Valid Creation Attributes list during self-registration, allowing anonymous attackers to set...
    📅 Updated: Nov 8, 2026
  • CVE-2025-57085CVSS 9.8
    Tenda W30E V16.01.0.19 (5037) was discovered to contain a stack overflow in the v17 parameter in the UploadCfg...
    📅 Updated: Nov 8, 2026
  • CVE-2025-59359CVSS 9.8
    The cleanTcs mutation in Chaos Controller Manager is vulnerable to OS command injection. In conjunction with CVE-2025-59358, this...
    📅 Updated: Nov 8, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.