Skip to content
November 8, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
Insignary Launches Clarity On-Demand: SBOMs, No Annual Commitment Required Insignary_logo_full_1200x720_1_1784050762w8XHmBCjEL
  • Press Release

Insignary Launches Clarity On-Demand: SBOMs, No Annual Commitment Required

cybernewswire July 15, 2026 0
Toronto, Canada, 15th July 2026, CyberNewswire
Read More Read more about Insignary Launches Clarity On-Demand: SBOMs, No Annual Commitment Required
Four Critical Coolify Vulnerabilities Allow Remote Code Execution and Cross-Team Server Access Coolify vulnerabilities enabling remote code execution and cross-tenant server access in the self-hosted PaaS
  • Vulnerability Report

Four Critical Coolify Vulnerabilities Allow Remote Code Execution and Cross-Team Server Access

Do Son July 15, 2026 0

Four critical Coolify vulnerabilities let low-privileged users reach remote code execution and cross-tenant server access. Update to v4.1.2 now.

Seedream 5.0 Pro Photo Generator: Advancing AI-Assisted Visual Content Creation CVE-2024-31070 & CVE-2024-36491
  • Technique

Seedream 5.0 Pro Photo Generator: Advancing AI-Assisted Visual Content Creation

Do Son July 15, 2026 0
Introduction The increasing adoption of AI-enabled creative tools is a trend currently observed playing out in the...
Read More Read more about Seedream 5.0 Pro Photo Generator: Advancing AI-Assisted Visual Content Creation
Cursor Zero-Day Vulnerability Remains Unpatched After Seven Months Cursor zero day vulnerability exploitation diagram, AI coding assistant security threat analysis
  • Vulnerability Report

Cursor Zero-Day Vulnerability Remains Unpatched After Seven Months

Do Son July 15, 2026 0

A high-severity Cursor zero day vulnerability allows automatic remote code execution via malicious git.exe files. Read how this flaw remains unpatched.
Google Images Turns 25: AI Personalization and Nano Banana Generation Arrive in Search Google Images 25th anniversary AI redesign with Nano Banana image generation
  • Technology

Google Images Turns 25: AI Personalization and Nano Banana Generation Arrive in Search

Do Son July 15, 2026 0

The Google Images 25th anniversary update brings real-time personalized results and Nano Banana image generation built into AI Overviews.

CrySome RAT Spread Through Fake Freight Rate Confirmation Phishing NATS-as-C2 Sysdig CVE-2026-33017 Langflow RCE Microsoft Phone Link Hijack CloudZ Pheno Plugin Insider Threat BlackCat (ALPHV) OFAC Sanctions DPRK IT Workers Transparent Tribe APT36 React2Shell, EtherRAT SideWinder Espionage, Netlify Phishing DDNS Abuse, C2 Infrastructure Hacking Health Club
  • Malware

CrySome RAT Spread Through Fake Freight Rate Confirmation Phishing

Do Son July 15, 2026 0

A CrySome RAT phishing attack used a fake freight rate confirmation to bypass AMSI, disable Defender, and steal browser credentials on Windows.
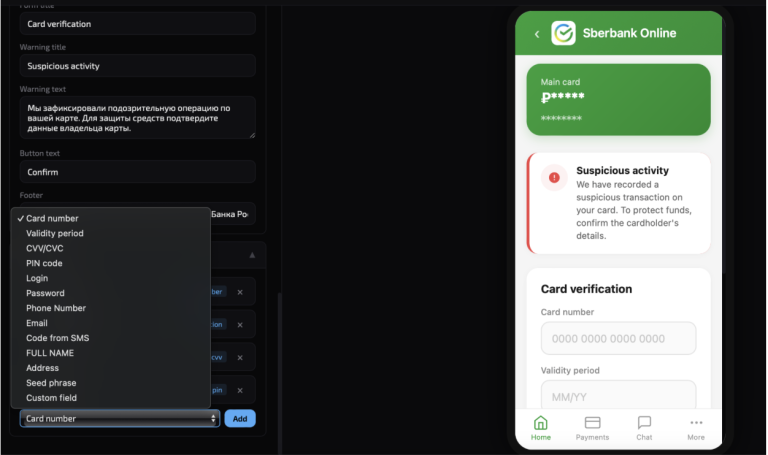
RedWing Android Malware Rents Out Spyware and Bank Theft on Telegram RedWing Android malware panel sold as malware-as-a-service on Telegram with banking overlays
  • Malware

RedWing Android Malware Rents Out Spyware and Bank Theft on Telegram

Do Son July 15, 2026 0

RedWing Android malware is a rental spyware sold as malware-as-a-service on Telegram. It steals banking logins, intercepts 2FA, and hijacks phones.
CVE-2026-10577: CVSS 10 Access Control Vulnerability Hits Rockwell Automation 1715 Redundant I/O Modules Rockwell Automation vulnerability CVE-2026-10577 access control flaw in 1715 Redundant I/O
  • Vulnerability Report

CVE-2026-10577: CVSS 10 Access Control Vulnerability Hits Rockwell Automation 1715 Redundant I/O Modules

Do Son July 15, 2026 0

Rockwell Automation vulnerability CVE-2026-10577 (CVSS 10) exposes an unauthenticated debug port in 1715 Redundant I/O modules. Update to firmware 3.011.
Malicious Go Module Exposes a 222-Repository GitHub Lure Network Malicious Go module exposing GitHub lure network of 222 repositories in Operation Muck and Load
  • Cybercriminals

Malicious Go Module Exposes a 222-Repository GitHub Lure Network

Do Son July 15, 2026 0

A malicious Go module exposed a GitHub lure network of 222 repositories, dubbed Operation Muck and Load, staging RATs and infostealers.

GodDamn Ransomware Rebrands Beast and Uses a Malicious Signed Driver to Disable Defenses North Korean hackers behind open-source supply chain attacks on axios, debug, and chalk NPM packages
  • Malware

GodDamn Ransomware Rebrands Beast and Uses a Malicious Signed Driver to Disable Defenses

Do Son July 15, 2026 0

GodDamn ransomware is the latest Beast ransomware rebrand from Hyadina. It uses a Microsoft-signed malicious kernel driver, PoisonX, to disable EDR.
Notepad++ v8.9.7 Fixes 5 Vulnerabilities, All With Public Details and PoC Exploit Code Notepad++ vulnerabilities public PoC exploit code path traversal CVE-2026-52886
  • Vulnerability Report

Notepad++ v8.9.7 Fixes 5 Vulnerabilities, All With Public Details and PoC Exploit Code

Do Son July 15, 2026 0

Notepad++ vulnerabilities now have public PoC exploit code. CVE-2026-52886, CVE-2026-54758, and CVE-2026-57233 are fixed in v8.9.7. Update now.
Chrome 150 Security Update Fixes 15 Flaws, Including Two Critical Use-After-Free Bugs Chrome security update 150 fixing critical use-after-free flaws CVE-2026-15764 and CVE-2026-15765
  • Vulnerability Report

Chrome 150 Security Update Fixes 15 Flaws, Including Two Critical Use-After-Free Bugs

Do Son July 15, 2026 0

Google's Chrome security update 150.0.7871.124 fixes 15 flaws, including critical use-after-free bugs CVE-2026-15764 and CVE-2026-15765. Update now.
Passkey Phishing Campaign Uses Vishing Calls to Hijack Microsoft Entra Accounts Passkey phishing vishing attack targeting Microsoft Entra passkey enrollment by O-UNC-066
  • Cybercriminals

Passkey Phishing Campaign Uses Vishing Calls to Hijack Microsoft Entra Accounts

Do Son July 15, 2026 0

A vishing attack tricks Microsoft 365 users into passkey phishing, letting O-UNC-066 enroll its own passkey and hijack Entra accounts for extortion.
CISA Warns Three SharePoint Server Vulnerabilities Are Exploited in the Wild, Urges Hardening CISA alert on SharePoint vulnerabilities exploited in the wild including CVE-2026-56164
  • Vulnerability Report

CISA Warns Three SharePoint Server Vulnerabilities Are Exploited in the Wild, Urges Hardening

Do Son July 15, 2026 0

CISA warns SharePoint vulnerabilities CVE-2026-32201, CVE-2026-45659, and CVE-2026-56164 are exploited in the wild. Patch and harden servers now.

Node.js Backdoor Hides Its C2 on the TON Blockchain Mercenary Akula European Financial Targeting AI-Generated Malware React2Shell Exploit UAT-8837 Critical Infrastructure Attack APT36, BOSS Linux BRICKSTORM Malware, China Espionage Curly COMrades, MucorAgent Chinese APT - HTTP Client Tools Shuckworm Cyber Espionage
  • Malware

Node.js Backdoor Hides Its C2 on the TON Blockchain

Do Son July 15, 2026 0

A LNK phishing attack drops a Node.js backdoor and hides its C2 on the TON blockchain using EtherHiding, LevelBlue reports.

CVE-2026-15409: SonicWall SMA1000 SSRF Vulnerability (CVSS 10.0) Exploited in the Wild SonicWall SMA1000 SSRF vulnerability CVE-2026-15409 and CVE-2026-15410
  • Vulnerability Report

CVE-2026-15409: SonicWall SMA1000 SSRF Vulnerability (CVSS 10.0) Exploited in the Wild

Do Son July 15, 2026 0

SonicWall SMA1000 SSRF flaw CVE-2026-15409 (CVSS 10.0) is exploited in the wild. Upgrade to hotfix 12.4.3-03453 or 12.5.0-02835 now.
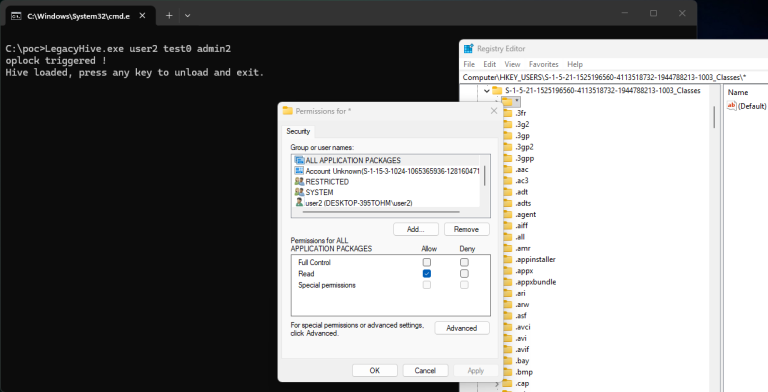
LegacyHive: Exploit Code and Full Details Publicly Disclosed for Unpatched Windows Privilege Escalation Flaw LegacyHive exploit public disclosure Windows privilege escalation flaw by Nightmare-Eclipse
  • Vulnerability Report

LegacyHive: Exploit Code and Full Details Publicly Disclosed for Unpatched Windows Privilege Escalation Flaw

Do Son July 14, 2026 0

LegacyHive exploit code is public. This unpatched Windows privilege escalation flaw from Nightmare-Eclipse defeats the July 2026 patch.

Microsoft July 2026 Patch Tuesday Fixes 570 Flaws, Two Zero-Days Exploited in the Wild Microsoft July 2026 Patch Tuesday zero-day vulnerabilities CVE-2026-56155 and CVE-2026-56164
  • Vulnerability Report

Microsoft July 2026 Patch Tuesday Fixes 570 Flaws, Two Zero-Days Exploited in the Wild

Do Son July 14, 2026 0

Microsoft's July 2026 Patch Tuesday fixes 570 flaws. Zero-days CVE-2026-56155 and CVE-2026-56164 are exploited in the wild. Patch now.

Tego AI Finds Claude Tag Slack Integration Can Trigger Unauthorized Enterprise Actions watermarked_img_2256307174777406298_1784021571yc2c34V8Fl
  • Press Release

Tego AI Finds Claude Tag Slack Integration Can Trigger Unauthorized Enterprise Actions

cybernewswire July 14, 2026 0
Tel Aviv, Israel, 14th July 2026, CyberNewswire
Read More Read more about Tego AI Finds Claude Tag Slack Integration Can Trigger Unauthorized Enterprise Actions
CVE-2026-53481 & CVE-2026-53483: Dell PowerProtect Full Takeover (9.8) Image showing a hacker taking complete control of system using CVE-2026-53483 and Dell vulnerabilities
  • Vulnerability Report

CVE-2026-53481 & CVE-2026-53483: Dell PowerProtect Full Takeover (9.8)

Do Son July 14, 2026 0

Critical Dell vulnerabilities like CVE-2026-53483 allow attackers to take complete control of system. Patch PowerProtect flaws to stop remote exploits.
Exploited in the Wild? Debian Webhost Rooted as Public PoCs Land for Bad Epoll (CVE-2026-46242) and IPv6 Frag Escape Bad Epoll CVE-2026-46242 Linux kernel privilege escalation use-after-free public PoC exploit
  • Vulnerability Report

Exploited in the Wild? Debian Webhost Rooted as Public PoCs Land for Bad Epoll (CVE-2026-46242) and IPv6 Frag Escape

Do Son July 14, 2026 0

A Debian webhost was rooted while missing fixes for Bad Epoll (CVE-2026-46242) and an IPv6 frag escape. Public PoC exploit code is now out.

CVE-2026-56000: Use-After-Free Flaw Hits X.Org Server and Xwayland X.Org Server use-after-free vulnerability CVE-2026-56000 patched in xorg-server 21.1.24
  • Vulnerability Report

CVE-2026-56000: Use-After-Free Flaw Hits X.Org Server and Xwayland

Do Son July 14, 2026 0

X.Org Server ships fixes for two flaws, including CVE-2026-56000, a CVSS 9.0 use-after-free. Update xorg-server and Xwayland now.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-18535CVSS 9.6
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 are vulnerable to a Regular Expression Denial of...
    📅 Updated: Nov 8, 2026
  • CVE-2026-17409CVSS 9.4
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote attacker to execute unauthorized...
    📅 Updated: Nov 8, 2026
  • CVE-2026-123614CVSS 9.3
    imgproxy from 4.0.0 before 4.0.16 contains an integer overflow in the ICO loader that allows remote attackers to...
    📅 Updated: Nov 8, 2026
  • CVE-2026-123550CVSS 9.3
    OpenAM before 16.1.4 contains an authentication bypass vulnerability in its SAML v2.0 service provider that accepts unsigned assertions...
    📅 Updated: Nov 8, 2026
  • CVE-2026-123551CVSS 10.0
    OpenAM from 14.0.0 before 16.1.4 contains an information disclosure vulnerability that allows unauthenticated attackers to read live session...
    📅 Updated: Nov 8, 2026
  • CVE-2026-123549CVSS 9.3
    OpenAM before 16.1.4 fails to enforce the Valid Creation Attributes list during self-registration, allowing anonymous attackers to set...
    📅 Updated: Nov 8, 2026
  • CVE-2025-57085CVSS 9.8
    Tenda W30E V16.01.0.19 (5037) was discovered to contain a stack overflow in the v17 parameter in the UploadCfg...
    📅 Updated: Nov 8, 2026
  • CVE-2025-59359CVSS 9.8
    The cleanTcs mutation in Chaos Controller Manager is vulnerable to OS command injection. In conjunction with CVE-2025-59358, this...
    📅 Updated: Nov 8, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.