 Do Son
PHP Composer patched three flaws, including CVE-2026-59948, an arbitrary file write that can run code outside your project. Update to 2.10.2 or 2.2.29.
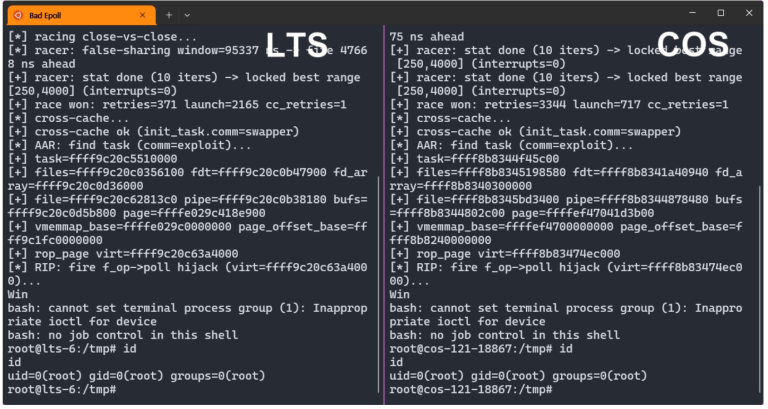
Bad Epoll (CVE-2026-46242) is a Linux kernel UAF enabling root privilege escalation. Full details and PoC exploit code are now public. Patch now.

An Anthropic API billing error mistakenly charged a Korean developer $16.6 million. Learn how this massive automated glitch froze his credit card.
VMware Avi Load Balancer Authentication Bypass (CVE-2026-47865, CVSS 9.8) Headlines Seven-Flaw Patch

VMware Avi Load Balancer Authentication Bypass (CVE-2026-47865, CVSS 9.8) Headlines Seven-Flaw Patch
VMware Avi Load Balancer patches CVE-2026-47865 (CVSS 9.8), a critical authentication bypass, plus six more flaws. Upgrade the Avi Controller now.

Explore the massive Meta Louisiana data center expansion. This $50 billion investment fuels local economic booms but ignites intense Wall Street anxiety.

Researcher @Cereblab confirms the Grok Build repository upload bypasses privacy mode; SpaceXAI's /privacy only covers code snippet sharing.

 cybernewswire
Vancouver, Canada, 14th July 2026, CyberNewswire

SAP Security Patch Day July 2026 fixes CVE-2026-44747 (CVSS 9.9), a memory corruption flaw in NetWeaver AS ABAP, plus two more critical bugs.

Discover how new prompt injection attacks threaten AI security. Hackers use prompt injection techniques to manipulate AI agents and bypass safety controls.
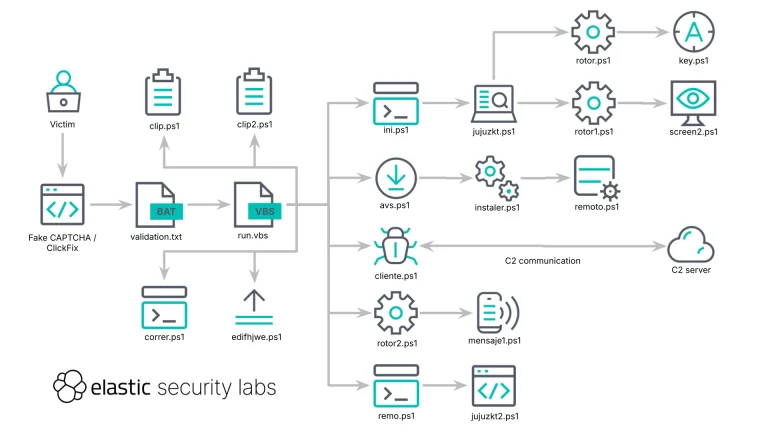
Discover how the REF6045 operation executes Mexican banking fraud. Hackers use fake CAPTCHAs and the SCMBANKER toolkit to steal financial data.
WinFsp vulnerabilities CVE-2026-3006 and CVE-2026-7162 enable local privilege escalation to SYSTEM on Windows. Update to WinFsp 2026 Beta2 now.

Discover the new Windows search box improvements in Windows 11. Learn how to disable Bing search distractions and prioritize local file search results.
The t.me domain is in serverHold status, taking down all Telegram contact and share links. Telegram falls back to telegram.me for new links.

Grok Build faces severe backlash over unauthorized repository data uploads. Learn how to opt out of data sharing and secure your sensitive code.
Netwrix Password Secure vulnerabilities (CVSS 9.9) allow authenticated remote code execution on the server. Update to version 26.6.100 now.

CVE-2026-6875 (CVSS 9.5) is a ServiceNow sandbox escape in the AI Platform allowing unauthenticated remote code execution. Patch to fixed releases now.
CVE-2026-53513 is a Better Auth SSRF flaw (CVSS 9.6) in the SSO plugin. It exposes cloud metadata and enables account takeover. Patch to 1.6.11 now.
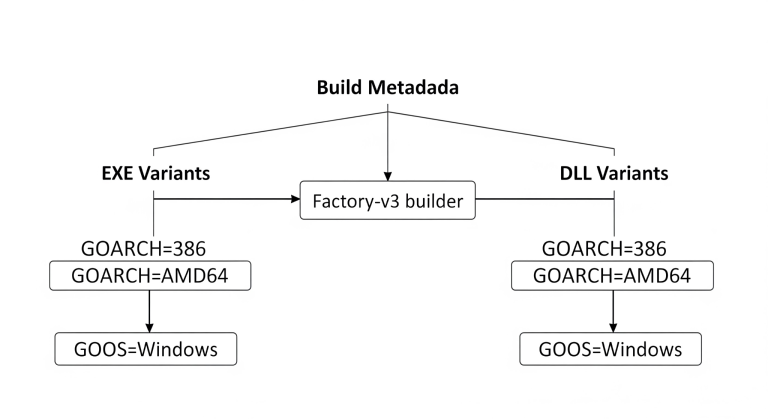
A new Vidar stealer campaign uses the Factory-v3 loader and fake certificates to deploy malware. Learn how attackers hide XMRig and bypass security.
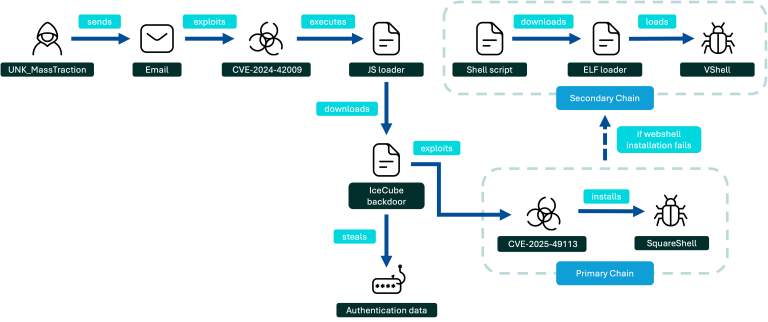
UNK_MassTraction, a suspected China-aligned actor, exploits Roundcube webmail flaws to steal credentials and deploy the VShell backdoor at universities.

Torrance, California, USA, 13th July 2026, CyberNewswire

UAT-7810, a China-nexus APT, grows its LapDogs ORB network with new router malware including LONGLEASH, DOGLEASH, and JARLEASH. Cisco Talos reports.
A critical privilege escalation flaw (CVE-2026-20744) affects Hydro-Québec EV charging stations. Learn how this vulnerability impacts the backend.