 Do Son
As cyber threats continue to evolve, attackers are increasingly targeting people rather than technology alone. Social engineering...
A massive ScreenConnect AsyncRAT campaign uses SEO poisoning and spoofed websites to drop malicious installer archives via remote monitoring tools.

Microsoft leverages advanced AI agents like MDASH to accelerate Windows vulnerability management and secure codebases.
A critical Veeam Backup vulnerability (CVE-2026-44963) allows remote code execution. Patch immediately to avoid ransomware targeting CVE-2023-27532.

StatCounter corrects flawed June 2026 data after reports falsely claimed Windows market share plunged to 56%. The anomaly stemmed from tracking errors.
A 20-nation alert warns that Russia's FSB Center 16 is hacking vulnerable routers. The group targets critical infrastructure through weak SNMP settings.
Australia's ACSC warns of a large-scale CMS exploitation campaign. Attackers exploit WordPress and CMS bugs to plant webshells on websites.

Suspected Iran-linked Cavern Manticore APT hackers deploy a new modular C2 framework to target Israeli government and IT sectors.

CVE-2026-4769 exposes WAGO System I/O field devices. An early-boot flaw lets an unauthenticated attacker reach full system compromise.
Suspected Armored Likho APT hackers deploy the new BusySnake Stealer to target government agencies and electric power sectors globally.
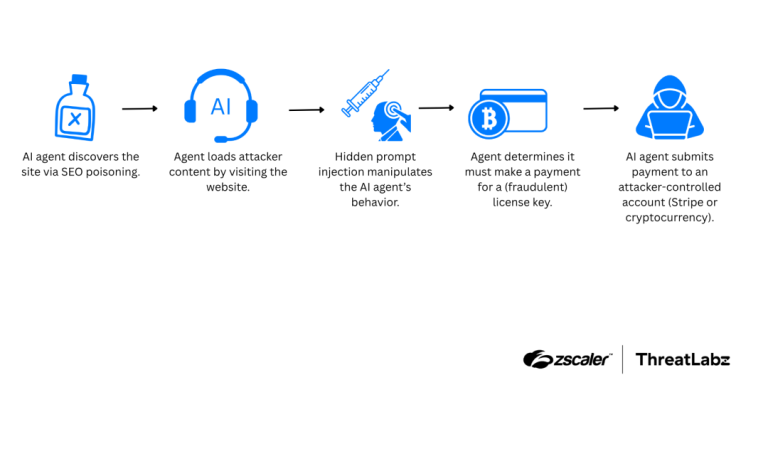
Indirect prompt injection exploits AI agent vulnerabilities through malicious web content. Attackers manipulate language models using hidden instructions.
Official SpaceX and Starlink X accounts were hijacked by a crypto scam ring to promote a fraudulent token amid the Musk-Altman feud.

Cursor is reportedly building a general-purpose AI agent to challenge Claude Cowork, expanding from coding into full computer control.

Our weekly CVE report: 1,571 new flaws and 6 actively exploited vulnerabilities hit CISA KEV, including ColdFusion and Joomla RCE.

Discover how the Mycelium Framework transforms infected machines into a malicious AI-as-a-Service botnet for distributed computing and automated exploits.
A new Apache Log4j flaw, CVE-2026-49844, makes log4j-api emit invalid JSON from non-finite numbers. Patch to 2.25.5 or 2.26.1 now.
A decompress npm vulnerability (CVE-2026-53486, CVSS 9.1) lets crafted archives write files outside the target folder via path traversal. Patch now.
75 CVEs confirmed exploited in Q2 2026. Microsoft leads with 15, Ivanti tops EPSS at 99%. Full breakdown by vendor, CWE, and publication-to-exploit gap.
Three Apache IoTDB vulnerabilities include a critical path traversal (CVE-2026-24014) and an authentication bypass. Upgrade to 2.0.8 now.

Silver Fox's Ghost distributor delivers MODBEACON, a modular Rust trojan, to picked targets in Operation Phnom Penh, per Qianxin. Here's what to know.
Four Apache Camel vulnerabilities allow header injection, server-side request forgery, secret disclosure, and an authentication bypass. Patch to 4.21.0 now.
CISA warns of a Gardyn IoT Hub flaw. CVE-2026-13768 (CVSS 10) enables unauthenticated remote code execution on smart garden devices. Update now.