 Do Son
Three FreeBSD privilege escalation flaws, including a kernel use-after-free, let local users gain root. Patch FreeBSD 14 and 15 now.
A Kafka authentication bypass lets attackers replay expired JWTs against 4.0.x brokers. The OAUTHBEARER path checks nbf but not exp. No fix yet.
 cybernewswire
London, United Kingdom, 10th July 2026, CyberNewswire
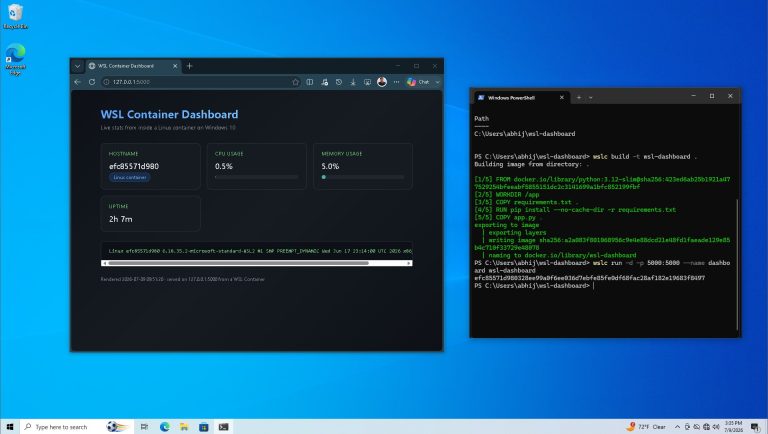
Microsoft confirms WSL Containers works on Windows 10 (Build 19041+) without Docker Desktop. Here's how to deploy it in six steps.
CVE-2026-13753 exposes a missing authorization vulnerability in HP Deskjet 2800 printers. Unauthenticated attackers can extract sensitive Wi-Fi credentials.
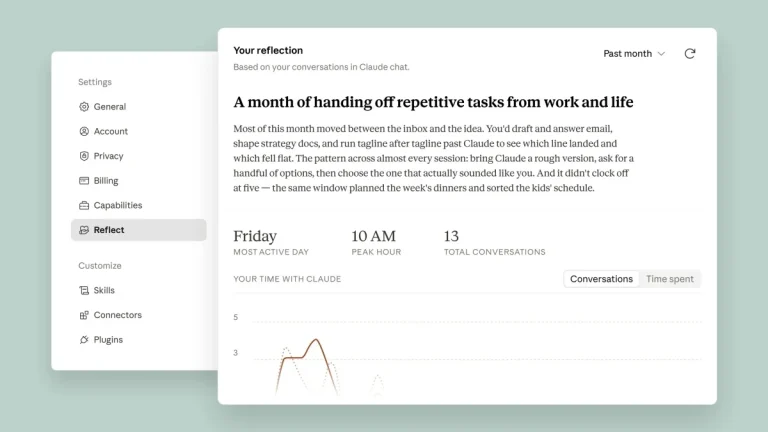
Discover the Claude Reflect dashboard. Anthropic's new digital health tool visualizes your AI usage, optimizes prompts, and promotes healthy collaboration.
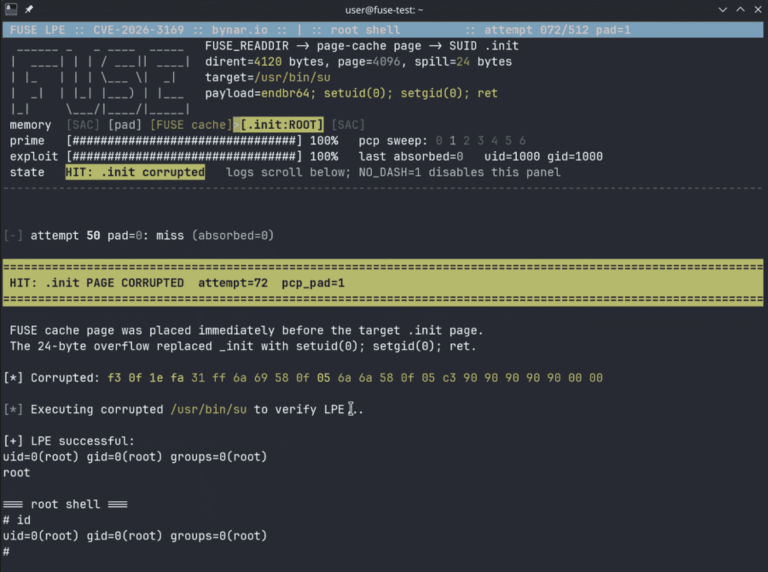
Public PoC and full details are out for CVE-2026-31694, a Linux kernel FUSE page cache overflow that gives local privilege escalation to root. Patch now.
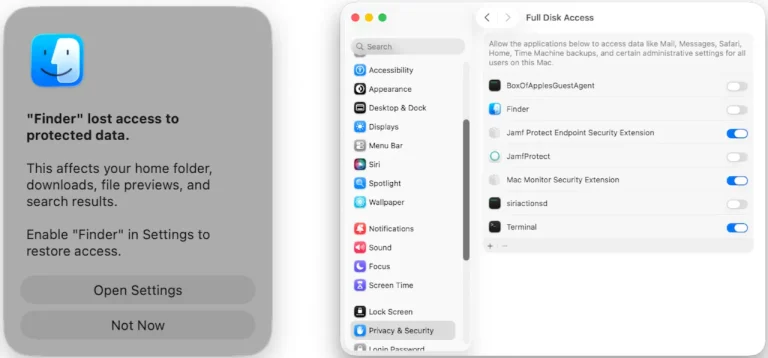
PamStealer macOS malware hides in a fake Maccy app and drops a Rust infostealer that checks your password via PAM before stealing it.
Four GNU Guix vulnerabilities in guix substitute and guix pull allow remote privilege escalation, file overwrite, and local file disclosure. Update now.
Sysdig documented JADEPUFFER, the first agentic ransomware run end-to-end by an AI agent. It breached Langflow via CVE-2025-3248 and extorted a database.
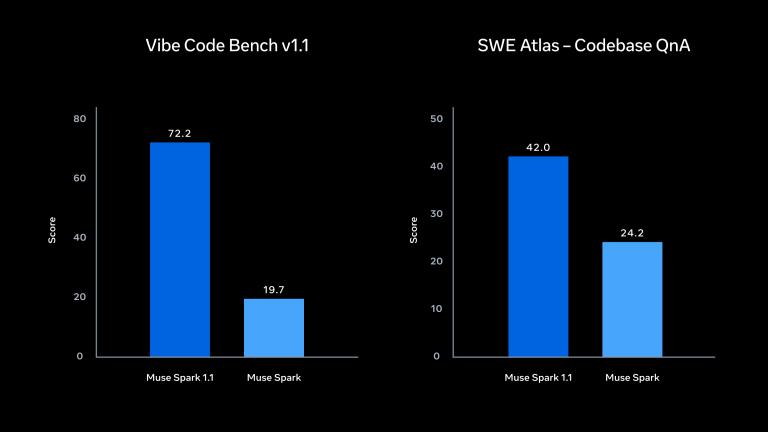
Meta introduces Muse Spark 1.1, a closed-source AI model built for complex agent tasks and programming. Discover its advanced capabilities and pricing.
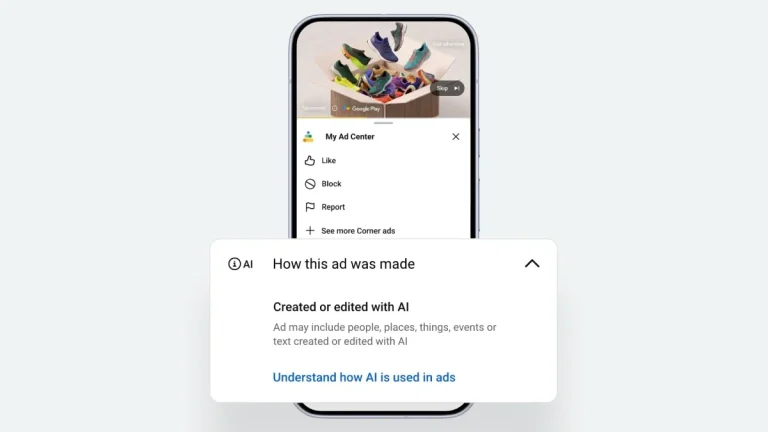
Google Ads AI transparency tools will soon label artificial content in My Ad Center. Discover how this update aims to protect consumer trust globally.
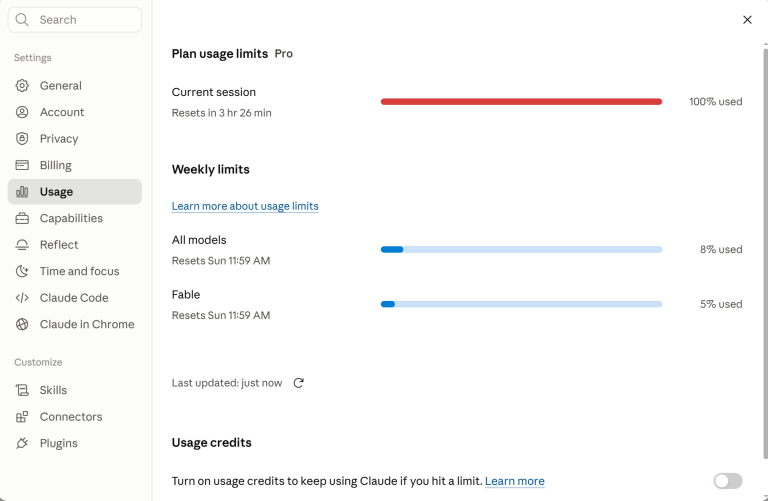
The recent Claude Code credit reset intensifies the AI race with OpenAI, allowing developers extended access to the powerful Claude Fable 5 model.
Cloudflare Drop offers free, rapid hosting for static websites with automatic global CDN acceleration. Claim your site for permanent access.
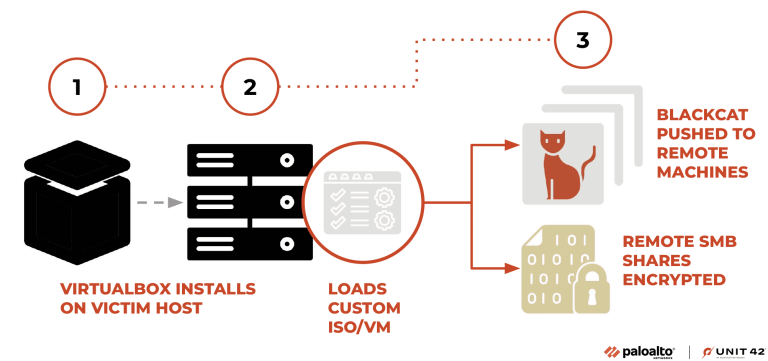
A Florida ransomware negotiator got 70 months for feeding clients' secrets to BlackCat ransomware actors. The DOJ seized over $10 million in proceeds.
CVE-2026-1207 is a Django SQL injection flaw (CVSS 8.3) in PostGIS raster lookups. Canada's CCCS says it is exploited in the wild. Patch now.

A Roundcube zero-click XSS, CVE-2026-54433, lets an email run script with no click. Roundcube 1.7.2 also fixes a second stored XSS. Update now.

Three Apache Lucene.NET vulnerability fixes land, including a Lucene.Net.Replicator path traversal flaw enabling unauthenticated file read. Patch now.
A critical Feast Feature Server flaw (CVE-2026-23537) lets unauthenticated attackers perform arbitrary file write and risk remote code execution. Act now.
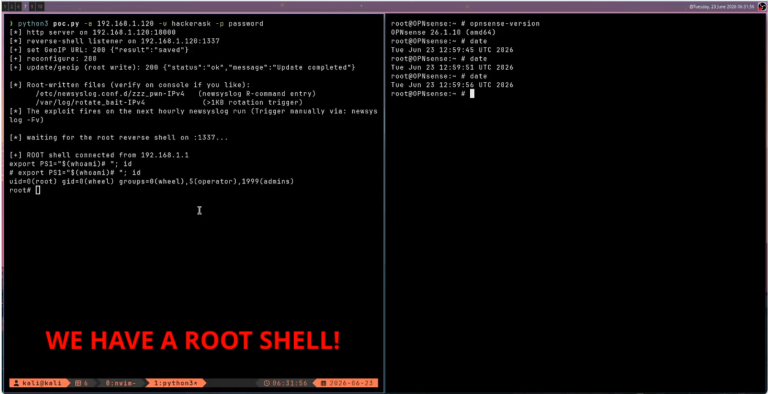
OPNsense root RCE flaws are public with PoC code. CVE-2026-57155 (9.9) chains an arbitrary file write to root. Patch 26.1.11 or 26.4.1p1 now.
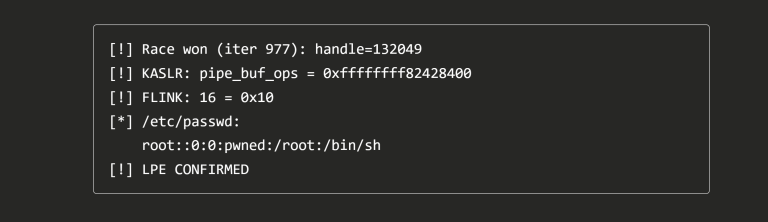
Public PoC and write-up detail a Linux kernel privilege escalation flaw (CVE-2026-46215) in DRM GEM. A local user gets root in ~99% of runs.
Progress patched three MOVEit Transfer flaws, including a stored XSS bug (CVE-2026-11903). No exploitation is confirmed. Update now.