Skip to content
November 8, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
Microsoft Patches RoguePlanet Defender Zero-Day That Grants SYSTEM Access Microsoft Defender zero-day RoguePlanet CVE-2026-50656 patched via Malware Protection Engine update
  • Vulnerability Report

Microsoft Patches RoguePlanet Defender Zero-Day That Grants SYSTEM Access

Do Son July 9, 2026 0

Microsoft patched the RoguePlanet Microsoft Defender zero-day, CVE-2026-50656, a race condition that grants SYSTEM privileges. A public PoC exists.

Chrome MV2 Extensions Removed from Web Store Aug 31 Chrome Web Store removing all Manifest V2 extensions on August 31 2026 affecting uBlock Origin and others
  • Technology

Chrome MV2 Extensions Removed from Web Store Aug 31

Do Son July 9, 2026 0

Google will remove all MV2 extensions from the Chrome Web Store on August 31, 2026. Back up your CRX files now before they are gone.

Google Photos Video Remix Uses Gemini Omni AI Google Photos Video Remix feature using Gemini Omni AI to apply filters and swap video backgrounds
  • Technology

Google Photos Video Remix Uses Gemini Omni AI

Do Son July 9, 2026 0

Google launches Video Remix in Google Photos, powered by Gemini Omni. Users can apply filters, swap backgrounds, and add avatars in seconds.
North Korea-Linked PolinRider Supply Chain Attack Expands Across Open Source PolinRider supply chain attack diagram showing North Korean hackers hiding loaders in open-source packages
  • Cybercriminals

North Korea-Linked PolinRider Supply Chain Attack Expands Across Open Source

Do Son July 9, 2026 0

Socket links the PolinRider supply chain attack to North Korean hackers. The campaign hid loaders in 108 open-source packages across four ecosystems.

KDDI Data Breach: Millions of Emails and Passwords Stolen KDDI data breach illustration, KDDI email leak security concept
  • Data Leak

KDDI Data Breach: Millions of Emails and Passwords Stolen

Do Son July 9, 2026 0

Discover the details of the recent KDDI data breach. Hackers stole over 12 million email addresses and millions of passwords. Learn how to protect yourself.

Rare Werewolf Phishing Campaign Targets Russian Aerospace With AnyDesk WhatsApp Worm, Brazilian Banking Trojan LAPSUS$ Alliance, Scattered Spider Ransomware, Cybercrime RedCurl APT group Russian Cyberespionage, ApolloShadow Malware
  • Cybercriminals

Rare Werewolf Phishing Campaign Targets Russian Aerospace With AnyDesk

Do Son July 9, 2026 0

Seqrite ties a Rare Werewolf phishing campaign to Russian aerospace firms, using a fake invoice to plant AnyDesk for stealthy remote access.
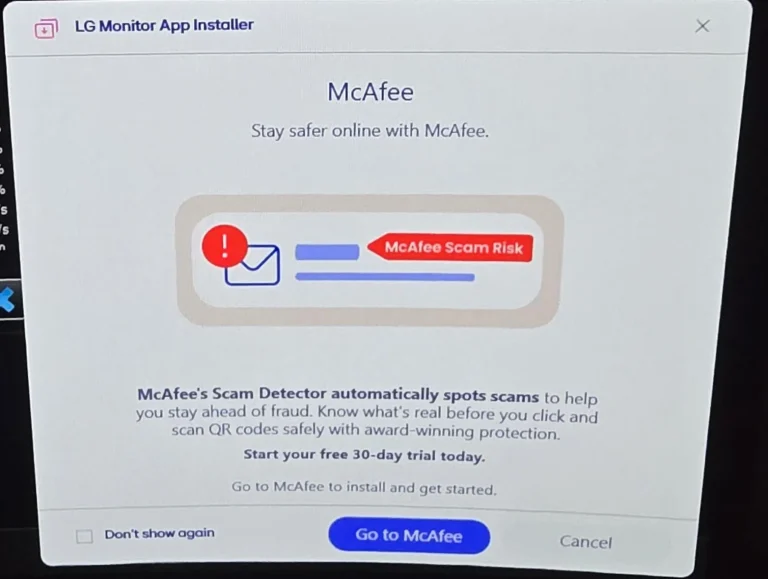
Hidden LG Monitor Adware: Stop Unwanted Pop-ups Now LG monitor adware warning showing unwanted McAfee pop-ups and bloatware installation
  • Malware

Hidden LG Monitor Adware: Stop Unwanted Pop-ups Now

Do Son July 9, 2026 0

Discover how hidden LG monitor adware automatically installs unwanted McAfee pop-ups on your PC. Learn how to stop this intrusive bloatware today.

HPLIP Vulnerability CVE-2026-14544 (CVSS 9.8) Allows Arbitrary Code Execution HPLIP vulnerability advisory graphic showing CVE-2026-14544 arbitrary code execution via crafted print data
  • Vulnerability Report

HPLIP Vulnerability CVE-2026-14544 (CVSS 9.8) Allows Arbitrary Code Execution

Do Son July 9, 2026 0

A critical HPLIP vulnerability, CVE-2026-14544 (CVSS 9.8), lets a remote attacker gain arbitrary code execution via crafted print data. Patch now.

DuckDuckGo Blocks YouTube Ads by Default on All Platforms DuckDuckGo browser blocking YouTube video ads by default using uBlock Origin community filter lists
  • Technology

DuckDuckGo Blocks YouTube Ads by Default on All Platforms

Do Son July 9, 2026 0

DuckDuckGo browser now blocks YouTube video ads by default on iOS, Windows, and Mac, using uBlock Origin filters as Chrome's MV3 limits rival tools.

LineageOS Browser Flash Tool Makes ROM Install Easier LineageOS browser-based flashing tool using WebUSB ADB Fastboot for custom Android ROM installation
  • Android

LineageOS Browser Flash Tool Makes ROM Install Easier

Do Son July 9, 2026 0

LineageOS launches a browser-based flashing tool via WebUSB, a redesigned updater showing patch levels, and streaming A/B OTA updates.
GitLab Patch Release Fixes Eight Flaws, Including a High-Severity XSS Bug (CVE-2026-6896) GitLab patch release fixing cross-site scripting vulnerability CVE-2026-6896 in version 19.1.2
  • Vulnerability Report

GitLab Patch Release Fixes Eight Flaws, Including a High-Severity XSS Bug (CVE-2026-6896)

Do Son July 9, 2026 0

The GitLab patch release fixes 8 flaws, including a high-severity cross-site scripting bug (CVE-2026-6896). Update to 19.1.2 now.

CVE-2026-0288: PAN-OS Buffer Overflow Can Execute Arbitrary Code PAN-OS buffer overflow CVE-2026-0288 enabling arbitrary code execution on Palo Alto firewall
  • Vulnerability Report

CVE-2026-0288: PAN-OS Buffer Overflow Can Execute Arbitrary Code

Do Son July 9, 2026 0

A PAN-OS buffer overflow, CVE-2026-0288, enables arbitrary code execution on Palo Alto firewalls. Patch now.

Chrome Security Update Patches 27 Flaws, Including Two Critical Use-After-Free Bugs Chrome security update patching critical use-after-free vulnerabilities in version 150.0.7871.114
  • Vulnerability Report

Chrome Security Update Patches 27 Flaws, Including Two Critical Use-After-Free Bugs

Do Son July 9, 2026 0

Google's latest Chrome security update fixes 27 flaws, including two critical use-after-free bugs. Update to 150.0.7871.114 now.

Foxit PDF Reader Flaws Enable Arbitrary Code Execution Foxit PDF Reader arbitrary code execution vulnerability patched in version 2026.1.2
  • Vulnerability Report

Foxit PDF Reader Flaws Enable Arbitrary Code Execution

Do Son July 8, 2026 0

Foxit fixed 28 flaws in Foxit PDF Reader and PDF Editor. Twenty allow arbitrary code execution via crafted PDFs. Update to 2026.1.2 now.

OpenSSH 10.4 Ships Eight Security Fixes for SSH Clients and Servers OpenSSH 10.4 security fixes including a client use-after-free and SFTP SCP path flaws
  • Vulnerability Report

OpenSSH 10.4 Ships Eight Security Fixes for SSH Clients and Servers

Do Son July 8, 2026 0

OpenSSH 10.4 ships eight security fixes, including a client use-after-free (CVE-2026-60002) plus SFTP and SCP path bugs. Update now.

Ghost Cache Poisoning Flaw Lets Attackers Hijack Staff Accounts Ghost cache poisoning XSS via x-ghost-preview header advisory graphic
  • Vulnerability Report

Ghost Cache Poisoning Flaw Lets Attackers Hijack Staff Accounts

Do Son July 8, 2026 0

A critical Ghost cache poisoning bug lets an unauthenticated x-ghost-preview header hijack staff accounts. Update to Ghost v6.37.0 now.
Network UPS Tools RCE Flaw Affects upsmon, With No Patch Yet Network UPS Tools RCE advisory showing upsmon command injection via ups.alarm
  • Vulnerability Report

Network UPS Tools RCE Flaw Affects upsmon, With No Patch Yet

Do Son July 8, 2026 0

A Network UPS Tools RCE (CVE-2026-54161) lets a malicious upsd trigger upsmon command injection as root. No patch exists yet, so mitigate now.

pretix Patches Two Critical Session Takeover and SSRF Flaws pretix vulnerabilities advisory showing the session takeover and SSRF fix
  • Vulnerability Report

pretix Patches Two Critical Session Takeover and SSRF Flaws

Do Son July 8, 2026 0

New pretix vulnerabilities include a critical session takeover chain (CVE-2026-13602) and an SSRF API key leak. Update to 2026.5.3 now.

OpenMatter Network Joins HOL Initiative to Help Define Standards for Verifiable AI Collaboration and Security Untitled_17_x_9_in_1782765623hTY1a9UzBA_1783448292rI4BiJQv9d
  • Press Release

OpenMatter Network Joins HOL Initiative to Help Define Standards for Verifiable AI Collaboration and Security

cybernewswire July 8, 2026 0
Melbourne, Florida, United States, 8th July 2026, CyberNewswire
Read More Read more about OpenMatter Network Joins HOL Initiative to Help Define Standards for Verifiable AI Collaboration and Security
Apache APISIX JWT Authentication Bypass, CVE-2026-39999 APISIX authentication bypass via JWT algorithm confusion, CVE-2026-39999
  • Vulnerability Report

Apache APISIX JWT Authentication Bypass, CVE-2026-39999

Do Son July 8, 2026 0

APISIX authentication bypass CVE-2026-39999 lets attackers forge JWTs via algorithm confusion. APISIX 3.16.0 is affected; upgrade to 3.16.1.

Claude Fable 5 Extension: Free Access Extended Claude Fable 5 extension announcement and API pricing details
  • Technology

Claude Fable 5 Extension: Free Access Extended

Do Son July 8, 2026 0

Anthropic extends the Claude Fable 5 complimentary window until July 12. Discover the 50% quota limit and upcoming transition to the Usage Credits system.

Google Voice Introduces Premium Paid Plans Google Voice paid plans subscription tiers and AI transcription features
  • Technology

Google Voice Introduces Premium Paid Plans

Do Son July 8, 2026 0

Google Voice introduced premium personal paid plans starting at $10 monthly. Discover new features like number retention and AI call transcription today.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-18535CVSS 9.6
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 are vulnerable to a Regular Expression Denial of...
    📅 Updated: Nov 8, 2026
  • CVE-2026-17409CVSS 9.4
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote attacker to execute unauthorized...
    📅 Updated: Nov 8, 2026
  • CVE-2026-123614CVSS 9.3
    imgproxy from 4.0.0 before 4.0.16 contains an integer overflow in the ICO loader that allows remote attackers to...
    📅 Updated: Nov 8, 2026
  • CVE-2026-123550CVSS 9.3
    OpenAM before 16.1.4 contains an authentication bypass vulnerability in its SAML v2.0 service provider that accepts unsigned assertions...
    📅 Updated: Nov 8, 2026
  • CVE-2026-123551CVSS 10.0
    OpenAM from 14.0.0 before 16.1.4 contains an information disclosure vulnerability that allows unauthenticated attackers to read live session...
    📅 Updated: Nov 8, 2026
  • CVE-2026-123549CVSS 9.3
    OpenAM before 16.1.4 fails to enforce the Valid Creation Attributes list during self-registration, allowing anonymous attackers to set...
    📅 Updated: Nov 8, 2026
  • CVE-2025-57085CVSS 9.8
    Tenda W30E V16.01.0.19 (5037) was discovered to contain a stack overflow in the v17 parameter in the UploadCfg...
    📅 Updated: Nov 8, 2026
  • CVE-2025-59359CVSS 9.8
    The cleanTcs mutation in Chaos Controller Manager is vulnerable to OS command injection. In conjunction with CVE-2025-59358, this...
    📅 Updated: Nov 8, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.