Skip to content
November 8, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
Android Remote Root Exploit Chain Unveiled by Nebula Android remote root exploit chain PoC by Nebula
  • Vulnerability Report

Android Remote Root Exploit Chain Unveiled by Nebula

Do Son July 8, 2026 0

Nebula reveals a severe Android remote root exploit chain combining a Firefox vulnerability and a 15-year-old Linux kernel flaw.

SpaceXAI Grok 4.5 Launch: Global Public Release Set SpaceXAI Grok 4.5 launch and V9 foundation model metrics
  • Technology

SpaceXAI Grok 4.5 Launch: Global Public Release Set

Do Son July 8, 2026 0

SpaceXAI Grok 4.5 launch brings Claude Opus-tier intelligence with superior speed and efficiency to the global public.

OpenAI GPT-5.6 Rollout: Global Access Approved OpenAI GPT-5.6 rollout featuring Sol, Terra, and Luna models
  • Technology

OpenAI GPT-5.6 Rollout: Global Access Approved

Do Son July 8, 2026 0

The US government has approved the broad OpenAI GPT-5.6 rollout. Discover pricing, features, and release details for Sol, Terra, and Luna.
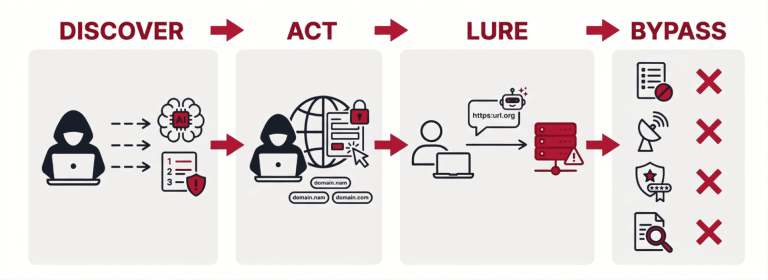
Phantom Squatting Attacks Weaponize AI Hallucinated Domains, Unit 42 Warns Phantom squatting attacker registering AI hallucinated domains predicted by LLM chatbots
  • Cybercriminals

Phantom Squatting Attacks Weaponize AI Hallucinated Domains, Unit 42 Warns

Do Son July 8, 2026 0

Unit 42 warns phantom squatting attacks weaponize AI hallucinated domains, with 13,229 malicious URLs and 250,000 fake domains open to registration.
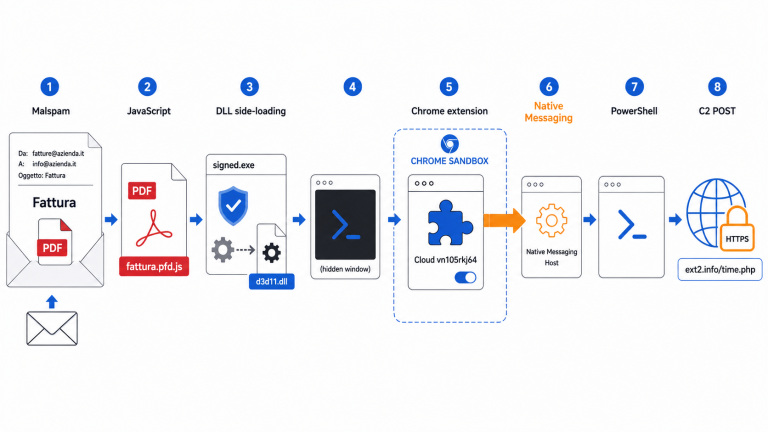
Native Messaging Backdoor Turns a Chrome Extension Into a Windows Threat Native Messaging backdoor malicious Chrome extension PowerShell Windows infection chain diagram
  • Malware

Native Messaging Backdoor Turns a Chrome Extension Into a Windows Threat

Do Son July 8, 2026 0

A Native Messaging backdoor pairs a malicious Chrome extension with a local host to run PowerShell, escaping the browser sandbox, says D3Lab.

Ubuntu 25.10 End of Life: Prepare Your Upgrade Ubuntu 25.10 end of life warning and upgrade to Ubuntu 26.04 LTS screen
  • Linux

Ubuntu 25.10 End of Life: Prepare Your Upgrade

Do Son July 8, 2026 0

Ubuntu 25.10 end of life is July 9, 2026. Upgrade your system to Ubuntu 26.04 LTS today to maintain crucial security updates and system stability.

The FCC’s Rollback of Broadband Transparency Rules Broadband Consumer Labels transparency rule
  • Technology

The FCC’s Rollback of Broadband Transparency Rules

Do Son July 8, 2026 0

The FCC plans to roll back Broadband Consumer Labels, allowing ISPs to hide junk fees and reducing transparency for everyday internet users.
Veil#Drop Malware Uses Blogspot to Deliver PureLog Stealer China influence operations using banned ChatGPT accounts in OpenAI's June 2026 threat report targeting the US AI policy debate
  • Malware

Veil#Drop Malware Uses Blogspot to Deliver PureLog Stealer

Do Son July 8, 2026 0

Veil#Drop malware abuses Blogspot to run PowerShell loaders and deploy PureLog Stealer in memory, dodging antivirus and file-based detection.

WordPress Sites at Risk: Outdated PHP, Plugins, and Default Configs WordPress outdated PHP end-of-life security risk chart showing plugin and PHP version gaps
  • Vulnerability Report

WordPress Sites at Risk: Outdated PHP, Plugins, and Default Configs

Do Son July 8, 2026 0

Censys research finds 70% of WordPress sites run end-of-life PHP. Outdated plugins and defaults leave millions of sites wide open to attack.
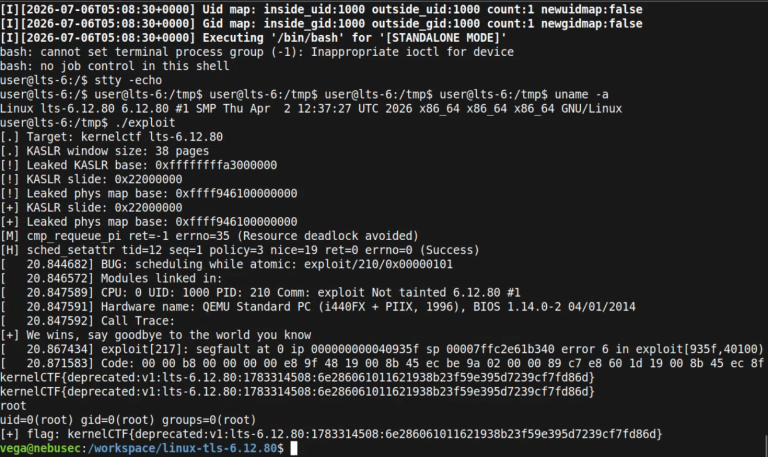
Public Exploit for GhostLock (CVE-2026-43499) Enables Linux Privilege Escalation and Container Escape GhostLock CVE-2026-43499 Linux kernel privilege escalation and container escape exploit chain
  • Vulnerability Report

Public Exploit for GhostLock (CVE-2026-43499) Enables Linux Privilege Escalation and Container Escape

Do Son July 8, 2026 0

Researchers disclosed GhostLock (CVE-2026-43499) with public PoC code. The 15-year Linux kernel bug enables privilege escalation and container escape.
CISA Adds Four Actively Exploited Flaws to Its KEV Catalog CISA KEV Catalog update listing four actively exploited Joomla Langflow and Adobe ColdFusion vulnerabilities
  • Vulnerability Report

CISA Adds Four Actively Exploited Flaws to Its KEV Catalog

Do Son July 8, 2026 0

CISA added four actively exploited flaws to its KEV Catalog, including critical Joomla, Langflow, and ColdFusion bugs. Agencies must patch by July 10.
Control-M CVE-2026-10539: Unauthenticated Remote Command Injection (CVSS 9.5) Control-M command injection vulnerability CVE-2026-10539 enabling unauthenticated remote command injection on the server
  • Vulnerability Report

Control-M CVE-2026-10539: Unauthenticated Remote Command Injection (CVSS 9.5)

Do Son July 7, 2026 0

BMC patches Control-M command injection flaw CVE-2026-10539, an unauthenticated remote command injection bug rated CVSS 9.5.

SharePoint Remote Code Execution Flaw CVE-2026-33112: Details and PoC Public SharePoint remote code execution CVE-2026-33112 XmlValidator bypass proof-of-concept diagram
  • Vulnerability Report

SharePoint Remote Code Execution Flaw CVE-2026-33112: Details and PoC Public

Do Son July 7, 2026 0

A SharePoint remote code execution flaw (CVE-2026-33112) is now public with full details and PoC. A low-privilege user can run code. Patch now.
Ubiquiti UniFi Security Advisory 066 Fixes 25 Vulnerabilities UniFi security advisory 066 covering 25 vulnerabilities including command injection
  • Vulnerability Report

Ubiquiti UniFi Security Advisory 066 Fixes 25 Vulnerabilities

Do Son July 7, 2026 0

Ubiquiti's UniFi security advisory 066 patches 25 flaws, including a critical command injection (CVE-2026-50746) scoring 10.0. Update your devices now.

Google Updates Android Backup Storage Policy Limits Android backup storage policy warning on a smartphone screen
  • Android

Google Updates Android Backup Storage Policy Limits

Do Son July 7, 2026 0

Discover how Google's new Android backup storage policy impacts your free cloud capacity. Learn to manage your data and avoid unexpected subscription costs.

SpaceXAI: Elon Musk’s Orbital Data Centers Vision SpaceXAI logo and orbital data centers concept in space
  • Technology

SpaceXAI: Elon Musk’s Orbital Data Centers Vision

Do Son July 7, 2026 0

Five months after merging his AI and space ventures, Elon Musk reveals SpaceXAI. Discover how the $2.1 trillion giant plans to build orbital data centers.
ARToken Phishing Platform Steals Microsoft 365 Tokens and Bypasses MFA phsi
  • Cybercriminals

ARToken Phishing Platform Steals Microsoft 365 Tokens and Bypasses MFA

Do Son July 7, 2026 0

Cisco Talos exposes ARToken, a phishing platform using device code phishing to steal Microsoft 365 tokens and bypass MFA.
Critical IBM Power HMC Vulnerability Exposes Systems IBM Power HMC vulnerability OS command injection diagram
  • Vulnerability Report

Critical IBM Power HMC Vulnerability Exposes Systems

Do Son July 7, 2026 0

A critical IBM Power HMC vulnerability (CVE-2026-12943) allows unauthenticated attackers to execute commands. Patch your systems immediately.
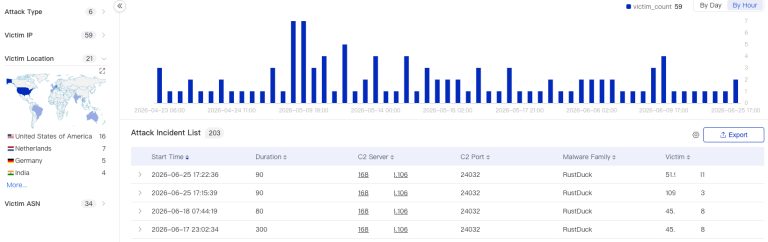
RustDuck Botnet: A Two-Stage DDoS Threat Shifting From C to Rust RustDuck botnet two-stage DDoS malware loader core architecture analysis diagram
  • Malware

RustDuck Botnet: A Two-Stage DDoS Threat Shifting From C to Rust

Do Son July 7, 2026 0

The RustDuck botnet is a fast-evolving two-stage DDoS threat moving from C to Rust, with encrypted C2 and heavy anti-analysis, per XLab.

Windows 11 Cloud Rebuild: Reinstall Without USB Windows Recycle Bin bug showing an internal $Rxxxxx filename in the delete confirmation dialog after the June 2026 update
  • Windows

Windows 11 Cloud Rebuild: Reinstall Without USB

Do Son July 7, 2026 0

Microsoft tests Windows 11 cloud rebuild in WinRE, letting users reinstall via the internet without USB drives when the system fails to boot.
Linux Kernel Vulnerability CVE-2024-26582: Public PoC Reaches Root Shell Linux kernel vulnerability CVE-2024-26582 TLS use-after-free root shell exploit diagram
  • Vulnerability

Linux Kernel Vulnerability CVE-2024-26582: Public PoC Reaches Root Shell

Do Son July 7, 2026 0

A Linux kernel vulnerability (CVE-2024-26582) has a public PoC that turns a TLS use-after-free into a root shell. Details and exploit are out.
DeepSeek AI Generates Browser Native Ransomware GMO Internet ransom demand diagram illustrating cloud security misconfiguration and breach leak
  • Cybercriminals

DeepSeek AI Generates Browser Native Ransomware

Do Son July 7, 2026 0

Discover how AI generated malware from DeepSeek turns hallucinated ideas into real browser native ransomware using the File System Access API.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-18535CVSS 9.6
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 are vulnerable to a Regular Expression Denial of...
    📅 Updated: Nov 8, 2026
  • CVE-2026-17409CVSS 9.4
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote attacker to execute unauthorized...
    📅 Updated: Nov 8, 2026
  • CVE-2026-123614CVSS 9.3
    imgproxy from 4.0.0 before 4.0.16 contains an integer overflow in the ICO loader that allows remote attackers to...
    📅 Updated: Nov 8, 2026
  • CVE-2026-123550CVSS 9.3
    OpenAM before 16.1.4 contains an authentication bypass vulnerability in its SAML v2.0 service provider that accepts unsigned assertions...
    📅 Updated: Nov 8, 2026
  • CVE-2026-123551CVSS 10.0
    OpenAM from 14.0.0 before 16.1.4 contains an information disclosure vulnerability that allows unauthenticated attackers to read live session...
    📅 Updated: Nov 8, 2026
  • CVE-2026-123549CVSS 9.3
    OpenAM before 16.1.4 fails to enforce the Valid Creation Attributes list during self-registration, allowing anonymous attackers to set...
    📅 Updated: Nov 8, 2026
  • CVE-2025-57085CVSS 9.8
    Tenda W30E V16.01.0.19 (5037) was discovered to contain a stack overflow in the v17 parameter in the UploadCfg...
    📅 Updated: Nov 8, 2026
  • CVE-2025-59359CVSS 9.8
    The cleanTcs mutation in Chaos Controller Manager is vulnerable to OS command injection. In conjunction with CVE-2025-59358, this...
    📅 Updated: Nov 8, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.