
 Do Son
Citrix NetScaler vulnerability CVE-2026-8451 is exploited in the wild after a public PoC exposed a pre-auth memory overread. Patch now.

Apache HttpComponents Core vulnerabilities CVE-2026-54399 and CVE-2026-54428 allow remote denial of service through memory exhaustion. Upgrade now.

Microsoft found a fake Perplexity AI extension that hijacks browser search and logs keystrokes. Google pulled the malicious Chrome extension.

Cloudflare Monetization Gateway uses the x402 protocol to charge AI tools and agents for pulling data from protected web resources.

Google launches Gemini Spark on macOS for AI Ultra subscribers. Discover how this $100 agentic AI assistant automates local files and Workspace tasks.

A GNU gzip vulnerability (CVE-2026-41991) lets a local attacker overwrite files through a gzexe symlink attack. Update to the patched gzip release now.

Mustang Panda targets India's government and hydropower sectors, abusing Zoho WorkDrive for C2. Acronis found new ZOHOMURK and MINIRECON implants.

Kaspersky details The Gentlemen ransomware, a fast-growing RaaS group with new Go and C lockers, EDR killers, and worldwide victims. Here's how it works.
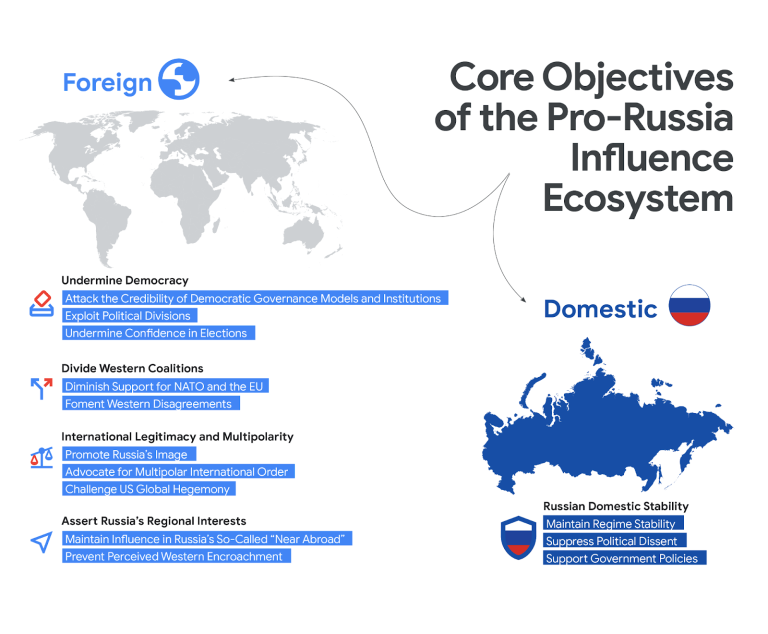
The pro-Russia influence ecosystem is expanding information operations beyond Ukraine. Discover how global targets face new cyber threats and AI tactics.
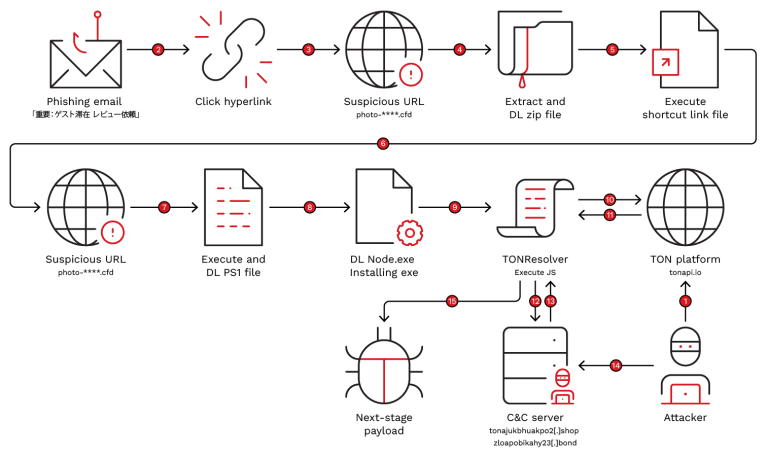
Trend Micro found TONResolver malware hitting Booking.com hotel partners in Japan. It hides its C2 in a TON blockchain smart contract. Details inside.

A critical IBM Db2 RCE flaw (CVE-2026-10109) allows pre-auth code execution. IBM patched it plus two other Db2 bugs. Update 11.5 and 12.1 now.

CISA flags an actively exploited SharePoint vulnerability (CVE-2026-45659) enabling remote code execution. Patch SharePoint Server 2016 now.
Following a Scattered Spider arrest, Peter Stokes faces extradition to the US for his alleged role in a $100M cyber extortion and hacking scheme.

Cisco fixes a Cisco Catalyst Center vulnerability (CVE-2026-20191, CVSS 7.5) and seven ClamAV vulnerabilities causing DoS in Secure Endpoint Connectors.
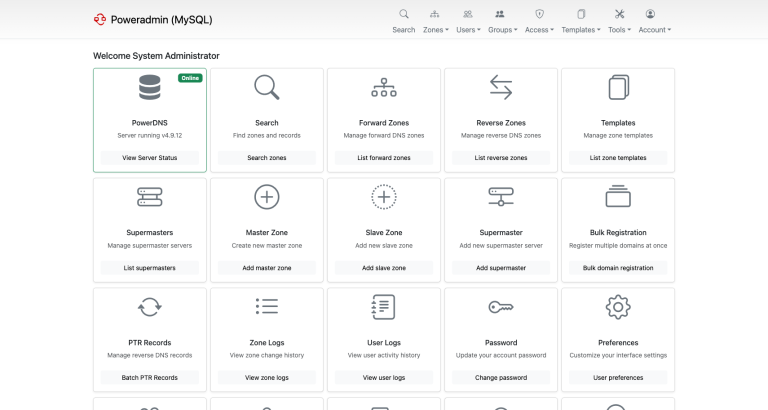
A critical Poweradmin host header injection flaw (CVE-2026-54588) lets attackers hijack DNS admin accounts. Update to 4.2.4 or 4.3.3 now.

A critical OpenAM WebAuthn RCE flaw (CVE-2026-45051) allows code execution via Java deserialization. Update OpenAM to 16.1.1 to stay protected.

A NetComm authentication bypass (CVE-2026-35019, CVSS 9.2) uses a hardcoded AES key to forge admin session cookies. Update to firmware R6B032 now.
A WinRAR vulnerability (CVE-2026-14191) causes a heap overflow via crafted .rev recovery files. Update WinRAR and UnRAR to version 7.23 now.

JetBrains patched a CVSS 10 authentication bypass and two more flaws (CVE-2026-50242). Its tools reach 15M developers. Update JetBrains Hub now.
 Shahid Latif
Sometimes, a story lasts for hours, but many viewers prefer only a short highlight. Therefore, turning a...
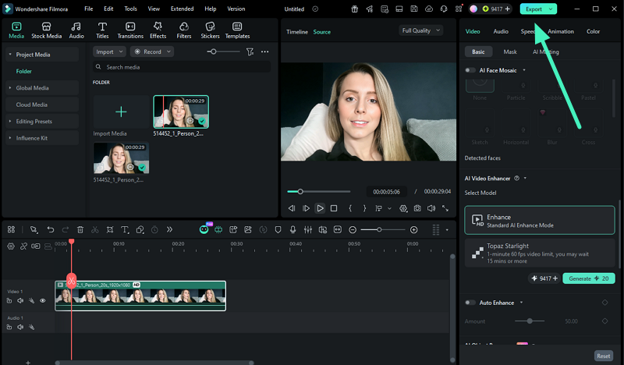
A content creator opens an old project file, only to find blurry footage and pixelated clips that...

Walk through any city center, industrial park, or large residential complex today, and you’ll likely notice tall,...