Skip to content
November 8, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
NVIDIA Security Updates Fix Critical Device Vulnerabilities NVIDIA security updates for ConnectX mitigating CVE-2025-23351
  • Vulnerability Report

NVIDIA Security Updates Fix Critical Device Vulnerabilities

Do Son July 1, 2026 0

Recent NVIDIA security updates address critical vulnerabilities, including CVE-2025-23351. Apply patches to secure your ConnectX and BlueField devices.
Kemp LoadMaster RCE Vulnerability Exploited in the Wild After Public PoC Release Kemp LoadMaster RCE vulnerability CVE-2026-8037 warning graphic
  • Vulnerability Report

Kemp LoadMaster RCE Vulnerability Exploited in the Wild After Public PoC Release

Do Son July 1, 2026 0

Attackers now target the Kemp LoadMaster RCE vulnerability (CVE-2026-8037) using a public PoC. Patch to 7.2.63.2 or 7.2.54.18 immediately.

Turning Indicators into Intelligence in OpenCTI with Criminal IP OpenClaw_Part_II_The_Growing_Security_Risks_Behind_1782355030QoWU2e1jD5
  • Press Release

Turning Indicators into Intelligence in OpenCTI with Criminal IP

cybernewswire July 1, 2026 0
Torrance, California, USA, 1st July 2026, CyberNewswire
Read More Read more about Turning Indicators into Intelligence in OpenCTI with Criminal IP
Mitigating Attacks Before They Impact Infrastructure: Link11 provides next generation network DDoS protection 04_NetworkDDoS_1782900896ZXxW8F2biG
  • Press Release

Mitigating Attacks Before They Impact Infrastructure: Link11 provides next generation network DDoS protection

cybernewswire July 1, 2026 0
Frankfurt am Main, Deutschland, 1st July 2026, CyberNewswire
Read More Read more about Mitigating Attacks Before They Impact Infrastructure: Link11 provides next generation network DDoS protection
Android 17 Rate Limiting Blocks PIN Guessing Android 17 rate limiting PIN lockout screen Google I/O 2026 highlights
  • Android

Android 17 Rate Limiting Blocks PIN Guessing

Do Son July 1, 2026 0

Android 17 rate limiting drastically cuts PIN attempts, making stolen phones far harder to unlock by guesswork.

Anthropic Overcomes Export Restrictions: Mythos and Fable Models Restored Anthropic AI export ban lifted for Mythos and Fable models
  • Technology

Anthropic Overcomes Export Restrictions: Mythos and Fable Models Restored

Do Son July 1, 2026 0

The US Commerce Department lifts the Anthropic AI export ban, restoring access to Mythos and Fable models after sweeping national security compromises.
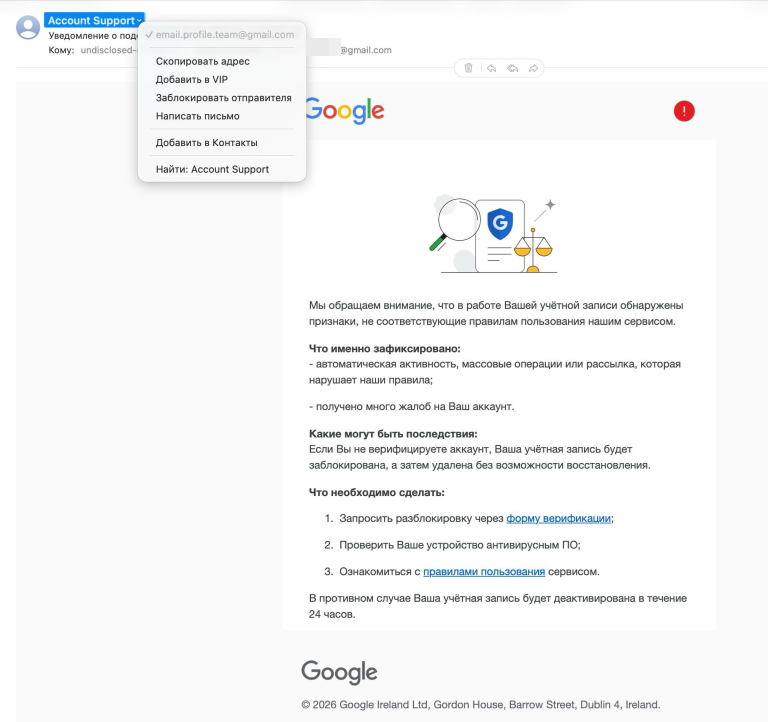
UNC1151 Phishing Campaign Targets Belarus and Ukraine UNC1151 phishing campaign login page created by the Ghostwriter threat actor.
  • Cybercriminals

UNC1151 Phishing Campaign Targets Belarus and Ukraine

Do Son July 1, 2026 0

A suspected UNC1151 phishing campaign targets Belarusian politicians and Ukrainian portals to steal credentials using deceptive login pages.

Claude Code Telemetry Rollback: Anthropic Responds to Backdoor Allegations Anthropic Claude Code telemetry rollback response and developer community controversy Claude Code human error Claude AI Data Wipe, Constraining AI Tools Anthropic lawsuit, AI copyright Claude Code, web editor
  • Technology

Claude Code Telemetry Rollback: Anthropic Responds to Backdoor Allegations

Do Son July 1, 2026 0

Anthropic announces a Claude Code telemetry rollback following intense developer backlash over hidden location tracking and proxy detection code.

Anthropic Unveils Claude Sonnet 5 for Efficient Agentic AI Anthropic Claude Sonnet 5 release focusing on enterprise Agentic AI cost efficiency
  • Technology

Anthropic Unveils Claude Sonnet 5 for Efficient Agentic AI

Do Son July 1, 2026 0

Anthropic announces the Claude Sonnet 5 release, featuring a highly efficient tokenizer for affordable Agentic AI workflows and reduced API costs.

Operation DragonReturn Targets Indian Tax Infrastructure WhatsApp Worm, Brazilian Banking Trojan LAPSUS$ Alliance, Scattered Spider Ransomware, Cybercrime RedCurl APT group Russian Cyberespionage, ApolloShadow Malware
  • Cybercriminals

Operation DragonReturn Targets Indian Tax Infrastructure

Do Son July 1, 2026 0

Operation DragonReturn is a suspected China-nexus cyber espionage campaign targeting India's tax infrastructure using deceptive phishing emails and DcRAT.
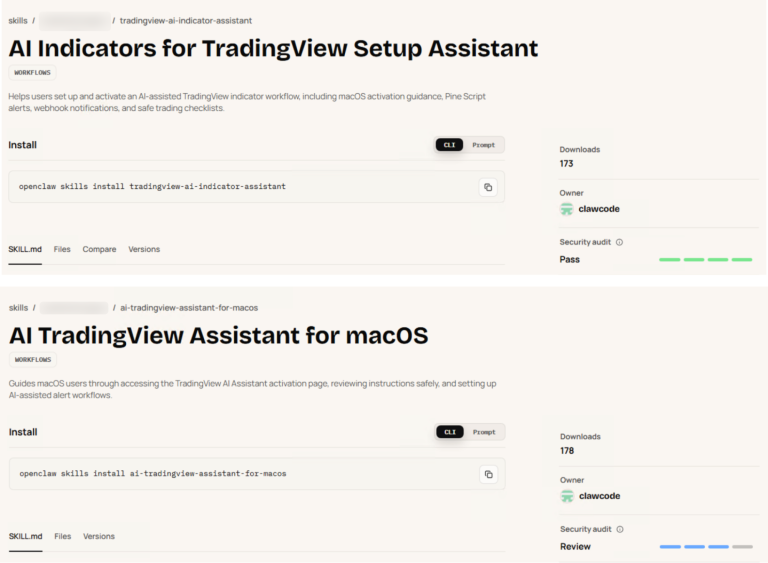
Malicious OpenClaw Skills on ClawHub Deliver Infostealers and Crypto Fraud Malicious OpenClaw skills on the ClawHub marketplace enabling an AI supply chain attack
  • Malware

Malicious OpenClaw Skills on ClawHub Deliver Infostealers and Crypto Fraud

Do Son July 1, 2026 0

Unit 42 found five malicious OpenClaw skills on ClawHub that bypassed scanners. The AI supply chain attack delivered infostealers and crypto fraud.

Gmail Live Beta Brings Voice Search to Your Inbox Gmail Live beta voice search interface on Android and iOS letting users find emails by talking to Gemini
  • Technology

Gmail Live Beta Brings Voice Search to Your Inbox

Do Son July 1, 2026 0

Gmail Live is now in beta on Android and iOS, letting you search your inbox by voice with Gemini. Here's how the feature works and who gets it.

Claude Code Spyware Controversy: Secret Location Tracking Exposed Claude Cowork quota update Claude Desktop native messaging bridge Anthropic Opus 4.5 Claude Excel Integration
  • Technology

Claude Code Spyware Controversy: Secret Location Tracking Exposed

Do Son July 1, 2026 0

A Reddit user discovered hidden spyware in Claude Code that tracks users' locations, particularly targeting Chinese developers and proxy usage. Read more.

Apache Tomcat Vulnerabilities Allow Authentication Bypass Apache Tomcat vulnerabilities including an authentication bypass via JNDIRealm GSSAPI bind (CVE-2026-55957)
  • Vulnerability Report

Apache Tomcat Vulnerabilities Allow Authentication Bypass

Do Son July 1, 2026 0

Seven Apache Tomcat vulnerabilities are patched, including an authentication bypass (CVE-2026-55957). Update to a fixed Tomcat release now.

Chrome Security Update Patches 382 Vulnerabilities, 15 Critical Chrome security update patching 382 vulnerabilities including 15 critical use-after-free flaws
  • Vulnerability Report

Chrome Security Update Patches 382 Vulnerabilities, 15 Critical

Do Son July 1, 2026 0

The latest Chrome security update patches 382 vulnerabilities, including 15 critical use-after-free flaws. Update Chrome now to stay protected.

Six Critical Incus Vulnerabilities Patched in v7.2.0 Incus vulnerabilities CVE-2026-48769 CVE-2026-48755 root file write security update
  • Vulnerability Report

Six Critical Incus Vulnerabilities Patched in v7.2.0

Do Son July 1, 2026 0

Six Incus vulnerabilities, all rated CVSS 9.9, are fixed in v7.2.0. CVE-2026-48769 and CVE-2026-48755 enable root attacks. Update now.

Ten GeoVision Camera Vulnerabilities Hit GV-LPC License Plate Models GeoVision camera vulnerabilities CVE-2026-57878 GV-LPC2011 GV-LPC2211 firmware V1.13 security advisory
  • Vulnerability Report

Ten GeoVision Camera Vulnerabilities Hit GV-LPC License Plate Models

Do Son July 1, 2026 0

Ten GeoVision camera vulnerabilities hit GV-LPC2011/2211 models, four rated CVSS 9.8 (CVE-2026-57878). Update to firmware V1.13 now.

Fluentd Vulnerabilities Patched in v1.19.3, Including Critical RCE Fluentd vulnerabilities CVE-2026-44024 RCE CVE-2026-44161 SSRF security patch v1.19.3
  • Vulnerability Report

Fluentd Vulnerabilities Patched in v1.19.3, Including Critical RCE

Do Son July 1, 2026 0

Four Fluentd vulnerabilities are fixed in v1.19.3, including a 9.8 RCE (CVE-2026-44024) and SSRF (CVE-2026-44161). Patch now.
ProFTPD ACL Bypass Flaw Exposes Files in Restricted Directories ProFTPD ACL bypass vulnerability CVE-2026-35025 access control bypass in RNFR command
  • Vulnerability Report

ProFTPD ACL Bypass Flaw Exposes Files in Restricted Directories

Do Son July 1, 2026 0

A ProFTPD ACL bypass (CVE-2026-35025, CVSS 8.6) lets logged-in FTP users reach files in restricted directories. No patch is out yet; use DefaultRoot.

Plone Fixes Critical RCE Flaw and Two Denial-of-Service Bugs Plone RCE vulnerability via TALES injection in the Classic portlet
  • Vulnerability Report

Plone Fixes Critical RCE Flaw and Two Denial-of-Service Bugs

Do Son July 1, 2026 0

A critical Plone RCE vulnerability (CVE-2026-57149, CVSS 9.9) allows TALES injection via the Classic portlet. Two more flaws enable DoS and SSRF.

Adobe ColdFusion Vulnerabilities Reach CVSS 10 With Arbitrary Code Execution Adobe ColdFusion vulnerabilities enabling arbitrary code execution with CVSS 10 scores (APSB26-68)
  • Vulnerability Report

Adobe ColdFusion Vulnerabilities Reach CVSS 10 With Arbitrary Code Execution

Do Son June 30, 2026 0

Eleven Adobe ColdFusion vulnerabilities include six CVSS 10 arbitrary code execution flaws. Patch ColdFusion 2025 and 2023 now.

Six NetScaler Vulnerabilities Allow Denial of Service and File Read NetScaler vulnerabilities causing denial of service, memory overread, and unauthenticated file read on NetScaler ADC and Gateway
  • Vulnerability Report

Six NetScaler Vulnerabilities Allow Denial of Service and File Read

Do Son June 30, 2026 0

Six NetScaler vulnerabilities allow denial of service, memory overreads, and an unauthenticated file read. Patch NetScaler ADC and Gateway now.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-18535CVSS 9.6
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 are vulnerable to a Regular Expression Denial of...
    📅 Updated: Nov 8, 2026
  • CVE-2026-17409CVSS 9.4
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote attacker to execute unauthorized...
    📅 Updated: Nov 8, 2026
  • CVE-2026-123614CVSS 9.3
    imgproxy from 4.0.0 before 4.0.16 contains an integer overflow in the ICO loader that allows remote attackers to...
    📅 Updated: Nov 8, 2026
  • CVE-2026-123550CVSS 9.3
    OpenAM before 16.1.4 contains an authentication bypass vulnerability in its SAML v2.0 service provider that accepts unsigned assertions...
    📅 Updated: Nov 8, 2026
  • CVE-2026-123551CVSS 10.0
    OpenAM from 14.0.0 before 16.1.4 contains an information disclosure vulnerability that allows unauthenticated attackers to read live session...
    📅 Updated: Nov 8, 2026
  • CVE-2026-123549CVSS 9.3
    OpenAM before 16.1.4 fails to enforce the Valid Creation Attributes list during self-registration, allowing anonymous attackers to set...
    📅 Updated: Nov 8, 2026
  • CVE-2025-57085CVSS 9.8
    Tenda W30E V16.01.0.19 (5037) was discovered to contain a stack overflow in the v17 parameter in the UploadCfg...
    📅 Updated: Nov 8, 2026
  • CVE-2025-59359CVSS 9.8
    The cleanTcs mutation in Chaos Controller Manager is vulnerable to OS command injection. In conjunction with CVE-2025-59358, this...
    📅 Updated: Nov 8, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.