Skip to content
November 8, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
Six NetScaler Vulnerabilities Allow Denial of Service and File Read NetScaler vulnerabilities causing denial of service, memory overread, and unauthenticated file read on NetScaler ADC and Gateway
  • Vulnerability Report

Six NetScaler Vulnerabilities Allow Denial of Service and File Read

Do Son June 30, 2026 0

Six NetScaler vulnerabilities allow denial of service, memory overreads, and an unauthenticated file read. Patch NetScaler ADC and Gateway now.

NDSS Symposium Heads to Seoul in 2027 to Expand Global Cybersecurity Collaboration ndss
  • Press Release

NDSS Symposium Heads to Seoul in 2027 to Expand Global Cybersecurity Collaboration

cybernewswire June 30, 2026 0
DC, United States, June 30th, 2026, CyberNewswire The Internet Society today announced that 2027 Network and Distributed System...
Read More Read more about NDSS Symposium Heads to Seoul in 2027 to Expand Global Cybersecurity Collaboration
Reflectiz to Host Webinar, Joined by Taboola, on Securing Third-Party Marketing in the AI Era tab
  • Press Release

Reflectiz to Host Webinar, Joined by Taboola, on Securing Third-Party Marketing in the AI Era

cybernewswire June 30, 2026 0
Boston, Massachusetts, June 30th, 2026, CyberNewswire Reflectiz, the web exposure management platform, today announced a live webinar...
Read More Read more about Reflectiz to Host Webinar, Joined by Taboola, on Securing Third-Party Marketing in the AI Era
OpenMatter Network Introduces Verifiable Trust Layer for Secure Collaboration and AI Agents Untitled_17_x_9_in_1782765623hTY1a9UzBA
  • Press Release

OpenMatter Network Introduces Verifiable Trust Layer for Secure Collaboration and AI Agents

cybernewswire June 30, 2026 0
Melbourne, Florida, June 30th, 2026, CyberNewswire OpenMatter Network today announced the launch of its cryptographically verifiable platform for...
Read More Read more about OpenMatter Network Introduces Verifiable Trust Layer for Secure Collaboration and AI Agents
AppViewX Launches Global Partner Program Amid Rising Demand for Machine and Agent Identity Security app
  • Press Release

AppViewX Launches Global Partner Program Amid Rising Demand for Machine and Agent Identity Security

cybernewswire June 30, 2026 0
New York, United States, June 30th, 2026, CyberNewswire Building on the momentum of its Agent Identity Security...
Read More Read more about AppViewX Launches Global Partner Program Amid Rising Demand for Machine and Agent Identity Security
NLnet Labs Patches Four Critical NSD Vulnerabilities NSD DNS vulnerabilities and CVE-2026-12244
  • Vulnerability Report

NLnet Labs Patches Four Critical NSD Vulnerabilities

Do Son June 30, 2026 0

NLnet Labs patched critical NSD DNS vulnerabilities, including CVE-2026-12244. Update now to protect your multi-tenant secondary DNS deployments.

Thousands Affected by NVIDIA 9.8 Auth Bypass NVIDIA security updates fixing CVE-2026-24270, CVE-2026-24260, and CVE-2026-24264
  • Vulnerability Report

Thousands Affected by NVIDIA 9.8 Auth Bypass

Do Son June 30, 2026 0

NVIDIA security updates patch a critical 9.8 CVSS authentication bypass in AIStore, plus severe flaws in Triton and Container Toolkit impacting thousands.
INC Ransomware Targets Mainframes in APAC Campaign INC ransomware targets mainframes using cross-platform ransomware payloads
  • Malware

INC Ransomware Targets Mainframes in APAC Campaign

Do Son June 30, 2026 0

INC ransomware targets mainframes using cross-platform ransomware payloads. Attackers expose a new campaign hitting APAC manufacturing and food companies.

Claude Fable 5 Requires Separate Credits and Strict ID Checks Claude Fable 5 credit purchase and identity verification UI leak
  • Technology

Claude Fable 5 Requires Separate Credits and Strict ID Checks

Do Son June 30, 2026 0

Anthropic's upcoming Claude Fable 5 model may require separate credit purchases and strict government ID verification, according to newly leaked app strings.

Gemini Personalized Images Now Free for US Users Gemini personalized images created free with Nano Banana and Google Photos showing the user's real face and life details
  • Technology

Gemini Personalized Images Now Free for US Users

Do Son June 30, 2026 0

Gemini personalized images are now free for eligible US users, using Nano Banana and Google Photos to create AI pictures that look like you.

Hospitality Malware Campaign Deploys Node.js Implant North Korean hackers behind open-source supply chain attacks on axios, debug, and chalk NPM packages
  • Cybercriminals

Hospitality Malware Campaign Deploys Node.js Implant

Do Son June 30, 2026 0

An active hospitality malware campaign uses photo lures and authentication laundering to infect hotel networks with a persistent Node.js implant.
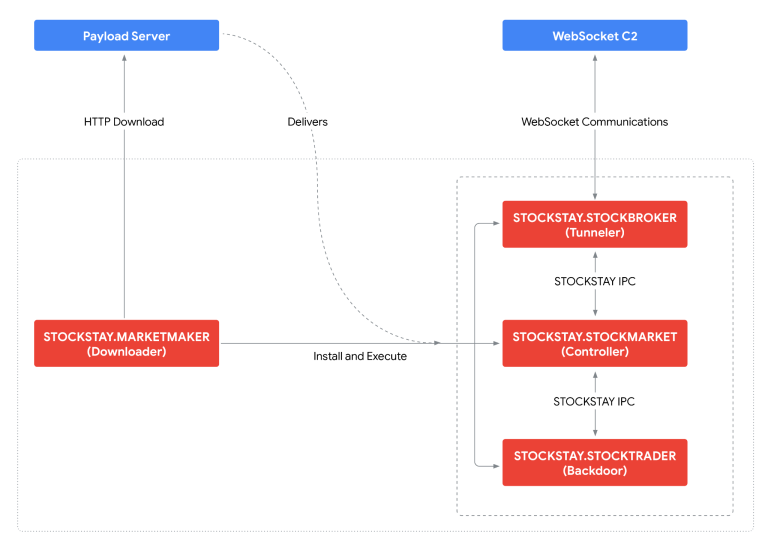
Turla STOCKSTAY Backdoor Targets Ukrainian Military Turla STOCKSTAY backdoor attacks Ukrainian military targets
  • Malware

Turla STOCKSTAY Backdoor Targets Ukrainian Military

Do Son June 30, 2026 0

Turla STOCKSTAY backdoor attacks Ukrainian military targets. Russian cyber espionage groups deploy this .NET malware via malicious RDP and WinRAR flaws.

TinyRCT Backdoor Attacks Target Asian Critical Infrastructure North Korean hackers behind open-source supply chain attacks on axios, debug, and chalk NPM packages
  • Cybercriminals

TinyRCT Backdoor Attacks Target Asian Critical Infrastructure

Do Son June 30, 2026 0

Chinese-speaking actors deploy TinyRCT backdoor attacks against Southeast Asian government and energy sectors. Discover the CL-STA-1062 cyber espionage tactics.

OpenClaw Brings Agentic AI to iOS and Android Phones OpenClaw app bringing agentic AI to iOS and Android with deep device permissions for an AI agent assistant
  • Technology

OpenClaw Brings Agentic AI to iOS and Android Phones

Do Son June 30, 2026 0

The OpenClaw app brings agentic AI to iOS and Android, letting an AI agent access your camera, screen, contacts, calendar, and more.
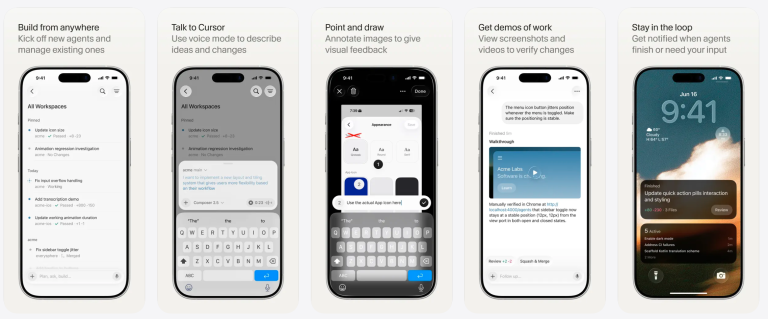
Cursor iOS Beta App Brings Remote AI Coding to Mobile Cursor iOS beta app interface for remote AI coding
  • Malware

Cursor iOS Beta App Brings Remote AI Coding to Mobile

Do Son June 30, 2026 0

Discover the new Cursor iOS beta app. This remote AI coding tool lets developers manage agents, review code, and merge pull requests directly from mobile.
iPhone 18 Pro Secrets Leaked in Tata Electronics Breach iPhone 18 Pro leak from the Tata Electronics data breach exposing Apple supplier lists, components, and drop-test photos RCS End-to-End Encryption
  • Data Leak

iPhone 18 Pro Secrets Leaked in Tata Electronics Breach

Do Son June 30, 2026 0

An iPhone 18 Pro leak from the Tata Electronics breach exposes supplier lists, component details, and device photos on the dark web.

WhatsApp Usernames Let You Hide Your Phone Number WhatsApp usernames privacy feature letting users connect without sharing a phone number, with reservations open now
  • Technology

WhatsApp Usernames Let You Hide Your Phone Number

Do Son June 30, 2026 0

WhatsApp usernames let you chat without sharing your phone number. Reservations open this week ahead of the full launch later this year.

WSO2 API Manager Hit by CVSS 10 Auth Bypass and Six More Flaws WSO2 API Manager vulnerabilities CVE-2026-5430 CVSS 10 JWT authentication bypass security advisory
  • Vulnerability Report

WSO2 API Manager Hit by CVSS 10 Auth Bypass and Six More Flaws

Do Son June 30, 2026 0

WSO2 patched seven flaws across API Manager and gateways, led by a CVSS 10 JWT auth bypass (CVE-2026-5430). Update WSO2 API Manager now.

Synology MailPlus Server Patched for CVSS 10 Flaw CVE-2026-13136 Synology MailPlus Server vulnerability CVE-2026-13136 CVSS 10 security advisory
  • Vulnerability Report

Synology MailPlus Server Patched for CVSS 10 Flaw CVE-2026-13136

Do Son June 30, 2026 0

Synology MailPlus Server has three new flaws, including CVE-2026-13136 at CVSS 10. Update to 4.0.1-31663 now. No exploit confirmed.
SimpleHelp Authentication Bypass Exploited in the Wild to Deploy TaskWeaver and Djinn Stealer hacked
  • Vulnerability Report

SimpleHelp Authentication Bypass Exploited in the Wild to Deploy TaskWeaver and Djinn Stealer

Do Son June 30, 2026 0

CVE-2026-48558, a SimpleHelp authentication bypass, is exploited in the wild to deploy TaskWeaver and Djinn Stealer. CISA added it to KEV. Patch now.
Critical wolfSSL Security Vulnerabilities Expose IoT Systems Diagram explaining wolfSSL security vulnerabilities and X.509 trust-chain bypass.
  • Vulnerability Report

Critical wolfSSL Security Vulnerabilities Expose IoT Systems

Do Son June 30, 2026 0

Developers patched six severe wolfSSL security vulnerabilities, including an X.509 trust-chain bypass. Update embedded systems to protect against exploits.

EVoke Systems Vulnerabilities Expose Charging Stations EVoke Systems vulnerabilities and charging station security
  • Vulnerability Report

EVoke Systems Vulnerabilities Expose Charging Stations

Do Son June 30, 2026 0

Critical EVoke Systems vulnerabilities expose charging stations to unauthorized access and DoS attacks. Update security profiles to mitigate these risks.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-18535CVSS 9.6
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 are vulnerable to a Regular Expression Denial of...
    📅 Updated: Nov 8, 2026
  • CVE-2026-17409CVSS 9.4
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote attacker to execute unauthorized...
    📅 Updated: Nov 8, 2026
  • CVE-2026-123614CVSS 9.3
    imgproxy from 4.0.0 before 4.0.16 contains an integer overflow in the ICO loader that allows remote attackers to...
    📅 Updated: Nov 8, 2026
  • CVE-2026-123550CVSS 9.3
    OpenAM before 16.1.4 contains an authentication bypass vulnerability in its SAML v2.0 service provider that accepts unsigned assertions...
    📅 Updated: Nov 8, 2026
  • CVE-2026-123551CVSS 10.0
    OpenAM from 14.0.0 before 16.1.4 contains an information disclosure vulnerability that allows unauthenticated attackers to read live session...
    📅 Updated: Nov 8, 2026
  • CVE-2026-123549CVSS 9.3
    OpenAM before 16.1.4 fails to enforce the Valid Creation Attributes list during self-registration, allowing anonymous attackers to set...
    📅 Updated: Nov 8, 2026
  • CVE-2025-57085CVSS 9.8
    Tenda W30E V16.01.0.19 (5037) was discovered to contain a stack overflow in the v17 parameter in the UploadCfg...
    📅 Updated: Nov 8, 2026
  • CVE-2025-59359CVSS 9.8
    The cleanTcs mutation in Chaos Controller Manager is vulnerable to OS command injection. In conjunction with CVE-2025-59358, this...
    📅 Updated: Nov 8, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.