Skip to content
November 3, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
Google Search Now Saves Your Uploaded Media to Train AI Google Search Save Media setting saving uploaded images and audio in Search Services History to train AI models
  • Technology

Google Search Now Saves Your Uploaded Media to Train AI

Do Son June 24, 2026 0

Google Search now saves uploaded files, images, and audio in your history to train AI models. Here's how to view and turn off the Save Media setting.

Outlook for Mac Glitch Omits Original Message Content Microsoft Outlook for Mac glitch causing missing email body content
  • Technology

Outlook for Mac Glitch Omits Original Message Content

Do Son June 24, 2026 0

Discover the latest Outlook for Mac glitch omitting original message text during replies, along with Microsoft's official workarounds.

Cloudflare PACT Protocol: A Privacy-First Era of Verification Diagram of the Cloudflare PACT protocol authenticating users without CAPTCHA
  • Technology

Cloudflare PACT Protocol: A Privacy-First Era of Verification

Do Son June 24, 2026 0

Discover the Cloudflare PACT protocol, a privacy-first initiative with Chrome, Edge, and Firefox to eliminate CAPTCHAs and authenticate web traffic safely.
AVer PTC Cameras Hit by Critical RCE Flaw CVE-2026-40624 (CVSS 9.8) AVer PTC camera flaw CVE-2026-40624 enabling remote code execution
  • Vulnerability Report

AVer PTC Cameras Hit by Critical RCE Flaw CVE-2026-40624 (CVSS 9.8)

Do Son June 24, 2026 0

CISA flags an AVer PTC camera flaw, CVE-2026-40624, enabling remote code execution. The CVSS 9.8 RCE bug affects four PTC models.

Containerd Critical Vulnerabilities Expose Host Servers Diagram explaining containerd critical vulnerabilities including CVE-2026-53492 and cache poisoning
  • Vulnerability Report

Containerd Critical Vulnerabilities Expose Host Servers

Do Son June 24, 2026 0

Three containerd critical vulnerabilities, including CVE-2026-53492, allow attackers to execute host commands and poison image caches. Patch immediately.

Webmin 2.641 Fixes Three Vulnerabilities Including a Critical Auth Bypass Webmin vulnerabilities authentication bypass CVE-2026-56020 patched in 2.641
  • Vulnerability Report

Webmin 2.641 Fixes Three Vulnerabilities Including a Critical Auth Bypass

Do Son June 24, 2026 0

Three Webmin vulnerabilities, including a critical authentication bypass (CVE-2026-56020), expose servers. Update to Webmin 2.641 to stay safe.

Can You Trust Your Exchange? Inside BTCC’s Monthly Proof-of-Reserves Audit CVE-2024-55563 - transaction-relay jamming attack
  • Technique

Can You Trust Your Exchange? Inside BTCC’s Monthly Proof-of-Reserves Audit

Do Son June 24, 2026 0
When you deposit crypto onto a centralized exchange, you are handing over custody. The exchange’s database ledger...
Read More Read more about Can You Trust Your Exchange? Inside BTCC’s Monthly Proof-of-Reserves Audit
How Secure Virtual Assistants Improve Outbound Calling Workflows call
  • Technique

How Secure Virtual Assistants Improve Outbound Calling Workflows

Do Son June 24, 2026 0
Outbound calling can create pipeline, but it can also create risk. For US teams, outsourced calling security...
Read More Read more about How Secure Virtual Assistants Improve Outbound Calling Workflows
Squidbleed (CVE-2026-47729): Squid Proxy Memory Leak Details and PoC Disclosed Squidbleed vulnerability CVE-2026-47729 Squid proxy memory leak diagram
  • Vulnerability Report

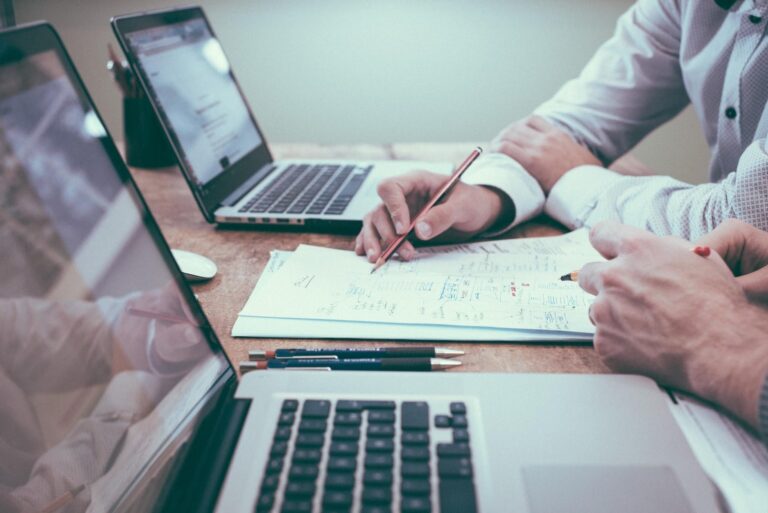
Squidbleed (CVE-2026-47729): Squid Proxy Memory Leak Details and PoC Disclosed

Do Son June 24, 2026 0

The Squidbleed vulnerability is a Squid proxy memory leak exposing user credentials. CVE-2026-47729 details and PoC exploit code are now public.
Top Train Ticket Booking App Development Companies in the USA tech-pass
  • Technique

Top Train Ticket Booking App Development Companies in the USA

Do Son June 24, 2026 0

Discover the top train ticket booking app development companies in the USA. Compare leading rail-tech firms and learn how to select the right partner.

LastPass Customer Data Stolen in Klue Supply Chain Breach LastPass Klue breach OAuth token theft Salesforce supply chain attack
  • Data Leak

LastPass Customer Data Stolen in Klue Supply Chain Breach

Do Son June 23, 2026 0

LastPass confirms the Klue breach exposed customer CRM data via OAuth token theft in Salesforce. Vaults stayed safe. Here's what to know.

CISA Adds Four Exploited UniFi OS and Lantronix Flaws to KEV Catalog CISA KEV catalog actively exploited vulnerabilities CVE-2026-34908 UniFi OS Lantronix EDS5000
  • Vulnerability Report

CISA Adds Four Exploited UniFi OS and Lantronix Flaws to KEV Catalog

Do Son June 23, 2026 0

CISA added four actively exploited vulnerabilities to its KEV catalog, hitting Ubiquiti UniFi OS and Lantronix EDS5000. Patch before June 26, 2026.

Internet Society Foundation Opens Global Call for Common Good Cyber Fund to Strengthen Cybersecurity  CGCF_Featured_image_17822196430bFkMKNfEs
  • Press Release

Internet Society Foundation Opens Global Call for Common Good Cyber Fund to Strengthen Cybersecurity 

cybernewswire June 23, 2026 0
DC, United States, June 23rd, 2026, CyberNewswire   Applications open 23 June–4 August 2026 to support nonprofits...
Read More Read more about Internet Society Foundation Opens Global Call for Common Good Cyber Fund to Strengthen Cybersecurity 
GitBait Phishing Campaign Targets 12 Mexican Banks via GitHub Pages GitBait phishing campaign abusing GitHub Pages and SheetBest API to steal Mexican banking credentials
  • Cybercriminals

GitBait Phishing Campaign Targets 12 Mexican Banks via GitHub Pages

Do Son June 23, 2026 0

The GitBait phishing campaign abuses GitHub Pages and the SheetBest API to steal banking credentials from at least 12 Mexican financial institutions.
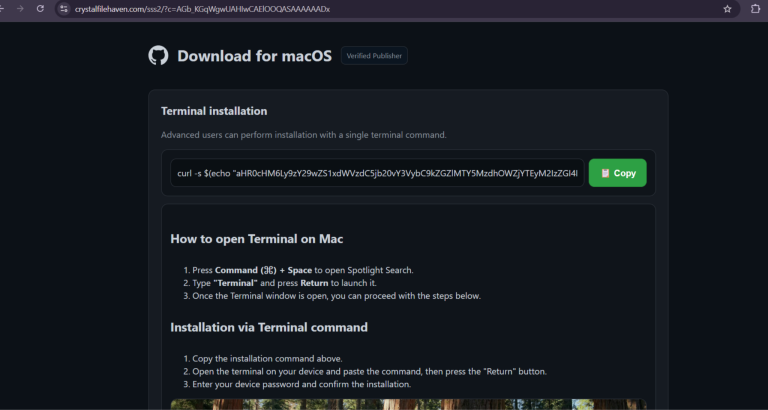
macOS ClickFix AppleScript Stealer Hijacks Crypto Wallets macOS ClickFix AppleScript stealer diagram showing the Meow macOS stealer infection chain
  • Malware

macOS ClickFix AppleScript Stealer Hijacks Crypto Wallets

Do Son June 23, 2026 0

A new macOS ClickFix AppleScript stealer named the Meow macOS stealer acts as a persistent RAT, hijacking wallets and evading detection. Protect your Macs.
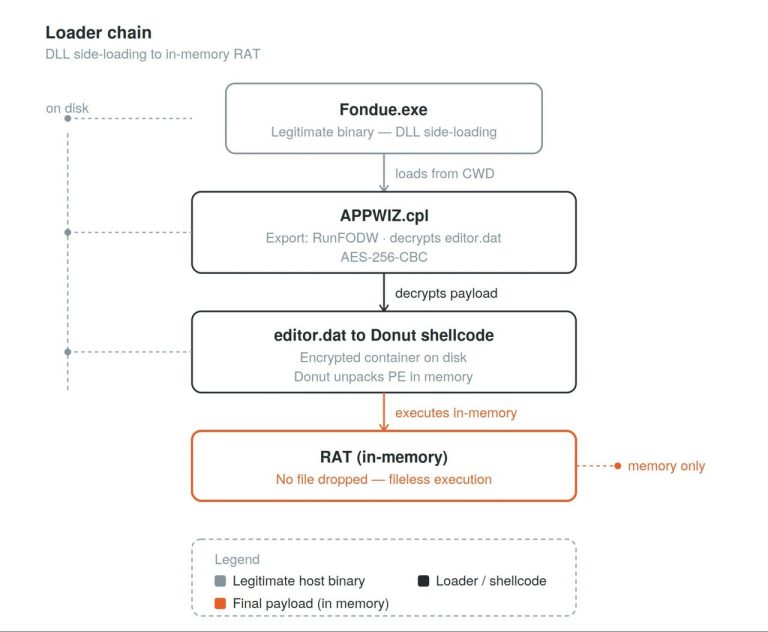
Dropping Elephant Malware: China-Themed Loader Campaign Analyzed Dropping Elephant malware China-themed loader and in-memory RAT diagram
  • Malware

Dropping Elephant Malware: China-Themed Loader Campaign Analyzed

Do Son June 23, 2026 0

Rapid7 exposes a new Dropping Elephant malware campaign using a China-themed loader to deploy a fileless RAT. Learn about its evasion tactics and defense.

AryStinger Malware Attacks Routers via CVE-2013-3307 AryStinger malware infection chain exploiting CVE-2013-3307
  • Malware

AryStinger Malware Attacks Routers via CVE-2013-3307

Do Son June 23, 2026 0

A new AryStinger malware campaign exploits CVE-2013-3307 and CVE-2016-5681 to compromise legacy routers, building a global attack proxy network.

Cloud DNS Takeover Powers Thai Gambling Campaign Zammad zero-day CVE-2026-102489 CVE-2026-102490 exploited in DIVD breach
  • Cybercriminals

Cloud DNS Takeover Powers Thai Gambling Campaign

Do Son June 23, 2026 0

A massive cloud DNS takeover campaign exploits abandoned enterprise domains to serve Thai gambling content. 163 organizations are currently compromised.

Android Developer Verification: Google Reveals the Full Timeline Android developer verification timeline showing the September 30 2026 sideloading enforcement and 24-hour advanced flow
  • Android

Android Developer Verification: Google Reveals the Full Timeline

Do Son June 23, 2026 0

Google's Android developer verification starts enforcing on Sept 30, 2026. See the full timeline, the 24-hour sideload flow, and the ADB exemption.
Tata Electronics Data Breach Exposes Apple and Tesla Files Tata Electronics data breach leaking Apple and Tesla component design and specification files on a dark web site
  • Data Leak

Tata Electronics Data Breach Exposes Apple and Tesla Files

Do Son June 23, 2026 0

A Tata Electronics data breach exposed 630GB of files. Hackers claim Apple and Tesla design documents are in the stolen 200,000-file haul.

Apple AirPort Utility Deprecated in iOS 27 & macOS 27 Apple AirPort Utility deprecated notice on legacy wireless routers AFP protocol macOS 27, SMB3 protocol, Apple Filing Protocol, file sharing protocol Apple WWDC 2026 announcements
  • Technology

Apple AirPort Utility Deprecated in iOS 27 & macOS 27

Do Son June 23, 2026 0

Apple confirms the AirPort Utility app is going away soon. Discover how the AirPort Utility deprecated status affects legacy Wi-Fi router management.
iOS 27 Developer Beta 2 Adds Write with Siri and RCS Replies iOS 27 Developer Beta 2 new features including Write with Siri keyboard button and RCS inline replies
  • Technology

iOS 27 Developer Beta 2 Adds Write with Siri and RCS Replies

Do Son June 23, 2026 0

iOS 27 Developer Beta 2 brings Write with Siri on the keyboard, RCS inline replies, Wallet Insights, and an iPhone Mirroring fix.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-81648CVSS 10.0
    The CryptoPayment Gateway WordPress plugin from 1.2.1 to 1.2.2 does not apply an authorization check on one of...
    Admin intel📅 Updated: Nov 3, 2026
  • CVE-2026-58115CVSS 10.0
    A vulnerability has been identified in SIMATIC IoT2050 Advanced (6ES7647-0BA00-1YA2) (All versions < V4.3.4.1 running Industrial OS with...
    Admin intel📅 Updated: Nov 2, 2026
  • CVE-2026-20051CVSS 7.4
    A vulnerability with the Ethernet VPN (EVPN) Layer 2 ingress packet processing of Cisco Nexus 3600 Platform Switches...
    Watchtower Verified📅 Updated: Nov 1, 2026
  • CVE-2026-20118CVSS 6.8
    A vulnerability in the handling of an Egress Packet Network Interface (EPNI) Aligner interrupt in Cisco IOS XR...
    Watchtower Verified📅 Updated: Nov 1, 2026
  • CVE-2010-20125CVSS 8.7
    DedeCMS before 5.7 contains a file inclusion vulnerability in plus/carbuyaction.php that allows remote unauthenticated attackers to control the...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2015-20130CVSS 5.1
    Netsweeper before 4.0.11 and 4.1.0 before 4.1.5 contains a reflected cross-site scripting vulnerability in webadmin/reporter/view_server_log.php that allows remote...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2026-111357CVSS 7.0
    Ivanti Connect Secure 22.8R2.4 mishandles the manner in which the dsinvoked broker trusts DSCache configuration data, leading to...
    CISA KEV📅 Added to KEV: Oct 30, 2026
  • CVE-2026-118527CVSS 4.3
    Use of predictable filenames in Ivanti Connect Secure before versions 25.1.1.3 and 22.8R2.6 allows a remote authenticated attacker...
    CISA KEV📅 Added to KEV: Oct 30, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-13594CVSS 9.1
    Zoho Corporation's ManageEngine Log360 and EventLog Analyzer versions 13062 and below are vulnerable to an issue that could...
    📅 Updated: Nov 3, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    📅 Updated: Nov 3, 2026
  • CVE-2026-86473CVSS 9.1
    Apache Airflow: the Core API logout endpoint revokes only a session token presented as the _token cookie. When...
    📅 Updated: Nov 3, 2026
  • CVE-2026-42252CVSS 9.1
    Apache Airflow's official documentation at `core-concepts/dag-run.html` ("Passing Parameters when triggering Dags") showed a verbatim `BashOperator(bash_command="echo value: {{ dag_run.conf['conf1']...
    📅 Updated: Nov 3, 2026
  • CVE-2026-33264CVSS 9.8
    A bug in `BaseSerialization.deserialize()` allowed unrestricted `import_string()` of attacker-controlled class paths when the Scheduler / API Server loaded...
    📅 Updated: Nov 3, 2026
  • CVE-2025-57735CVSS 9.1
    When user logged out, the JWT token the user had authtenticated with was not invalidated, which could lead...
    📅 Updated: Nov 3, 2026
  • CVE-2026-81648CVSS 10.0
    The CryptoPayment Gateway WordPress plugin from 1.2.1 to 1.2.2 does not apply an authorization check on one of...
    Admin intel📅 Updated: Nov 3, 2026
  • CVE-2026-94290CVSS 9.1
    SUSE Rancher Fleet clusters reference a kubeconfig secret that the controller uses to install and manage a Fleet...
    📅 Updated: Nov 3, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.