
 Do Son
This weekly CVE report covers 2,060 new vulnerabilities from June 15-21, including 358 critical flaws and 4 actively exploited CVEs now in CISA KEV.
Four undici vulnerabilities (CVE-2026-6734, CVE-2026-9697) affect the Node.js HTTP client, which sees 133M weekly downloads. Update undici now.

ErrTraffic malware powers ClickFix attacks on hacked WordPress sites, using EtherHiding on the blockchain to hide its C2 and spread infostealers.
CVE-2026-55518 is a critical Avo authorization bypass flaw enabling privilege escalation in Ruby on Rails admin panels. Update to Avo 3.32.1 now.

Three critical pgAdmin 4 vulnerabilities (CVE-2026-12046, CVE-2026-12048, CVE-2026-12045) risk XSS and RCE. Update to pgAdmin 4 9.16 now.

A public PoC exploit for the FreeBSD kTLS vulnerability (CVE-2026-45257) enables local privilege escalation to root. Patch your FreeBSD systems now.
QNAP patched 14 NAS vulnerabilities in QTS, QuTS hero, and QVP, including command injection and credential-theft flaws. Update your QNAP NAS now.
A new npm package uses prompt injection and token flooding for AI malware scanner evasion. Discover how attackers disrupt AI-assisted malware review.

Attackers exploit ArcGIS Account Recovery flaws. Read this security bulletin to secure your enterprise by disabling default accounts and enabling SMTP.
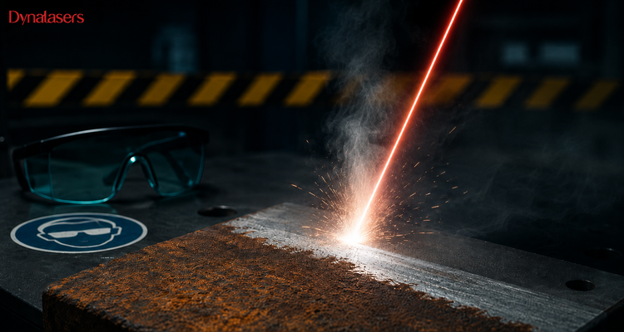
Learn safety checks before choosing a laser cleaning machine manufacturer for rust removal, paint stripping, oxide removal, and industrial cleaning.

A new device code phishing campaign abuses Microsoft's OAuth flow to hijack Microsoft 365 accounts, no password stealing needed. How to spot it.

GlassWASM malware hides WebAssembly payloads in trojanized Open VSX extensions, abusing Solana memos for stealthy command-and-control.
A transmitter with the highest advertised depth isn’t automatically the right choice for a difficult bore. Deep...

 cybernewswire
Luxembourg, Luxembourg, 19th June 2026, CyberNewswire


The UNC1151 Gmail phishing campaign by Ghostwriter steals passwords and 2FA codes from Polish targets via fake Google login pages. Stay alert.

IBM X-Force links the Interlock and Rhysida ransomware ecosystem through shared malware like Supper, NodeSnake, and overlapping crypters.
CVE-2026-8713 is a critical Avada Builder vulnerability enabling unauthenticated arbitrary file deletion on 1M WordPress sites. Update to 3.15.4 now.

Discover how APT37 NarwhalRAT malware uses MS-themed phishing and a dead-drop C2 to target users with a sophisticated Python backdoor.

Google Calendar now offers 200 custom colors and a full RGB picker, replacing its old 11-color limit for events.

Anthropic initiates a Claude Code quota reset for premium subscribers affected by a morning server glitch that erroneously blocked message transmissions.

Discover how the MaXSS and Spyder Chrome extension vulnerabilities in MaxAI and SiderAI put millions at risk. Protect your browser sessions today.