Skip to content
October 13, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
  • Home
  • News
  • Malware
  • RedLine malware pretends to be a Windows 11 upgrade installers
  • Malware

RedLine malware pretends to be a Windows 11 upgrade installers

Do Son February 9, 2022 2 minutes read
RedLine malware

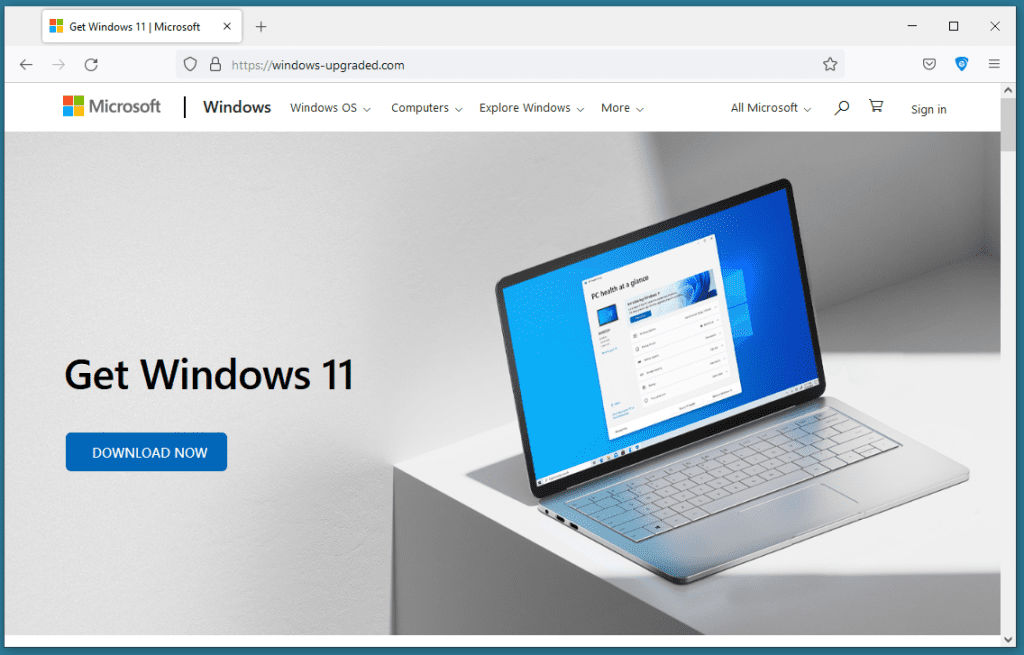
Fake website used for malware distribution (HP)

Add Daily CyberSecurity as a preferred source on Google

Security researchers have noticed cases where hackers began to distribute malware to Windows 10 users under the guise of upgrading Windows 11 systems. Microsoft is currently deploying Windows 11 systems widely, so most supported devices should receive a prompt from Microsoft via system update pushes at this time. Criminals also saw an opportunity in this case, and the gang behind the RedLine malware started creating fake upgrades to lure users into downloading.

RedLine malware
Fake website used for malware distribution (HP)

Since it is a system upgrade program, the file size should be relatively large, so the volume of the upgrade program package forged by the criminals is as high as 753MB. Of course, don’t expect the upgrade program to be so big, otherwise, it may take a long time for users to download, and hackers obviously won’t let users spend time waiting. The phishing website windows-upgraded[.]com created by the criminals looks very real, and the actual downloaded upgrade program is only 1.5MB. Decompressing the file results in a folder of 753MB of size, showcasing an impressive compression ratio of 99.8%, achieved thanks to the presence of padding in the executable.

When the user launches the program, the malware connects to the command-and-control server and gets instructions from the server.

This kind of routine is actually very common, and the phishing website has been shut down, but I believe this fake upgrade assistant should be slowly spreading on the Internet. Hackers will induce users to download through other means, such as posting on some social forums, and some may also bundle them through some download sites and install them silently.

For users who want to upgrade the Windows 11 system, they can directly click Update in the system, or download the upgrade assistant from Microsoft’s official website and follow the prompts.

Finally, let’s talk about the RedLine malware. This is an old malware but it is still very harmful, especially when it performs a variety of malicious operations. The main behaviors include stealing browser cookies to log in to user accounts, stealing passwords, stealing credit card information, and even stealing cryptocurrency wallet keys.

Related coverage

  • New Android Banking Trojan Targets Indian Users Through Fake Apps
  • AI’s Supply Chain Nightmare: The Lightning Framework Worm and the “Silence Developer” Meme
  • The “Gentlemen” Ransomware Toolkit and the Lethal z1.bat Pre-Encryption Weapon
  • RedCurl APT Group: Cyber Espionage with Living-Off-the-Land Techniques
  • SmokeLoader Rises From the Ashes with New, Evasive Variants
  • Hamas-Linked SysJoker Backdoor: A Persistent Threat’s New Dangerous Facade
Track all actively exploited CVEs →

Support Our Threat Intelligence

Find our threat intelligence and malware analysis helpful? Support our work today and unlock a 100% ad-free reading experience!

Buy Me a Coffee Logo Buy Me a Coffee
Select your plan
Free Pro Team

Hover over a plan to see its benefits.

Get Zero-Hour Vulnerability Alerts

Critical CVEs, CVSS scores, and PoC updates — straight to your inbox every week.

We respect your inbox. Unsubscribe anytime.

SHARE
Share on FacebookShare on XShare on LinkedInShare on TelegramShare on BlueskyShare on Mastodon
Written by
@DdoS Β· Security Researcher

Do Son

Do Son is the Founder and Editor of SecurityOnline.info. Working in cybersecurity since 2013, he reports on vulnerabilities, malware, and emerging threats, providing timely analysis to help organizations and individuals stay ahead of evolving risks.

Tags: RedLine malware

Search

Translation

CVE ALERTS
πŸ“ˆ

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

πŸ›‘οΈ

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

πŸ™

GitHub Issues
Auto-create alert tickets without duplication.

πŸ“¬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

πŸ”€

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days β†’

🚨 Active Exploits in the Wild

  • CVE-2026-104935CVSS 8.6
    Authentication bypass by spoofing in ICS before version 25.1.3.0 allows a remote unauthenticated attacker to execute arbitrary commands....
    Admin intel📅 Updated: Oct 13, 2026
  • CVE-2026-102255CVSS 10.0
    A Pre-authentication SSRF vulnerability exists in the SMA1000 Appliance Work Place interface due to an unintended alternate access...
    Admin intel📅 Updated: Oct 9, 2026
  • CVE-2026-105133CVSS 6.9
    A vulnerability was detected in Ahsay AhsayCBS up to 10.3.2. This affects the function checkSysPwd of the file...
    Admin intel📅 Updated: Oct 9, 2026
  • CVE-2023-22894CVSS 4.9
    Strapi through 4.5.5 allows attackers (with access to the admin panel) to discover sensitive user details by exploiting...
    CISA KEV📅 Added to KEV: Oct 8, 2026
  • CVE-2016-3081CVSS 8.1
    Apache Struts 2.3.19 to 2.3.20.2, 2.3.21 to 2.3.24.1, and 2.3.25 to 2.3.28, when Dynamic Method Invocation is enabled,...
    CISA KEV📅 Added to KEV: Oct 8, 2026
  • CVE-2015-3306CVSS 10.0
    The mod_copy module in ProFTPD 1.3.5 allows remote attackers to read and write to arbitrary files via the...
    CISA KEV📅 Added to KEV: Oct 8, 2026
  • CVE-2015-5477CVSS 7.5
    named in ISC BIND 9.x before 9.9.7-P2 and 9.10.x before 9.10.2-P3 allows remote attackers to cause a denial...
    CISA KEV📅 Added to KEV: Oct 8, 2026
  • CVE-2021-3199CVSS 9.8
    Directory traversal with remote code execution can occur in /upload in ONLYOFFICE Document Server before 5.6.3, when JWT...
    CISA KEV📅 Added to KEV: Oct 8, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-89107CVSS 9.9
    SAP S/4HANA (Manage Substitution/Validation Rules) does not sufficiently validate input processed by rule definition functionality that utilizes a...
    📅 Updated: Oct 13, 2026
  • CVE-2026-89108CVSS 9.1
    SAP Manufacturing Integration and Intelligence does not sufficiently enforce authorization boundaries within certain administrative functionality. An attacker with...
    📅 Updated: Oct 13, 2026
  • CVE-2026-89110CVSS 9.9
    SAP NetWeaver Visual Composer does not perform sufficient authorization checks in certain portal functionality. An attacker with low...
    📅 Updated: Oct 13, 2026
  • CVE-2026-64007CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: netfilter: synproxy: refresh tcphdr after skb_ensure_writable synproxy_tstamp_adjust() rewrites...
    📅 Updated: Oct 13, 2026
  • CVE-2026-109520CVSS 9.3
    A flaw has been found in Colorful iGameCenter 2.0.0.82. Affected by this vulnerability is the function MmMapIoSpace in...
    📅 Updated: Oct 13, 2026
  • CVE-2026-109573CVSS 9.2
    phpMyFAQ before 4.1.9 contains an SQL injection vulnerability in PdoMysql::escape(), which escapes single quotes with backslashes that are...
    📅 Updated: Oct 13, 2026
  • CVE-2026-104803CVSS 9.8
    The WPCOM Member plugin for WordPress is vulnerable to Authentication Bypass in all versions up to, and including,...
    📅 Updated: Oct 13, 2026
  • CVE-2026-103889CVSS 9.8
    The 3D Product configurator for WooCommerce plugin for WordPress is vulnerable to Remote Code Execution in all versions...
    📅 Updated: Oct 13, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
Β© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.