 Do Son
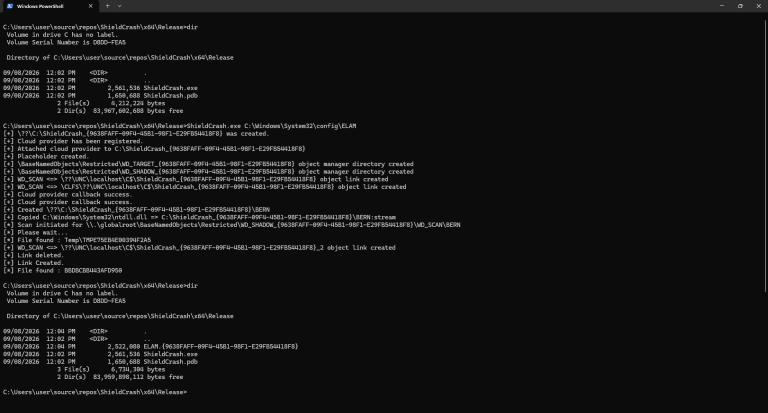
A Windows Defender 0day, CVE-2026-69414, has public PoC exploit code. ShieldCrash reads files as SYSTEM on all supported Windows versions.
0day

Identified as CVE-2023-4863, the vulnerability traces its origin to a heap buffer overflow in the WebP image format