 Do Son
7-Zip vulnerability CVE-2026-14266 (CVSS 7.0) allows remote code execution via crafted XZ data. Update to 7-Zip 26.02. No exploitation confirmed.
7-Zip

CVE-2026-48095 (CVSS 8.8) is a heap buffer overflow in 7-Zip that a crafted archive can trigger. Update to the patched version now.

Warning: 7zip [.] com has been hijacked to spread residential proxy malware. Learn how to identify this 7-Zip impersonator and protect your system.
A patched 7-Zip path-traversal flaw (RCE) now has public exploit code. Users must update immediately, as 7-Zip lacks auto-updates.

The Zero Day Initiative (ZDI) has published details of two critical vulnerabilities in the popular open-source compression...

A critical vulnerability (CVE-2025-55188, CVSS 2.7) in 7-Zip allows remote attackers to perform arbitrary file writes via a crafted archive, potentially leading to code execution.

Two new medium-severity vulnerabilities (CVE-2025-53816, -53817) in 7-Zip versions prior to 25.0.0 risk memory corruption and denial of service. Update immediately.
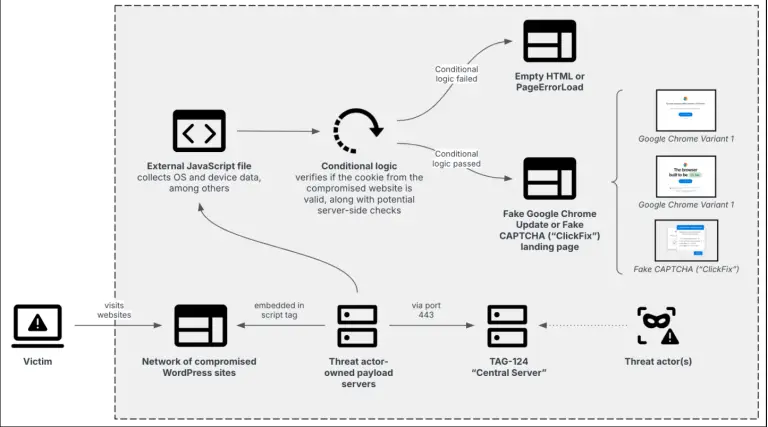
GrayAlpha, linked to FIN7, escalates tactics with fake browser/7-Zip updates and TAG-124 TDS, spreading NetSupport RAT in a multi-pronged infection campaign.

Uncover the LegionLoader Campaign's deceptive tactics. Learn how fake CAPTCHAs and CloudFlare Turnstile are used in malware distribution.

Security researcher Dhmos Funk released a PoC exploit for CVE-2025-0411 (CVSS 7.0), a high-severity vulnerability in the 7-Zip file archiver
Find out how a flaw in 7-Zip could have exposed Windows to malware attacks. Learn about the high-risk CVE-2025-0411 vulnerability.

7-Zip vulnerability (CVE-2024-11477): understand the risks and learn how to safeguard your systems from potential code execution attacks.

CVE-2023-31102 is a serious vulnerability that can allow attackers to execute arbitrary code on the victim's computer.