 Do Son
A ProFTPD ACL bypass (CVE-2026-35025, CVSS 8.6) lets logged-in FTP users reach files in restricted directories. No patch is out yet; use DefaultRoot.
access control bypass
Ubiquiti patches three critical CVSS 10.0 vulnerabilities in UniFi OS affecting gateways, storage, and NVRs. Update your firmware immediately!

Splunk releases coordinated patches for CVE-2026-20240 and adjacent flaws exposing raw session cookies, data filters, and triggering server DoS.
Two critical flaws in Spring AI (CVE-2026-22729 & CVE-2026-22730) allow attackers to bypass access controls via JSONPath and SQL injection. Update now.

Apache Superset 6.0.0 addresses high-severity flaws, including a PostgreSQL read-only bypass and dataset access control leaks. Secure your BI platform today!

A normalization flaw in Better Auth's router allows attackers to bypass access controls and rate limits using simple double-slash URLs.
Hikvision has issued an advisory for three flaws in its HikCentral products. The most severe, with a CVSS of 8.6, allows an unauthenticated user to get admin access.

Two critical flaws in Apache Traffic Server (CVE-2025-31698, CVE-2025-49763) allow IP-based ACL bypass and remote DoS via ESI plugin.

Cloud Software Group issues urgent patches for two critical NetScaler flaws allowing access bypass and memory overread. Update immediately.
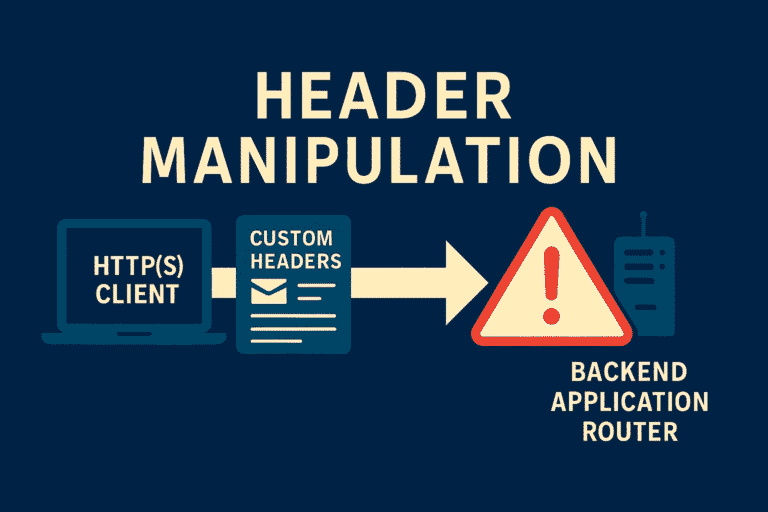
A critical flaw in Fabio load balancer allows malicious clients to manipulate or strip HTTP headers, leading to potential access control bypass. Upgrade to 1.6.6.