 Do Son
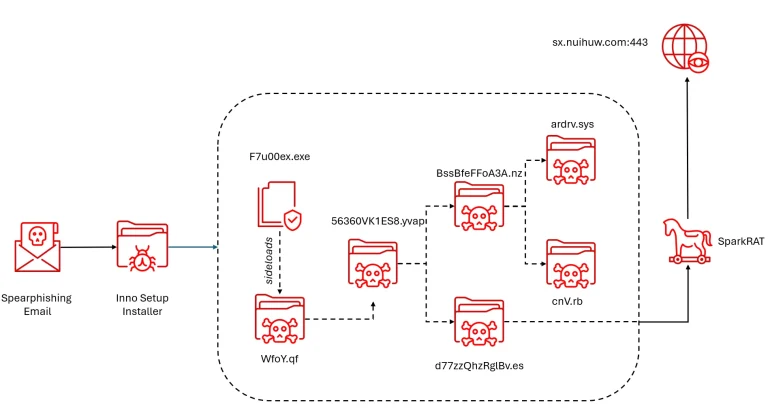
A Cambodia malware campaign hides SparkRAT in PNG files and abuses a vulnerable driver to kill antivirus, Acronis TRU reports.
Acronis TRU

A Lampion malware campaign is hitting Portugal. The Portugal phishing campaign uses fake SAPO transfer pages to drop a multistage VBS infection chain.
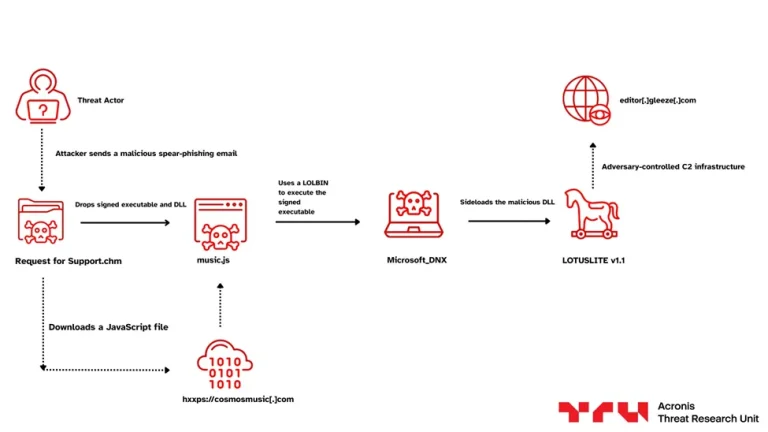
Mustang Panda targets India’s financial sector with the LOTUSLITE malware. Learn how this DLL sideloading campaign bypasses defenses for cyber-espionage.
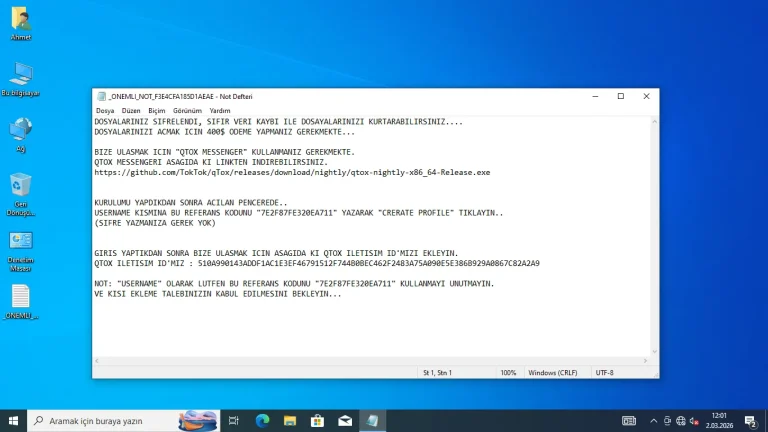
Acronis uncovers JanaWare, a persistent ransomware targeting Turkey since 2020. Discover how geofencing and polymorphism keep this threat in the shadows.

Acronis uncovers a massive campaign targeting gamers with fake cheats to deliver Vidar Stealer 2.0, a highly evasive malware stealing crypto and passwords.
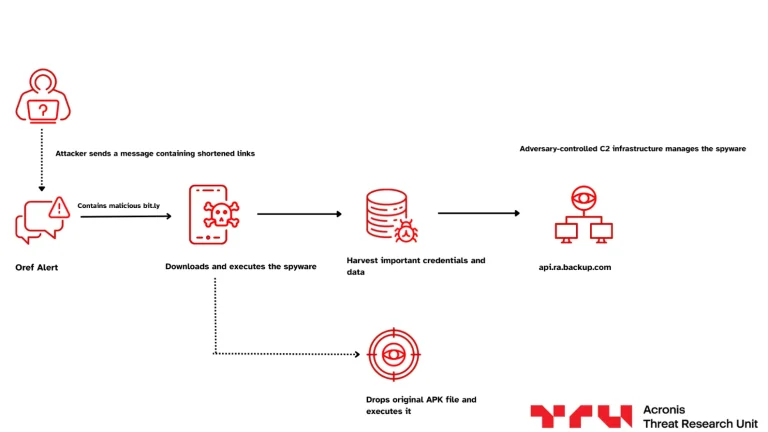
Acronis TRU uncovers a trojanized Red Alert rocket warning app targeting Israelis. Linked to APT-C-23, this Android malware steals data while alerting users.

Acronis uncovers CRESCENTHARVEST, a new spyware targeting Iranian dissidents. Attackers use protest lures & Google DLL sideloading to steal data.

LockBit 5.0 launches with a unified codebase targeting Windows, Linux, and ESXi. Acronis reveals identical encryption and ties to SmokeLoader.

Mustang Panda targets US gov with new LOTUSLITE backdoor. Campaign uses Venezuela lures and DLL sideloading to evade detection.