 Do Son
Two Citrix NetScaler zero-day RCE flaws are under active exploitation. Citrix confirmed CVE-2026-88771 and CVE-2026-88772 and shipped patches. Update now.
Active Exploitation
PaperCut confirms a NG/MF vulnerability exploited in the wild. Restrict server access now and apply the emergency patch for versions 25 and 26.

CVE-2026-54420, a LiteSpeed cPanel privilege escalation flaw, is exploited in the wild to gain root on shared hosting. Patch to plugin v2.4.8 now.
Cisco warns CVE-2026-20262, a Cisco SD-WAN vulnerability enabling arbitrary file write, is exploited in the wild. Patch SD-WAN Manager now.

A Jenkins RCE vulnerability (CVE-2026-53435) is under active exploitation. Honeypots are seeing attacks now, so patch your Jenkins controller fast.
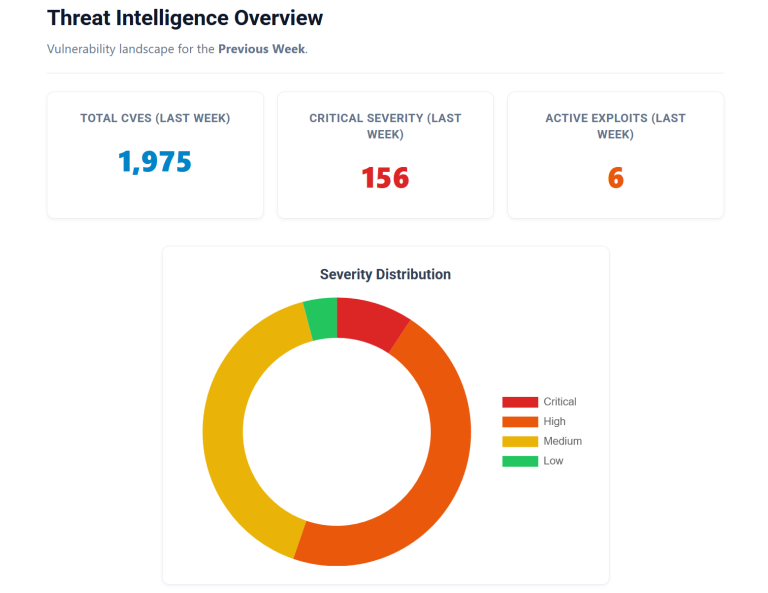
Cisco SD-WAN (CVE-2026-20182) and Exchange Server (CVE-2026-42897) are actively exploited in the wild! Discover the top threats you must patch now.

Ivanti confirms active exploitation of EPMM (CVE-2026-6973). Attackers are using old credentials to hijack mobile management. Patch to v12.8.0.1 immediately!
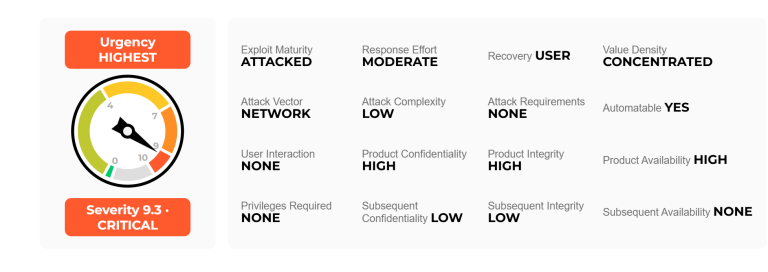
Palo Alto Networks confirms CVE-2026-0300 is being exploited in the wild. The 9.3 CVSS flaw allows unauthenticated root RCE. Secure your PAN-OS firewalls now!

CISA adds 8 vulnerabilities to the KEV Catalog, including Cisco, PaperCut, and Zimbra flaws. Actively exploited threats require immediate patching.

Shadowserver warns of active exploitation of CVE-2021-4473 in Tianxin systems. This 9.3 CVSS flaw allows unauthenticated RCE. Patch your firmware immediately!

PolyShell Exposed: Public PoC and active exploitation disclosed for critical Magento RCE. With no official patch, your storefront is at risk. Secure it now!

A critical 10.0 CVSS flaw (CVE-2026-20127) in Cisco Catalyst SD-WAN is actively exploited in the wild. A public PoC is now available. Patch immediately!

Cisco warns that two vulnerabilities (CVE-2026-20122 and CVE-2026-20128) in its Catalyst SD-WAN Manager are being actively exploited. Update immediately.

Unit 42 warns of active attacks on critical BeyondTrust flaw CVE-2026-1731. Hackers bypass auth for RCE and data theft. Patch self-hosted instances now.

Critical FileZen flaw CVE-2026-25108 is under active attack. Antivirus feature allows command injection. Update to V5.0.11 immediately to secure data.

Critical SmarterMail flaw WT-2026-0001 allows unauthenticated admin reset & RCE. Attackers are exploiting this in the wild. Update to Build 9511 now.

Critical Academy LMS flaw CVE-2025-15521 (CVSS 9.8) is being exploited. Unauthenticated attackers can reset admin passwords. Update now to secure your site.

Cisco warns CVE-2026-20045 is being exploited. This critical RCE allows unauthenticated root access on Unified CM. Patch immediately to secure your network.

Urgent: Modular DS flaw CVE-2026-23550 (CVSS 10) is actively exploited in the wild. Attackers are creating fake admins. Update to the latest version now.
CISA adds MongoBleed (CVE-2025-14847) to its KEV Catalog after confirming active exploitation. 80,000+ MongoDB servers are at risk. Patch by Jan 19!

A critical FortiGate SSO flaw (CVSS 9.1) is under active exploitation, letting unauthenticated attackers bypass login via crafted SAML. The flaw is armed by default registration, risking config exfiltration. Patch immediately.
CISA added a critical XXE flaw (CVE-2025-58360) in OSGeo GeoServer to the KEV Catalog. The actively exploited bug allows attackers to read arbitrary files and perform SSRF on internal networks. Patch immediately.