 Do Son
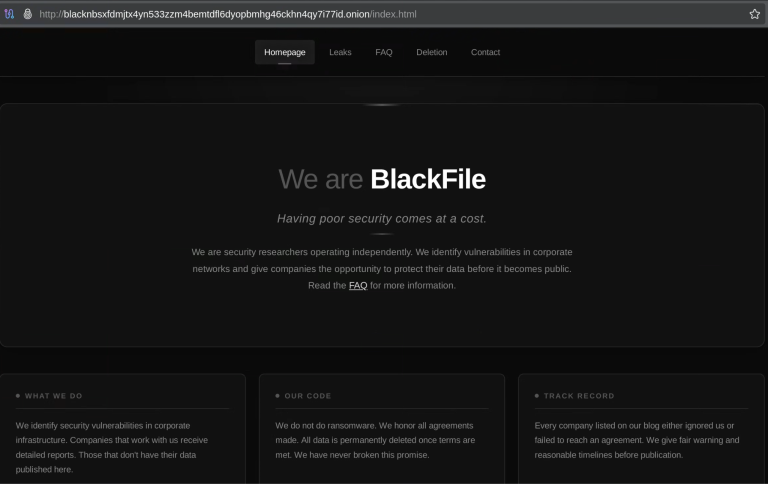
Google Threat Intelligence exposes UNC6671 ("BlackFile"), an aggressive group using vishing and AiTM proxies to bypass MFA in Microsoft 365 and Okta.
adversary-in-the-middle
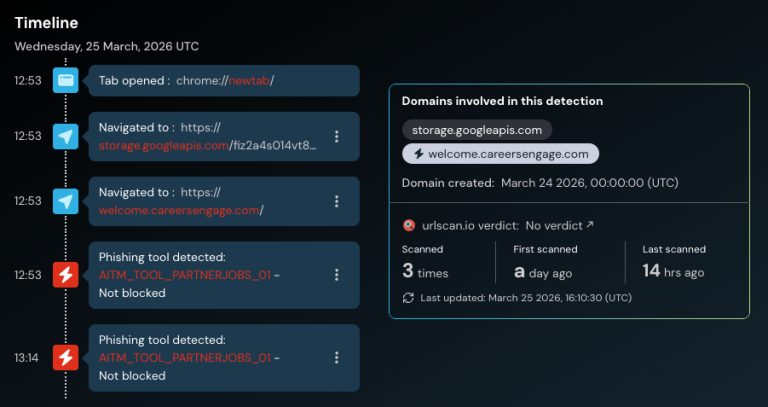
Researchers uncover a novel AiTM campaign targeting TikTok for Business. Attackers bypass MFA to steal Google SSO tokens and hijack corporate ad accounts.
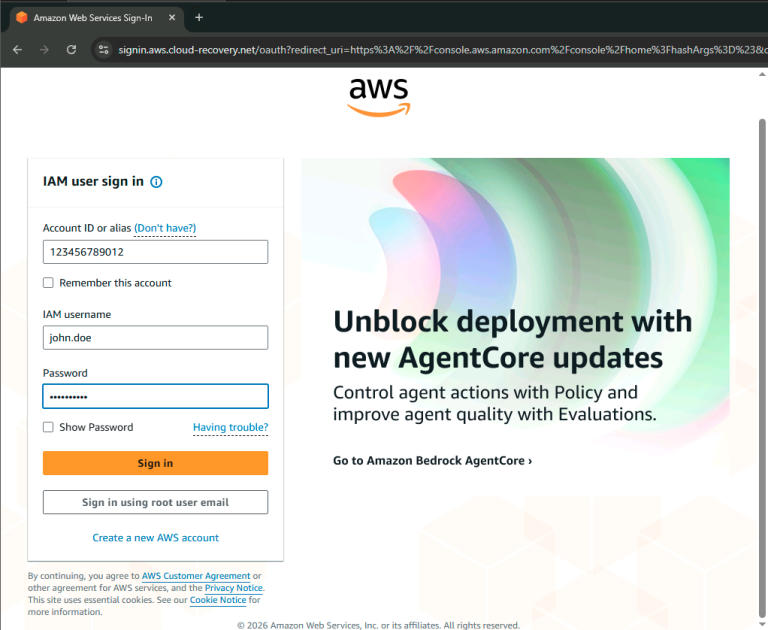
Datadog Security Research uncovers a sophisticated AiTM phishing campaign using real-time proxies to steal AWS Console credentials and bypass MFA in minutes.

A new advanced phishing kit, PoisonSeed, bypasses MFA with AitM techniques to steal credentials and launch cryptocurrency scams. NVISO uncovers the tactics.

Microsoft reveals Russian state actor Secret Blizzard is targeting foreign embassies in Moscow with ISP-level AiTM attacks, deploying ApolloShadow malware to spy on diplomats.

Microsoft's Digital Crimes Unit strikes blow against cybercrime supply chain. Learn how they seized 240 fraudulent websites and disrupted a major player in the PhaaS industry.

Beware of phishing campaigns using file hosting services as a launching pad for business email compromise attacks. Stay informed and secure.

NSPX30 implant, the arsenal of Blackwood, is a testament to the group's technical prowess. This is delivered through updates of legitimate software