 Do Son
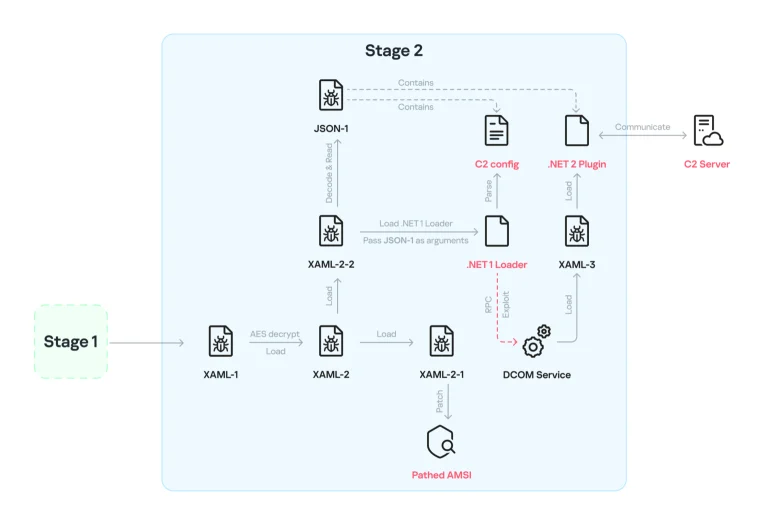
NetamLoader, a new XAML-based .NET loader, points to a supply chain attack on a custom Windows build used by government entities in Asia.
AMSI Bypass

A CrySome RAT phishing attack used a fake freight rate confirmation to bypass AMSI, disable Defender, and steal browser credentials on Windows.

An in-depth PHANTOMPULSE malware analysis reveals a sneaky blockchain C2 channel and AI-assisted coding techniques used by advanced threats.
Point Wild exposes a sophisticated PyInstaller loader using in-memory AMSI patching and SHA-512 decryption to drop XWorm V7.4. Patch now!

McAfee Labs exposes a massive CountLoader campaign using EtherHiding and AMSI bypass to drop stealthy cryptocurrency clippers. Secure your assets!

CYFIRMA warns of Operation SilentCanvas: A weaponized JPEG delivers trojanized ScreenConnect, bypassing AMSI and UAC for full-system surveillance. Stay alert!
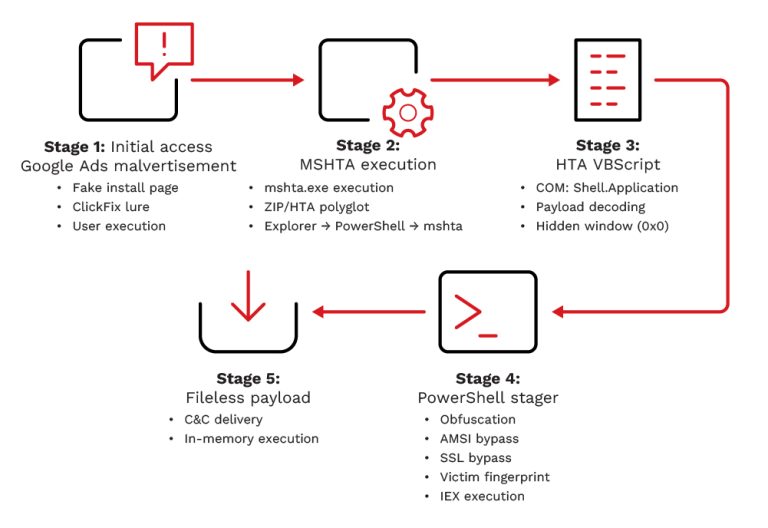
Beware of InstallFix: Fake Claude AI Google Ads trick users into running fileless scripts that deploy RedLine Stealer to steal passwords and crypto.
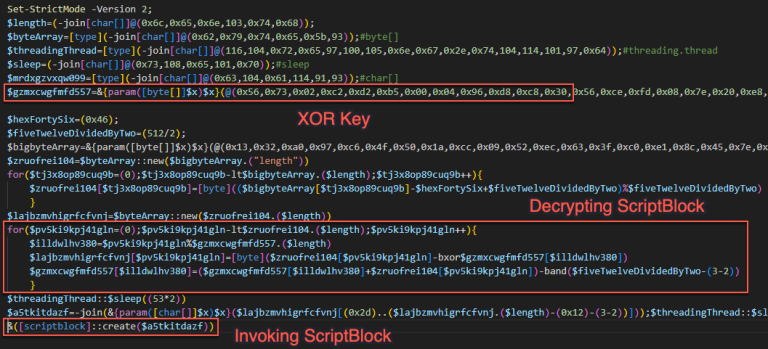
Rapid7 uncovers a fake Claude AI installer using ClickFix techniques to bypass AMSI and inject shellcode. Stay safe from this sophisticated AI-themed threat.
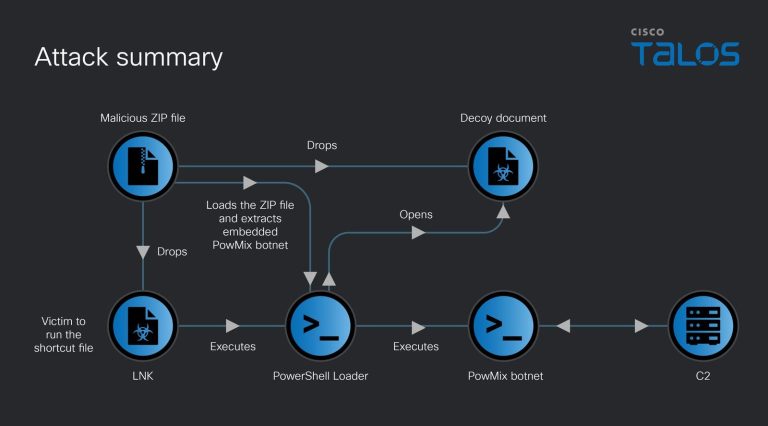
Cisco Talos uncovers PowMix, a stealthy botnet targeting Czech HR via AMSI bypass and Heroku-hosted C2. Learn how this malware evades modern EDR systems.
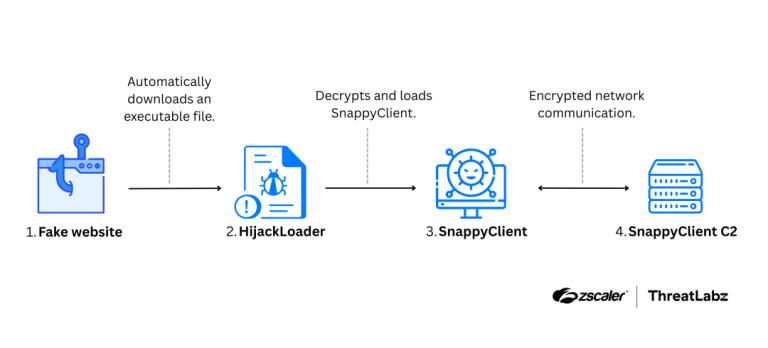
Zscaler ThreatLabz unmasks SnappyClient, a C++ C2 framework linked to HijackLoader. It uses AMSI bypass and Heaven’s Gate to steal crypto and gain remote access.

Trend Micro uncovers a selective PureLog Stealer campaign using fake legal notices and fileless execution to target healthcare and government sectors.

eSentire exposed the Amatera Stealer campaign using ClickFix social engineering to deliver multi-stage PowerShell. The malware patches AMSI in memory and deploys NetSupport RAT for remote access.

XWorm V6.0 has resurfaced with 35+ plugins, including ransomware functionality. The modular RAT uses stealth injection and obfuscated PowerShell to bypass AMSI.

Netskope uncovers XWorm 6.0, a new variant using VBScript droppers, AMSI bypass, and critical process marking to evade detection and force system reboots if terminated.

Splunk uncovers XWorm's evolution: a modular RAT now delivering LockBit ransomware. It uses flexible delivery, AMSI/ETW bypasses, and process injection to evade detection.