 Do Son
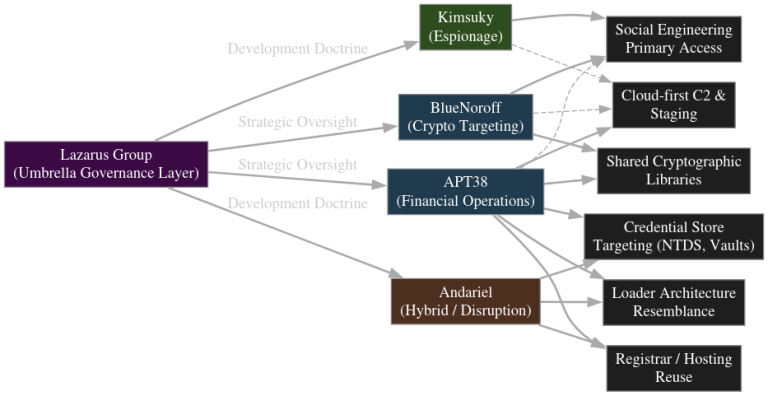
DomainTools exposes North Korea’s "mature portfolio model": a compartmentalized cyber strategy designed for mission specialization and attribution resistance.
Andariel

OFAC sanctioned Song Kum Hyok (Andariel) and others for orchestrating North Korea's remote IT worker scheme, which used stolen identities to fund DPRK weapons programs.

Uncover the sophisticated RID Hijacking technique used by the Andariel threat group. Learn how this technique allows attackers to escalate privileges during breaches.

Learn about the stealthy keylogger malware used by the North Korean APT group Andariel to infiltrate and harvest sensitive information from U.S. organizations.

Symantec's Threat Hunter Team unveils the persistence of Stonefly, a North Korean cyberespionage group, in targeting U.S. organizations despite recent indictments.

Learn about the escalating cyberattacks on South Korea's construction and engineering sectors and how cybercriminal groups are exploiting VPN vulnerabilities.

Uncover the alarming connection between a North Korean hacker, ransomware attacks on hospitals, and state-sponsored cyber espionage campaigns.

Discover how APT45 Andariel, a notorious North Korean hacker group, stole confidential information on weapon systems and technologies.

LilacSquid deploys a series of malicious tools, including MeshAgent, a customized version of QuasarRAT, dubbed "PurpleInk,"

A North Korean hacking organization known as Andariel has been wreaking havoc in the digital realm, stealthily infiltrating South Korean firms