 Do Son
Singapore CSA warns of active attacks and public PoC code for CVE-2026-119618, a critical Apache RCE flaw in mod_http2. Update to 2.4.71 immediately.
apache
Update Apache HTTP Server to 2.4.71 now to fix CVE-2026-119618, a critical mod_http2 remote code execution flaw, alongside CVE-2026-106023.
Apache Commons Codec 1.23.0 addresses CVE-2026-119078 and CVE-2026-124077, while Apache HTTP Server 2.4.70 fixes a heap buffer overflow.
35 Apache vulnerabilities fixed, including Apache ZooKeeper flaws CVE-2026-115448 and CVE-2026-100252, plus OpenOffice, ActiveMQ and Juneau bugs.
The ASF patched Apache security vulnerabilities with new Apache security fixes for Syncope, Arrow, and Fineract, including critical flaw CVE-2026-64618.
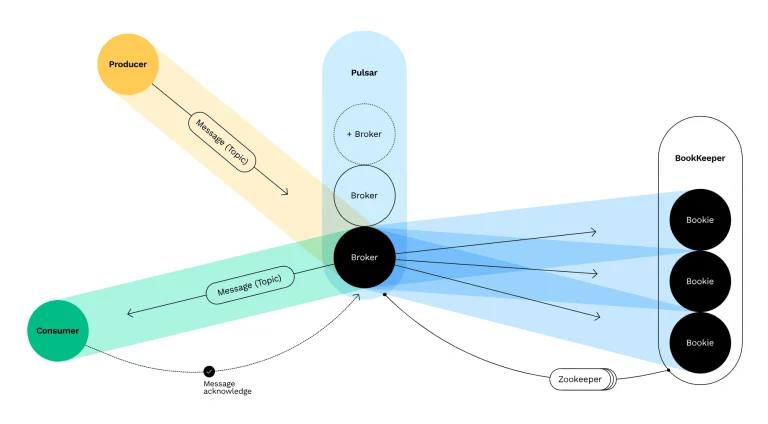
Patch 13 Apache Pulsar vulnerabilities and 4 Apache IoTDB flaws now, including critical bugs CVE-2026-105944, CVE-2026-105869, and CVE-2026-59229.
Upgrade to Apache bRPC 1.18.0 to patch 35 Apache bRPC vulnerabilities, including high-severity flaws CVE-2026-48830 and CVE-2026-56388.
Six Apache DolphinScheduler vulnerabilities, including CVE-2026-71896 and Kubernetes credential leak CVE-2026-71895, are fixed in 3.4.3.
Two Apache Jackrabbit vulnerabilities, including critical session hijack flaw CVE-2026-92414 (CVSS 9.3), are fixed. Upgrade to 2.23.6 now.
Apache Thrift 0.25.0 fixes 61 Apache Thrift vulnerabilities, including critical heap overflow CVE-2026-91135. Upgrade every binding now.
Unpatched Apache OpenOffice vulnerability CVE-2026-59265 runs code via crafted files. Apache Directory LDAP API and Traffic Server fixes out.
Apache HTTP Server 2.4.69 fixes 20 flaws, including CVE-2026-63292, a mod_vhost_alias stack overflow that may enable code execution.
Apache patched critical Apache Storm vulnerabilities. Update to fix Apache Storm vulnerabilities causing root privilege escalation and arbitrary file reads.
An unpatched Log4j RCE vulnerability was publicly disclosed on Apache's issue tracker. No CVE is assigned and no fix exists yet. Workaround inside.

An Apache InLong SQL injection flaw, CVE-2026-63038, lets attackers inject SQL via multiple parameters. Two more bugs join it. Upgrade to 2.4.0.

Three Apache Fineract SQL injection flaws (CVE-2026-57821, CVE-2026-56287, CVE-2026-35152) let authenticated users exfiltrate data. Upgrade to 1.15.0.

Apache OpenMeetings vulnerability CVE-2026-49488 lets room moderators perform arbitrary file read and steal server secrets. Upgrade to version 9.1.0.

Apache HttpComponents Core vulnerabilities CVE-2026-54399 and CVE-2026-54428 allow remote denial of service through memory exhaustion. Upgrade now.

New "directory shadowing" malware creates physical folders to hijack WordPress URLs. It feeds gambling spam to Googlebots while staying invisible.
Log4j’s Security Blind Spot: New TLS Flaw Lets Attackers Intercept Sensitive Logs Despite Encryption

Log4j’s Security Blind Spot: New TLS Flaw Lets Attackers Intercept Sensitive Logs Despite Encryption
A new Log4j flaw (CVE-2025-68161) breaks TLS hostname verification, allowing Man-in-the-Middle attacks on log data. Upgrade to v2.25.3 now.

A critical LPE flaw (CVSS 9.1) in Plesk's Password-Protected Directories allows Apache configuration injection. Any Plesk user can execute root commands and achieve full server takeover. Update immediately.

Apache HTTP Server 2.4.64 patches 8 vulnerabilities, including HTTP Response Splitting, SSRF, DoS, and TLS desync attacks. Upgrade immediately!