
 Do Son
Learn about the latest Screening Serpens cyberattacks exposed by Unit 42. Discover their new RAT variants and advanced defensive evasion tactics.
APT group

Kaspersky unmasks HoneyMyte's 2025 campaign, using the ProjectConfiguration.sys kernel rootkit to deploy ToneShell backdoors with elite stealth.

A new report uncovers 45 previously unknown domains linked to the Chinese APT group Salt Typhoon. The findings reveal a long-term, multi-year espionage infrastructure.

A new report reveals Noisy Bear, an APT group targeting Kazakhstan’s oil and gas sector with spear-phishing and multi-stage malware, mimicking internal communications.

A new Group-IB report reveals ShadowSilk, a hybrid Chinese and Russian-speaking threat cluster that uses Telegram bots for cyber espionage against Central Asian governments.

A data leak from an alleged North Korean APT group's workstation has revealed its use of a commercial proxy service, offering a rare look into its anonymizing infrastructure.


The SideCopy APT group is evolving its tactics, using new methods like MSI packages and custom malware to target critical Indian sectors, including railways and oil & gas

CRIL identified a sophisticated campaign employing a tiny, stealthy backdoor, now suspected to be the work of the infamous Turla APT group
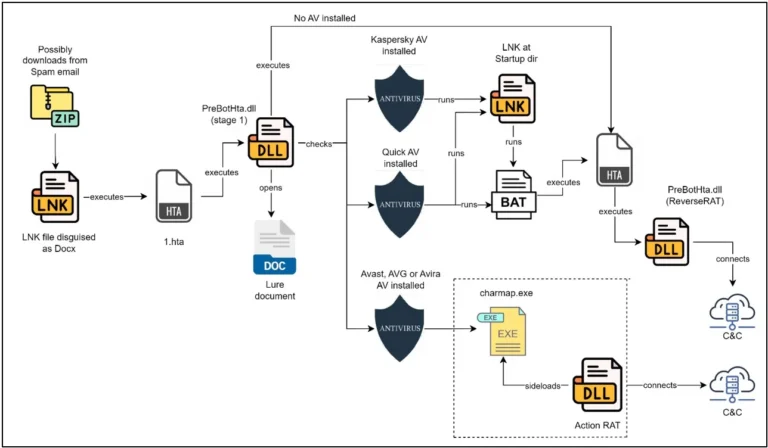
Upon further investigation, CRIL uncovered the use of malicious LNK files in the SideCopy malware campaign. These files, once executed