 Do Son
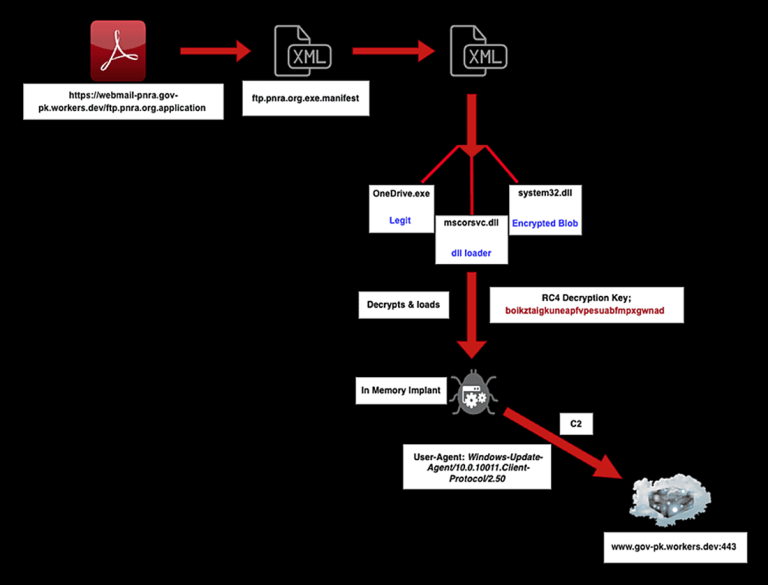
Arctic Wolf details a year-long cyber espionage campaign by Sloppy Lemming, deploying the custom BurrowShell malware against Pakistan and Bangladesh.
APT

Lotus Blossom compromises Notepad++ infrastructure to deploy "Chrysalis" malware. Rapid7 reveals the group using Microsoft Warbird to evade detection.

North Korea's LABYRINTH CHOLLIMA splits into 3 units: GOLDEN, PRESSURE, & Core. CrowdStrike reveals new strategy targeting crypto & defense.
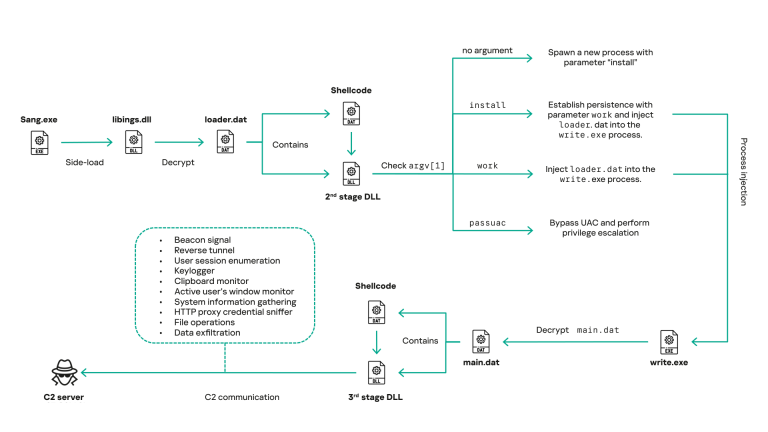
HoneyMyte (Mustang Panda) shifts to real-time surveillance using updated CoolClient. New 2025 campaign uses Pixeldrain for stealthy exfiltration.

Nomad Leopard targets Afghan officials with fake ministry docs. SEQRITE reveals how the "afghanking777000" OPSEC fail exposed the spies.

Genians reveals "Operation Poseidon": Konni APT exploits Google & Naver ad redirects to bypass defenses and deploy EndRAT.

KnownSec leak exposes a "vertically integrated espionage stack." See how ZoomEye and GhostX power China's state-aligned cyber operations.

Mustang Panda targets US gov with new LOTUSLITE backdoor. Campaign uses Venezuela lures and DLL sideloading to evade detection.

Cisco Talos warns: China-linked UAT-8837 targets North American infrastructure using zero-days (CVE-2025-53690) & open-source tools.

Cisco Talos reveals UAT-7290, a China-nexus group targeting global telecoms. They act as both spies and infrastructure builders for other hackers.

The Forum Troll APT is targeting Russian scholars with highly personalized phishing lures and the Tuoni framework disguised as plagiarism reports.

Salt Typhoon operators, former Cisco Academy students, breached 80+ telecos and CALEA systems to harvest calls from high-profile targets. The report highlights the risk of corporate tech training in geopolitics.
Ashen Lepus (Hamas-APT) significantly evolved during the conflict, deploying the AshTag modular .NET malware suite. It uses in-memory execution and Rclone for stealthy cyber-espionage against diplomatic targets in the Middle East.

A sophisticated new malware, EtherRAT, leverages Ethereum smart contracts for covert C2 (EtherHiding) 48 hours after the React2Shell (CVSS 10.0) flaw. Analysis shows ties to North Korean APTs.

Chinese APT Silver Fox is using a Cyrillic false flag in an SEO poisoning campaign impersonating Microsoft Teams. The attack installs ValleyRAT for espionage and financial fraud.
FortiGuard exposed UDPGangster, a custom UDP backdoor deployed by MuddyWater APT. The malware evades network defenses and analysis by using UDP for C2 and checking for single-core CPUs/low RAM.
China-linked APT UNC5174 is using a Go-based backdoor that abuses the Discord API as a covert C2 channel. This method allows the lightweight malware to execute arbitrary commands and evade traditional firewall monitoring.

Amazon exposed Chinese APTs exploiting the React2Shell zero-day (CVE-2025-55182, CVSS 10.0) hours after disclosure. Earth Lamia and Jackpot Panda are actively targeting unpatched Next.js servers for reconnaissance.

Patchwork APT deployed StreamSpy, a new trojan that uses WebSocket for covert C2 and HTTP for file transfer, blending malicious activity with web traffic to evade detection during espionage operations.
Bloody Wolf APT is targeting Central Asia using custom Java droppers to deploy the NetSupport RAT. The group uses geo-fencing and fake Ministry of Justice lures to achieve stealthy, persistent access for espionage.

Kaspersky exposed ToddyCat APT's evolution: the group steals M365 OAuth tokens from memory and uses TCSectorCopy to steal locked Outlook OST files, allowing covert access to cloud email outside the perimeter.

Threat actors are actively exploiting a new WSUS RCE flaw (CVE-2025-59287) to gain SYSTEM shells and deploy the dangerous ShadowPad backdoor. Patch immediately!