 Do Son
A GitLab critical vulnerability, CVE-2026-97229 (CVSS 10.0), allows unauthenticated arbitrary code execution. Upgrade to GitLab 19.4.2 now.
Arbitrary Code Execution
Apple patched an exploited Apple zero-day vulnerability. Learn how this Apple zero-day vulnerability impacts devices and install emergency updates now.
An Adobe Commerce vulnerability, CVE-2026-75650 (CVSS 10), enables unauthenticated arbitrary code execution and is exploited in the wild. Patch now.
Three critical Adobe Campaign Classic flaws (CVE-2026-76197, CVSS 10.0) allow arbitrary code execution. Update to build 9401 now.
CVE-2026-19001 (CVSS 9.5) headlines 32 MongoDB security vulnerabilities, including a BI Connector ODBC Driver flaw enabling arbitrary code execution.
Adobe patched critical Adobe Campaign Classic flaws. CVE-2026-48331 scores CVSS 10.0 and enables arbitrary code execution. Update to build 9399 now.
Adobe Campaign Classic flaw CVE-2026-48449 scores a perfect CVSS 10.0 and allows arbitrary code execution. Update to build 9398 now.
CVE-2026-45293 is an arbitrary code execution flaw in WordPress Coding Standards, rated CVSS 8.6. The dev tool has 46M+ installs. Upgrade to 3.4.1.
JetBrains patched 18 vulnerabilities across its IDEs. CVE-2026-64812 and CVE-2026-64813 reach CVSS 10, and most of the rest allow arbitrary code execution.
Ubuntu Pro Client vulnerability CVE-2026-11386 (CVSS 9.0) lets a spoofed contract server inject APT sources and run code with root privileges.
A critical HPLIP vulnerability, CVE-2026-14544 (CVSS 9.8), lets a remote attacker gain arbitrary code execution via crafted print data. Patch now.
A PAN-OS buffer overflow, CVE-2026-0288, enables arbitrary code execution on Palo Alto firewalls. Patch now.
Foxit fixed 28 flaws in Foxit PDF Reader and PDF Editor. Twenty allow arbitrary code execution via crafted PDFs. Update to 2026.1.2 now.
A critical CVSS 10 ColdFusion arbitrary code execution flaw (CVE-2026-48282) is actively exploited in the wild. Update immediately to prevent attacks.
Two UltraVNC repeater vulnerabilities enable arbitrary code execution (CVE-2026-7840) plus admin access via a hardcoded password. Update now.
Eleven Adobe ColdFusion vulnerabilities include six CVSS 10 arbitrary code execution flaws. Patch ColdFusion 2025 and 2023 now.

A critical CodeIgniter vulnerability (CVE-2026-48062, CVSS 9.8) lets attackers bypass upload checks and trigger arbitrary code execution. Update now.

A critical Mistral policy bypass flaw allows arbitrary code execution. Learn how to patch your workflow service to prevent security credentials theft.

Urgent: A memory corruption flaw in MongoDB time-series collections (CVE-2026-8053) enables server takeover. Patch to versions 8.3.2, 8.0.23, or 7.0.34 now.
A critical 9.4 CVSS vulnerability in protobuf.js puts 220 million monthly downloads at risk of RCE. Patch your Node.js and browser apps to version 8.0.1+.
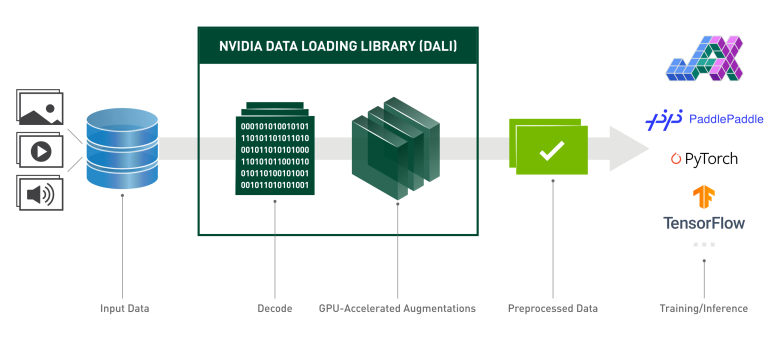
NVIDIA patches high-severity flaws in DALI and Triton Inference Server. Prevent arbitrary code execution and DoS—upgrade to DALI v2.0 and Triton r26.02 now.
Netwrix issues an urgent advisory for critical vulnerabilities in its Password Secure platform allowing arbitrary code execution. Update to v26.3.100 now.