 Do Son
Synology fixed 8 DSM vulnerabilities, including two critical unauthenticated flaws (CVE-2026-13684, CVE-2026-13639) on DiskStation Manager. Update now.
Arbitrary File Write
CVE-2026-18051 (CVSS 10) is an unauthenticated arbitrary file write in W3 Total Cache, exposing 900k+ WordPress sites. Update to 2.10.5.
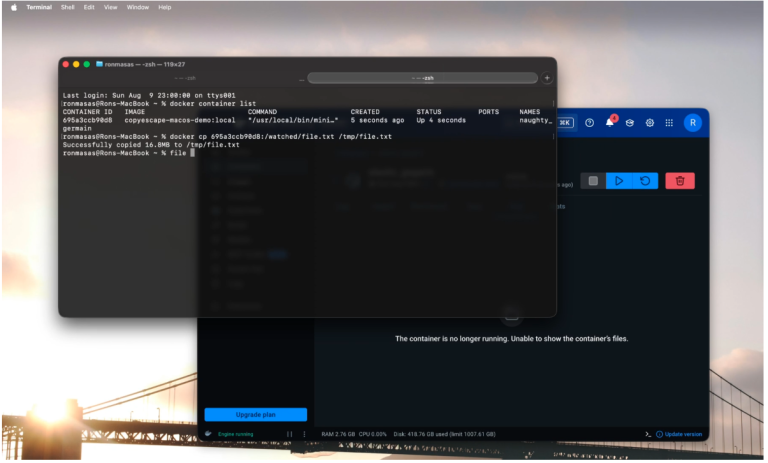
CVE-2026-17106 (CVSS 7.1) is the Docker CopyEscape vulnerability, letting malicious containers overwrite host files and trigger code execution.
PHP Composer patched three flaws, including CVE-2026-59948, an arbitrary file write that can run code outside your project. Update to 2.10.2 or 2.2.29.
A decompress npm vulnerability (CVE-2026-53486, CVSS 9.1) lets crafted archives write files outside the target folder via path traversal. Patch now.
Three Apache IoTDB vulnerabilities include a critical path traversal (CVE-2026-24014) and an authentication bypass. Upgrade to 2.0.8 now.
A critical Feast Feature Server flaw (CVE-2026-23537) lets unauthenticated attackers perform arbitrary file write and risk remote code execution. Act now.
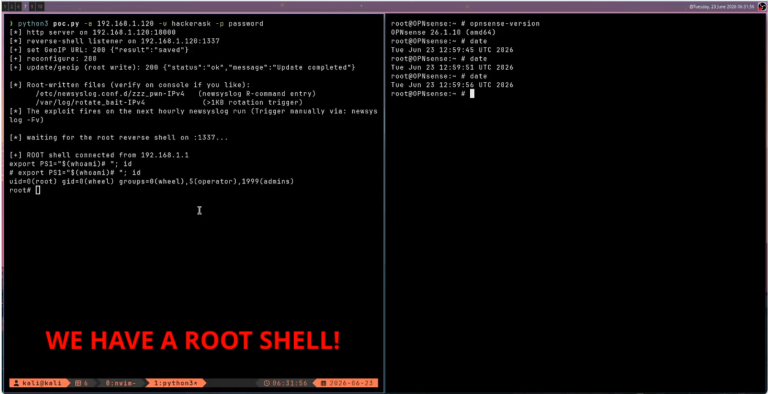
OPNsense root RCE flaws are public with PoC code. CVE-2026-57155 (9.9) chains an arbitrary file write to root. Patch 26.1.11 or 26.4.1p1 now.
Cisco warns CVE-2026-20262, a Cisco SD-WAN vulnerability enabling arbitrary file write, is exploited in the wild. Patch SD-WAN Manager now.
Urgent: Casdoor IAM platform hit by critical file write flaw (CVE-2026-44213). Attackers can bypass sandboxes to overwrite databases and gain host access.
Roundcube v1.6.14 patches a critical pre-authentication file write flaw and account hijacking bugs. Secure your webmail server with this high-priority update.
Two critical flaws in Langflow (CVE-2026-33017 & CVE-2026-33309) allow unauthenticated remote code execution and arbitrary file writes. Secure servers now.

Microsoft warns of critical flaw CVE-2026-25592 (CVSS 10.0) in Semantic Kernel SDK. AI agents can overwrite system files. Update to v1.70.0 now.

Critical ASUSTOR ADM flaw CVE-2026-24936 (CVSS 9.5) allows remote file overwrite. Unauthenticated attackers can seize NAS control. Update to v5.1.2 now.

CVE-2026-21440: A critical 9.2 flaw in AdonisJS file uploads allows attackers to overwrite system files and gain RCE. Update to v10.1.2 immediately!

Ivanti patched four severe flaws in EPM 2024 SU4. A Critical XSS (9.6) allows admin hijack, and an unauthenticated file write (8.8) risks RCE. Update to 2024 SU4 SR 1 immediately.

A critical hardware attack, TEE.fail, uses low-cost DDR5 memory bus interposition to extract root attestation keys from Intel TDX and AMD SEV-SNP. The flaw affects core server-grade TEEs.

Researchers from Exodus Intelligence, led by Michele Campa, have disclosed a privilege-escalation vulnerability in Microsoft’s Cloud Files...

A path traversal flaw (CVE-2025-62725) in Docker Compose lets attackers overwrite host files via remote OCI artifact annotations, triggered by read-only commands.

Atlassian patched a Critical (CVSS 8.7) Path Traversal flaw (CVE-2025-22167) in Jira Software/Service Management that allows attackers to perform arbitrary file writes. Immediate update is urged.

Flowise patched a Critical (CVSS 10.0) RCE flaw (CVE-2025-61913) in WriteFileTool. Authenticated attackers can write arbitrary files to the filesystem to gain command execution.

A new report reveals a critical flaw in Harness Gitness that allows authenticated attackers to write arbitrary files to the server, risking a full system compromise.