 Do Son
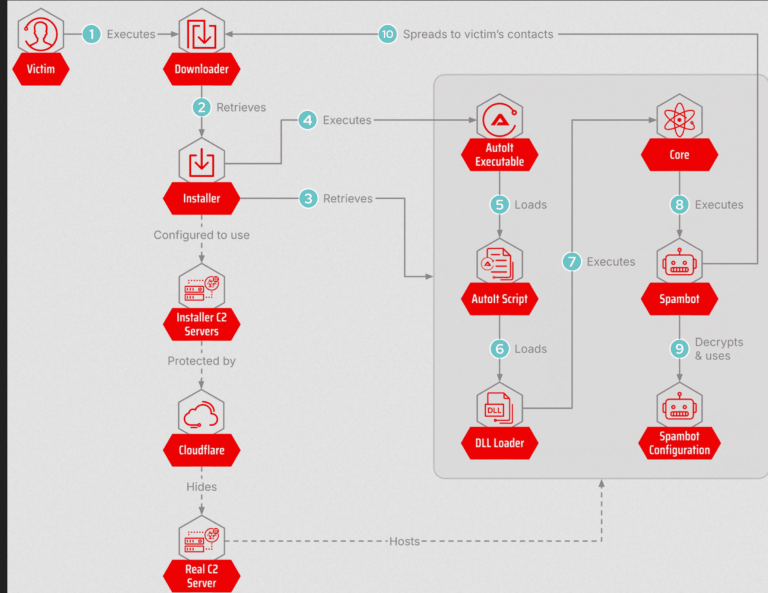
Astaroth's new WhatsApp spambot auto-messages every victim contact in Brazil using a hidden browser, quietly turning each victim into a malware distributor.
Astaroth

New Astaroth campaign "Boto Cor-de-Rosa" uses a Python worm to hijack WhatsApp Web. It auto-messages your contacts to spread banking malware globally.

Sophos exposed STAC3150, a campaign using fake "View Once" messages to deploy Astaroth banking trojan. The malware hijacks WhatsApp Web sessions via WPPConnect/Selenium for self-propagation.
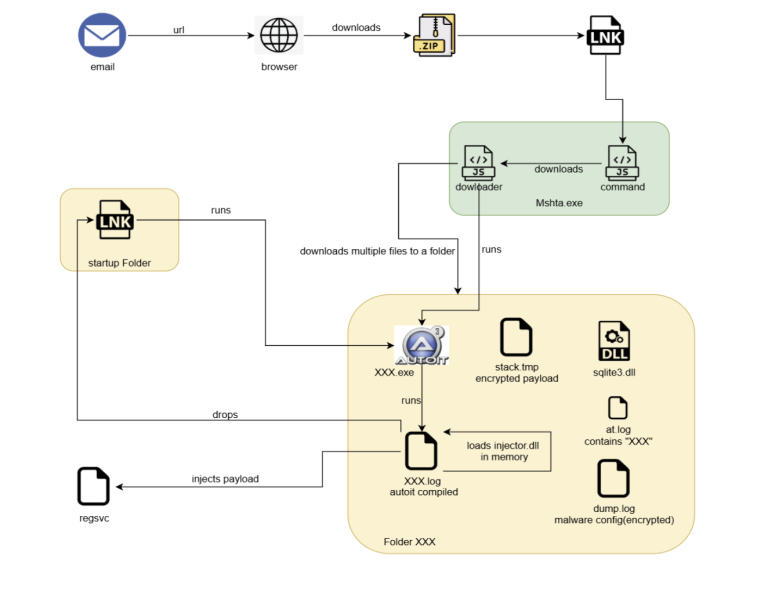
McAfee uncovered the Astaroth banking Trojan using GitHub for C2 backup, hiding encrypted configuration data via steganography in images to target Brazilian financial and crypto users.
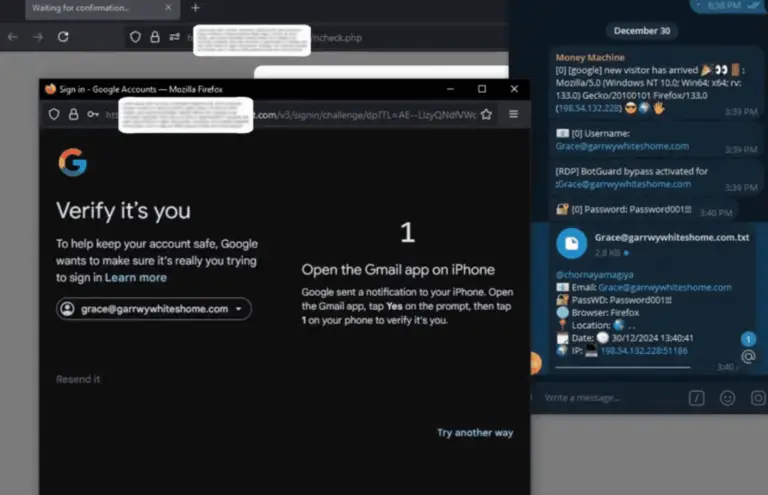
Uncover the dangers of the Astaroth Phishing Kit, which bypasses two-factor authentication to steal sensitive credentials.

Discover the Water Makara spear-phishing campaign targeting companies in Brazil. Find out how to identify and protect against this dangerous threat.

These campaigns focus heavily on Latin America, notably targeting victims with the notorious Astaroth, Mekotio, and Ousaban trojans