 Do Son
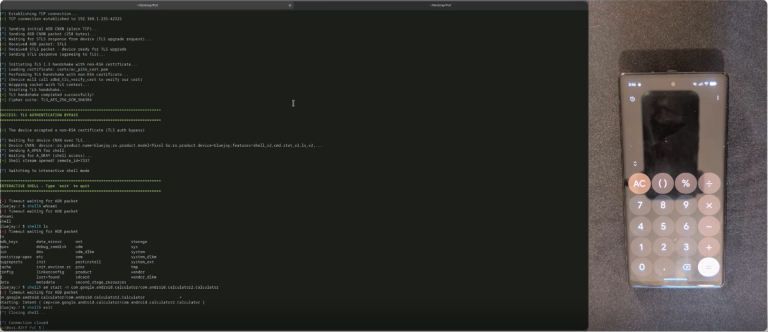
BARGHEST reveals CVE-2026-0073: a zero-click Android ADB bypass over Wi-Fi. Public PoC and exploit details are now live. Secure your mobile device today!
Auth Bypass

CISA adds 8 vulnerabilities to the KEV Catalog, including Cisco, PaperCut, and Zimbra flaws. Actively exploited threats require immediate patching.

WSO2 patched three Critical flaws (CVSS 9.8) in API Manager/Identity Server. Flaws in regex access control and case-sensitive HTTP methods allow unauthenticated administrative takeover.

WSO2 patched two Critical flaws: CVE-2025-10611 (CVSS 9.8) allows unauthenticated admin bypass of System REST APIs, and CVE-2025-9804 (CVSS 9.6) allows privilege escalation via SOAP services.

Rockwell issued an urgent fix for a Critical (CVSS 10.0) auth bypass in its 1783-NATR router (CVE-2025-7328). The flaw allows remote admin takeover and configuration disruption.

GitLab patched two high-severity flaws: CVE-2025-11340 (Auth Bypass) allows API write access with read-only tokens, and CVE-2025-10004 permits unauthenticated DoS via GraphQL.