 Do Son
Patch two Barracuda vulnerabilities, CVE-2026-116606 and CVE-2026-111560, that allow attackers to gain Barracuda root access across multiple appliances.
Authorization Bypass
Patch CVE-2026-110720 now. This 9.9 CVSS consul-k8s vulnerability enables a cross-namespace authorization bypass in ACL binding rules.
Six Apache DolphinScheduler vulnerabilities, including CVE-2026-71896 and Kubernetes credential leak CVE-2026-71895, are fixed in 3.4.3.
Octopus Deploy addressed critical Octopus Server vulnerabilities involving a CVSS 8.7 remote code execution. Apply the security patches to prevent attacks.
A critical HPE EdgeConnect authorization bypass (CVE-2026-76670) enables full system compromise. Patch this HPE EdgeConnect authorization bypass now.
MongoDB fixed 24 MongoDB Server vulnerabilities, including a critical auth bypass (CVE-2026-82067) and unauthenticated denial of service flaws. Patch now.

Four OpenDJ vulnerabilities are patched in 5.1.2. They include a CVSS 9.6 authorization bypass and an unauthenticated SSRF scoring CVSS 9.4.


CERT/CC warns of a Plane authorization bypass, CVE-2026-15342. It lets users reach other workspaces' files, and no patch exists yet.
CVE-2026-55518 is a critical Avo authorization bypass flaw enabling privilege escalation in Ruby on Rails admin panels. Update to Avo 3.32.1 now.

Apache Camel K fixes CVE-2026-45760, a critical cross-namespace "Build Deputy" flaw allowing authorized users to hijack pods in secure namespaces.
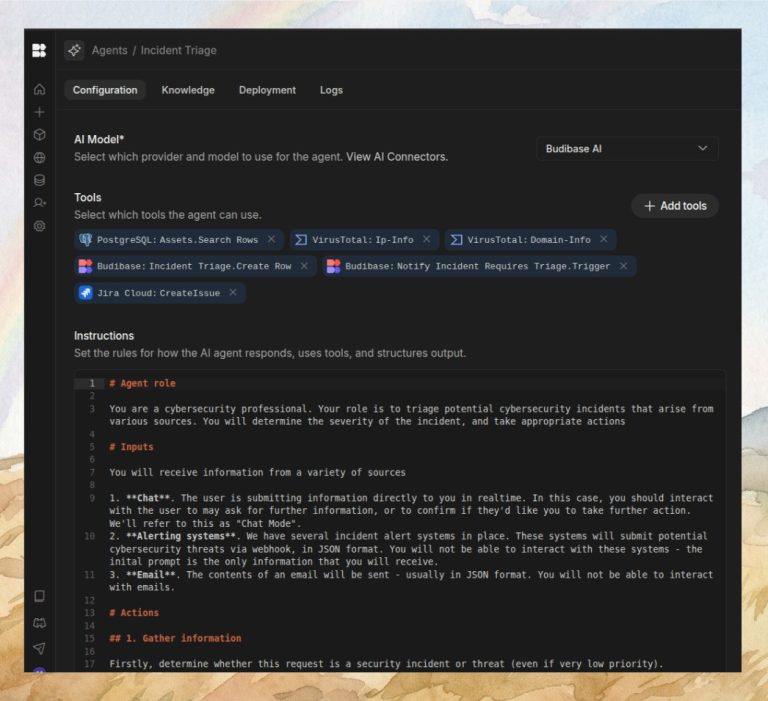
Budibase patches a critical 9.9 CVSS SCIM authorization bypass (CVE-2026-46425). Basic users can delete admins and hijack accounts. Update now!

pgAdmin 4 v9.15 fixes a 9.4 CVSS auth bypass and multiple RCE flaws. Attackers can execute OS commands via SQL tools. Upgrade your pgAdmin server now!

ArcadeDB 26.4.1 fixes a critical 9.0 CVSS authorization bypass (CVE-2026-44221) that dismantles database isolation. Secure your multi-model data and patch now!

Spring Security reveals 7 flaws, including a critical 9.6 CVSS vulnerability in version 7.0. From auth bypass to X.509 impersonation, upgrade to 7.0.5 now.

Apache NiFi 2.9.0 fixes a high-severity RCE (CVE-2026-39816) in the Tinkerpop service. Secure your data pipelines and verify your annotations today!

Dgraph patches a critical 10.0 CVSS flaw (CVE-2026-33976). Unauthenticated attackers can overwrite databases and read local files. Update to v25.3.1 now!
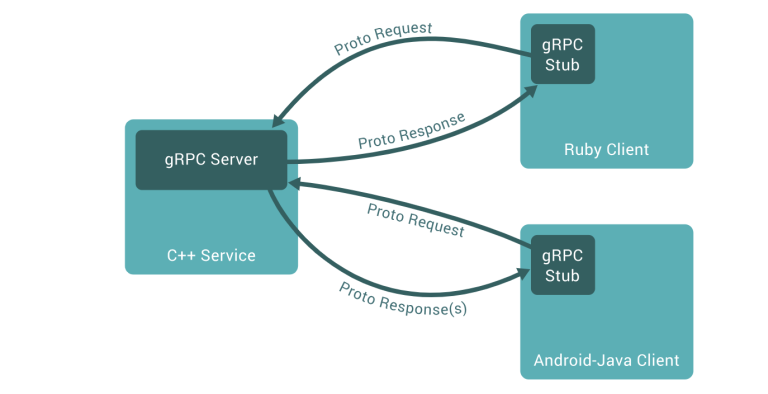
A critical 9.1 CVSS flaw in gRPC-Go (CVE-2026-33186) allows attackers to bypass authorization by omitting a leading slash. Upgrade to v1.79.3 immediately.

Two critical 10.0 CVSS flaws (CVE-2026-30956, CVE-2026-30957) in OneUptime allow full account takeovers and Server-Side RCE. Update to 10.0.21 immediately.
Apache NiFi flaw CVE-2026-25903 allows unauthorized users to modify restricted components. Update to version 2.8.0 immediately to secure data pipelines.

Apache Solr patches moderate flaws CVE-2026-22444 & CVE-2026-22022. Vulnerabilities risk NTLM hash leaks and auth bypass. Update to v9.10.1 now.

A flaw in Apache Fineract risks Authorization Bypass via IDOR (CVE-2025-58137) in its self-service API, potentially exposing customer data. Also fixed: Weak Password Policy and Unmasked Server Keys. Update to v1.13.0.