 Do Son
Trend Micro reveals how an exposed Spring Boot Actuator and a spreadsheet of plaintext secrets led to a malware-less SharePoint data exfiltration attack.
Azure AD

Critical: ABB OPTIMAX flaw CVE-2025-14510 (CVSS 9.2) allows auth bypass via Azure AD. Attackers can shut down systems. Patch or disable SSO now.

Microsoft Authenticator will purge Entra ID credentials from jailbroken/rooted devices starting Feb 2026 to block token theft, enforcing security for enterprise accounts.
CVE-2025-55241: Microsoft Entra ID Flaw with CVSS 10.0 Could Have Compromised Every Tenant Worldwide
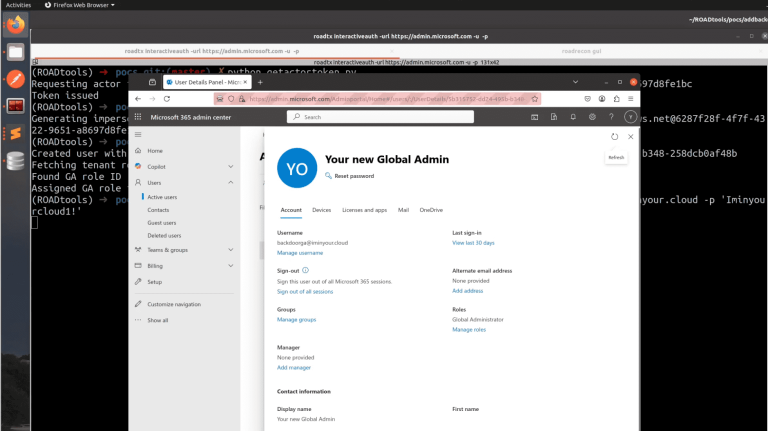
CVE-2025-55241: Microsoft Entra ID Flaw with CVSS 10.0 Could Have Compromised Every Tenant Worldwide
A critical flaw (CVE-2025-55241) in Microsoft Entra ID could have allowed a compromise of every tenant worldwide by bypassing security with "Actor tokens."

A new report reveals a dangerous misconfiguration: exposed appsettings.json files can contain Azure AD credentials, giving attackers full access to a company's cloud kingdom.

Over 50,000 Microsoft Azure AD user records from the aviation industry were exposed due to a misconfigured, unauthenticated API, revealing sensitive data and posing major risks.