 Do Son
Veeam fixes seven vulnerabilities in Veeam Backup for Microsoft 365 and Management Pack, including RCE flaws CVE-2023-22793 and CVE-2026-106076.
Backup Security
Dell fixes PowerProtect Data Domain vulnerabilities in DD OS, including four CVSS 9.8 flaws like CVE-2026-86400 allowing root command execution.
Critical Veeam Backup vulnerability CVE-2025-64393 (CVSS 9.4) enables RCE by low-privileged users. Update to 12.3.2 P4 now.
An Acronis cPanel plugin vulnerability is exploited in the wild. Acronis urges an immediate update to 1.9.3 HF3 or 1.9.4. Patch your backup plugin now.
A critical Veeam ONE vulnerability (CVE-2026-65641, CVSS 9.3) lets an unauthenticated attacker coerce SMB authentication. Patch Veeam now.
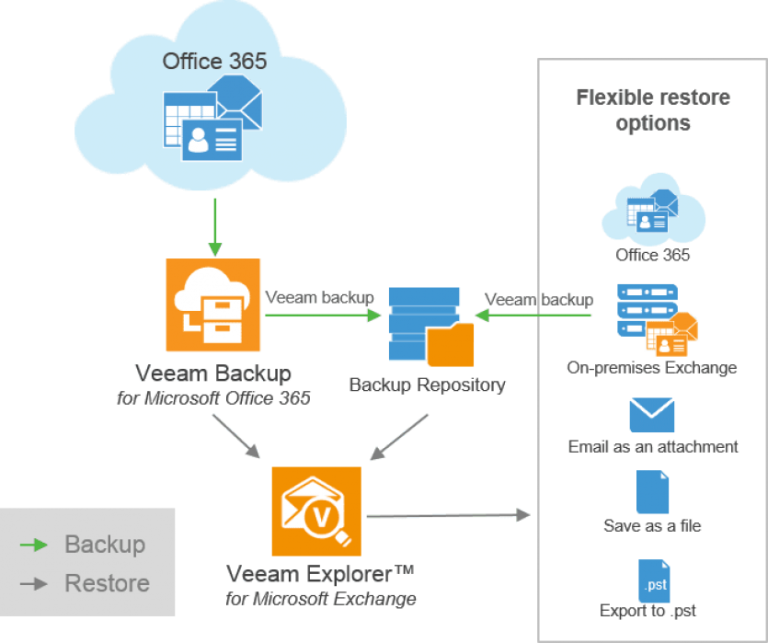
Learn about the new Veeam security vulnerabilities, including a critical 9.4 RCE flaw in Service Provider Console, and how to patch your systems.
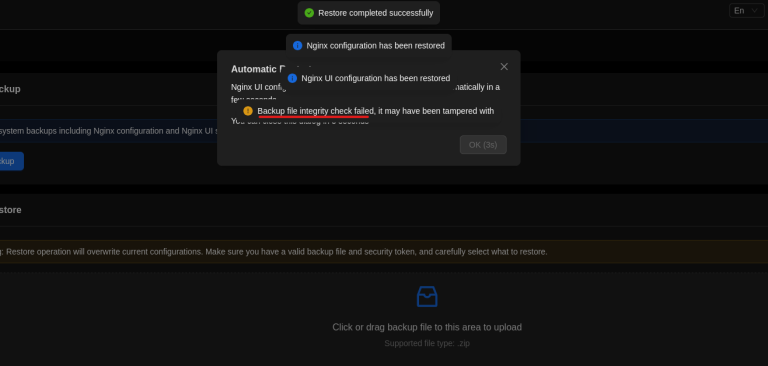
Public PoC exploit and details are out for Nginx UI’s 9.4 CVSS backup flaw (CVE-2026-33026). Attackers can hijack servers via tampered backups. Update now!

Veeam urgently patches critical 9.9 CVSS RCE flaws (CVE-2026-21666, CVE-2026-21708) in Backup & Replication 12.3.2. Update your servers immediately.

Veeam releases a critical security update fixing 9.9 CVSS RCE flaws (CVE-2026-21669, CVE-2026-21708) in Backup & Replication. Patch servers immediately.

Acronis fixes 3 critical flaws (CVSS 10.0) in Cyber Protect. Attackers can manipulate backups without auth. Update to v16 Update 4 immediately.
Veeam patched two Critical RCE flaws (CVE-2025-48983 & -48984) in Backup & Replication v12 that let authenticated domain users compromise backup infrastructure.