 Do Son
Our weekly CVE report for Oct 12-18, 2026 tracks 5,499 new flaws and 12 exploited vulnerabilities, with CISA KEV trailing by up to 8 days.
BeyondTrust
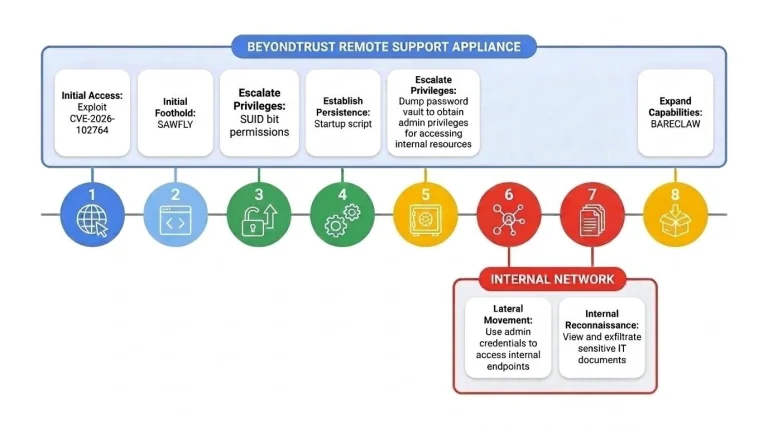
Patch CVE-2026-102764 now. This critical BeyondTrust Remote Support vulnerability is exploited in the wild as an ARMORY CASTLE zero-day.
BeyondTrust patched two high-severity EPM flaws (CVE-2026-40144, CVE-2026-40145) allowing local privilege escalation on Windows. Update to 26.1.2.
BeyondTrust patched two critical pre-authentication vulnerabilities (CVE-2026-40138, CVE-2026-40139, CVE-2026-40140). Update Remote Support instances now.

Unit 42 warns of active attacks on critical BeyondTrust flaw CVE-2026-1731. Hackers bypass auth for RCE and data theft. Patch self-hosted instances now.
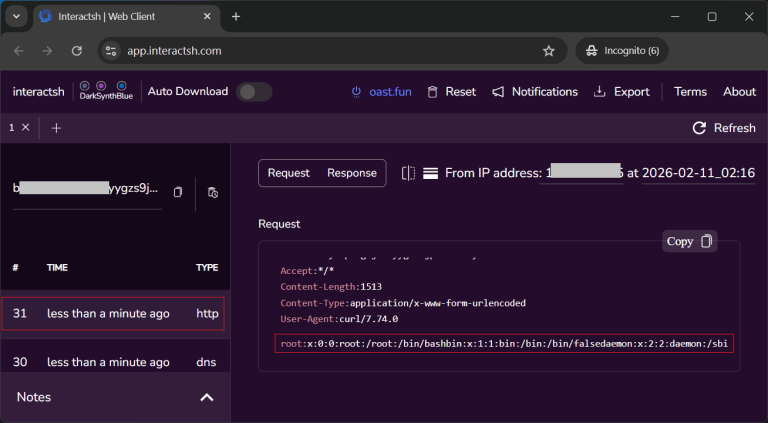
Arctic Wolf warns of CVE-2026-1731, a critical BeyondTrust flaw exploited in the wild. Attackers use it to deploy backdoors. Patch self-hosted instances now.

Critical BeyondTrust flaw CVE-2026-1731 (CVSS 9.9) allows unauthenticated RCE on Remote Support & PRA appliances. Update to v25.3.2 immediately.
BeyondTrust patches two high-severity LPE flaws (CVE-2025-2297, CVE-2025-6250) in Privilege Management for Windows, allowing local attackers to gain SYSTEM privileges via user profile manipulation and WMIC exploit.

BeyondTrust warns of a high-severity unauthenticated RCE flaw in Remote Support and PRA, exploitable via the built-in chat feature. Patch immediately

CVE-2025-0217 flaw in BeyondTrust PRA allows session hijacking via local auth bypass. Upgrade to version 25.1+ to prevent exploitation.
CVE-2025-0889 poses a serious risk. Discover how this vulnerability affects BeyondTrust Privilege Management for Windows solutions.

Urgent warning: Critical security vulnerabilities CVE-2024-12686 pose significant risks. BeyondTrust and Qlik Sense Enterprise impacted.
Protect your organization from critical command injection vulnerability CVE-2024-12356 in BeyondTrust’s Privileged Remote Access and Remote Support solutions.