 Do Son
The DOJ and FBI seized QScan and QTRouter, platforms run by China state-sponsored hackers to hide attacks on U.S. critical infrastructure.
Black Lotus Labs
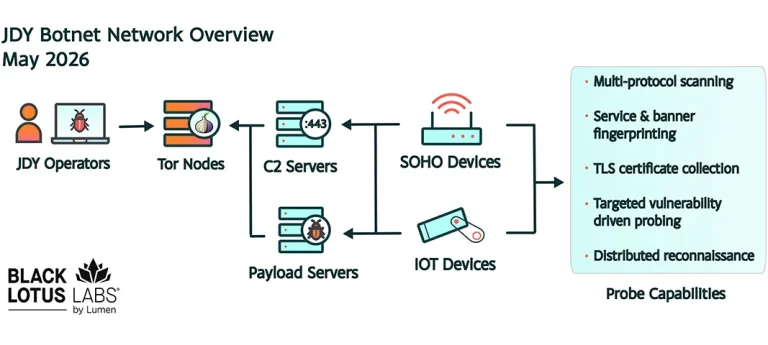
The JDY botnet, a China-nexus IoT network tied to Volt Typhoon, now spans 1,500+ devices and scans for new bugs like CVE-2026-35616 within hours.
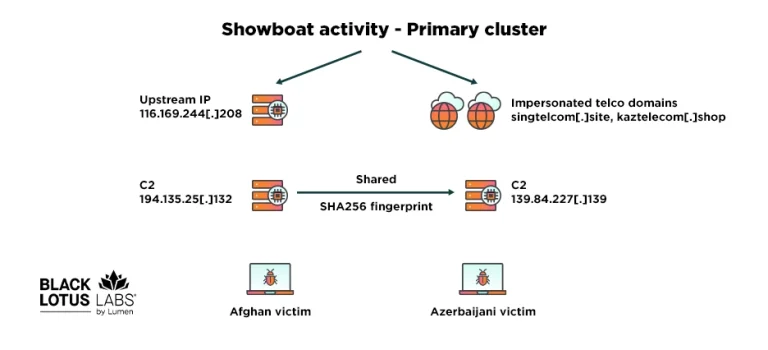
Discover the new Showboat Linux malware framework uncovered by Black Lotus Labs. Learn how PRC threat actors target telecommunications networks.
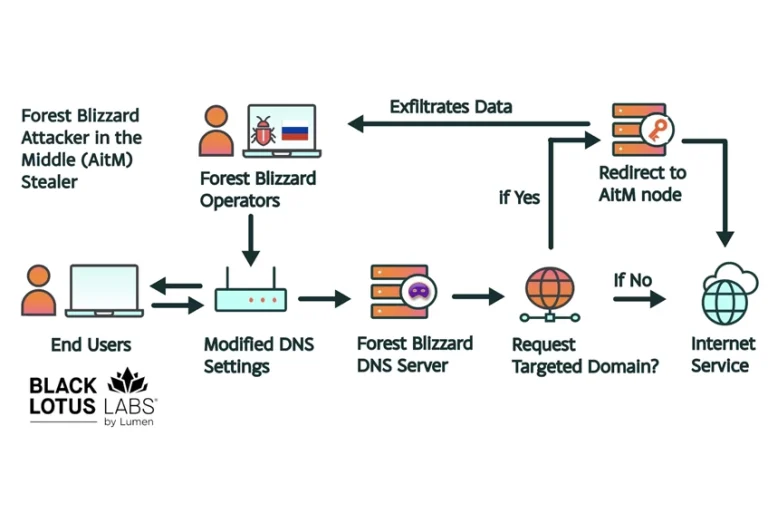
Russian-linked Forest Blizzard's FrostArmada campaign hijacked 18,000+ routers to steal OAuth tokens via DNS redirection. Learn how they stayed invisible.
Black Lotus Labs uncovers KadNap, a stealthy P2P botnet infecting over 14,000 Asus routers to fuel the Doppelgänger dark web proxy network.

A new report from Black Lotus Labs reveals SystemBC, a malware-powered proxy network. The botnet compromises VPS systems and fuels global ransomware attacks.