 Do Son
ChainDrop npm worm infected 400+ packages, stealing cloud keys and CI secrets via blockchain C2. Unit 42 details the full attack chain and fixes.
Blockchain C2

The Dysphoria botnet uses blockchain ENS/SNS domains for covert C2 and turns victims into relays. XLab tracked over 200,000 bots in this IoT DDoS botnet.
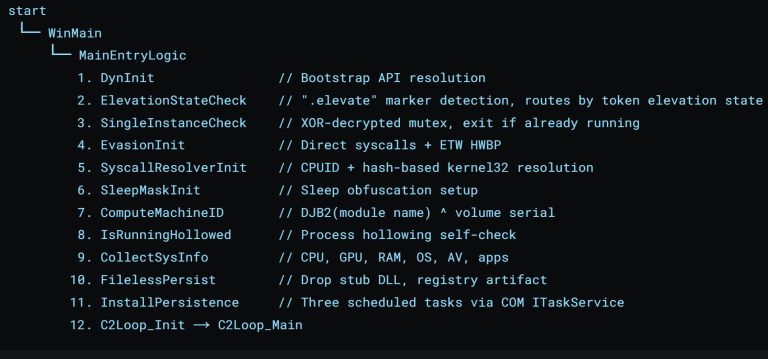
An in-depth PHANTOMPULSE malware analysis reveals a sneaky blockchain C2 channel and AI-assisted coding techniques used by advanced threats.
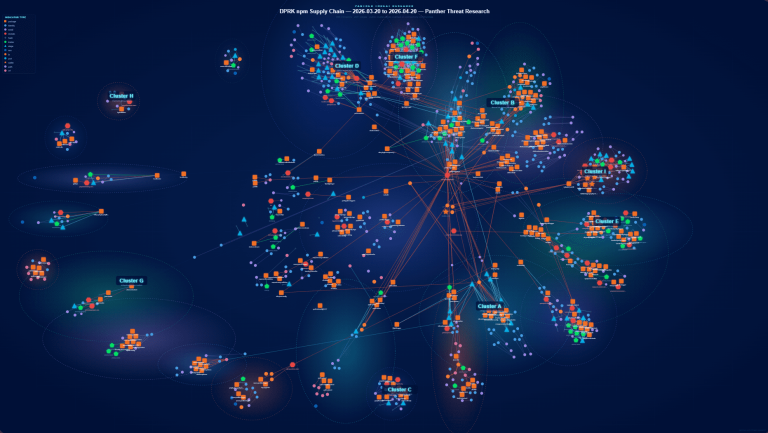
Panther Research exposes a massive 2026 DPRK npm campaign using blockchain dead-drops to steal crypto keys and AI secrets. Secure your CI/CD pipelines now.
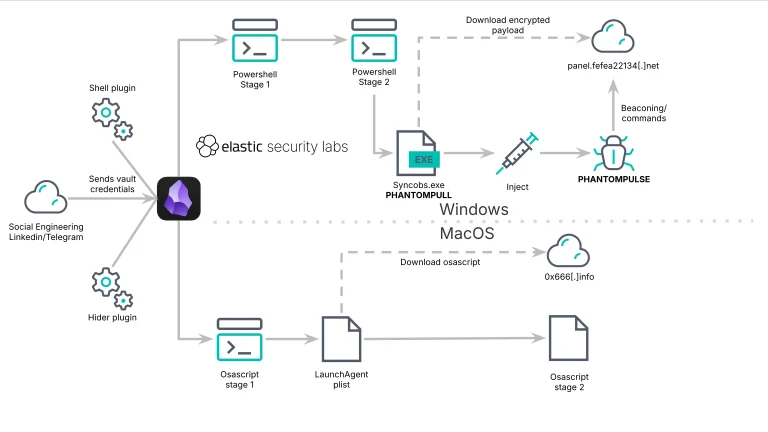
Elastic uncovers PHANTOMPULSE: A novel RAT abusing Obsidian plugins and blockchain C2. Stay safe from this AI-assisted campaign targeting crypto firms.

ASEC warns of EtherRAT, a multi-stage crypto-stealer exploiting the React2Shell flaw. It uses Node.js and Ethereum for stealthy C2. Patch now!

A sophisticated new malware, EtherRAT, leverages Ethereum smart contracts for covert C2 (EtherHiding) 48 hours after the React2Shell (CVSS 10.0) flaw. Analysis shows ties to North Korean APTs.

Kaspersky exposed Tsundere, a Node.js botnet using an Ethereum smart contract for unkillable C2 updates. The system includes a cybercrime marketplace and spreads via fake MSI game installers for RCE.