 Do Son
A researcher reported a critical PS5 hypervisor vulnerability to Sony for $50,000, triggering fierce debate and halting the PS5 Linux project.
bug bounty
Google restructures its Chrome VRP rewards, raising baseline payouts for memory corruption bugs to $2,000 and offering up to $20,000 for critical exploits.
Learn how the LLM-generated PhantomRaven information stealer targets developers. The PhantomRaven information stealer uses npm to hijack CI/CD secrets.
Discover the details of the Liquid Network hack. A white hat attacker stole 4,000 Bitcoins but returned most of the funds to force a bug bounty payment.
Apple restricts its Bug Bounty program to combat a surge of fake AI-generated vulnerability reports, instituting caps to protect critical flaw detection.
Discover how the new GitHub bug bounty program impacts researchers. The platform replaces floating ranges with fixed payouts and a lucrative VIP tier.
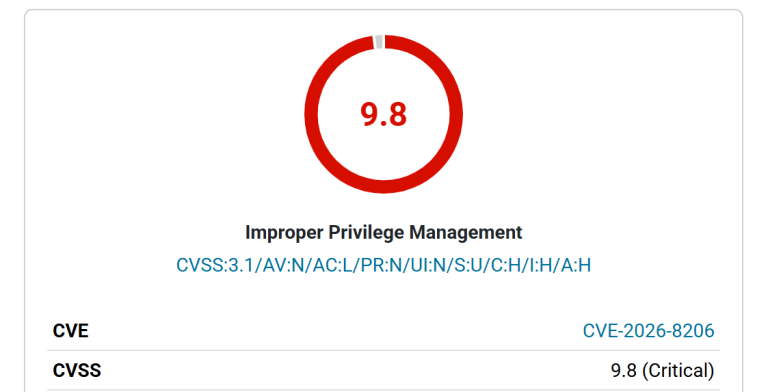
An active Kirki plugin vulnerability allows a critical WordPress account takeover. Learn how this 9.8 CVSS flaw impacts 150,000 active websites.
Chrome’s Security Overhaul: 127 Fixes and $100k+ in Bounties Power the New Chrome 148 Stable Release
Chrome’s Security Overhaul: 127 Fixes and $100k+ in Bounties Power the New Chrome 148 Stable Release
Google Chrome 148 is out with 127 security fixes, including 3 Critical flaws in Blink and V8. Protect your data—check your version and update today!
Google patches 31 Chrome flaws, including a $90K graphics engine bug. Update to version 147.0.7727.101 now to block critical sandbox escapes and RCE risks.
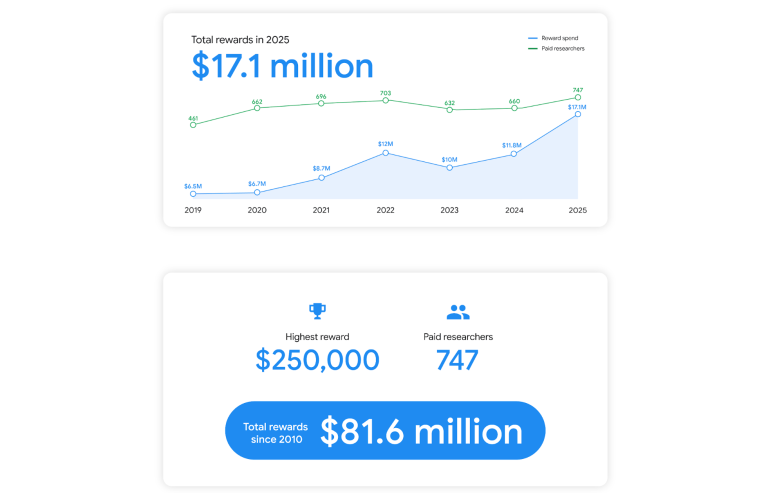
Google’s 2025 VRP hit an all-time high with $17.1M in payouts. Discover how the new AI VRP and elite bugSWAT events are shaping the future of security.
Google releases Chrome 146, fixing 29 vulnerabilities including a critical heap buffer overflow in WebML (CVE-2026-3913). Update your browser immediately.

Google has paid out its highest-ever Chrome bug bounty of $250,000 for a critical sandbox escape flaw that could bypass multiple security layers.

The cURL project's bug bounty program is overwhelmed by AI-generated, fraudulent vulnerability submissions, leading the lead developer to consider its discontinuation.

Dylan, 13, became Microsoft's youngest security researcher, uncovering a Teams flaw and prompting a Bug Bounty Program rule change. He has since submitted 20 reports.

A patched Google flaw allowed researchers to extract linked phone numbers without user notification. The vulnerability is now fixed, and no exploits were detected.

Google's research division has unveiled v8CTF, a Capture the Flag (CTF) challenge tailored specifically for its V8 JavaScript engine