 Do Son
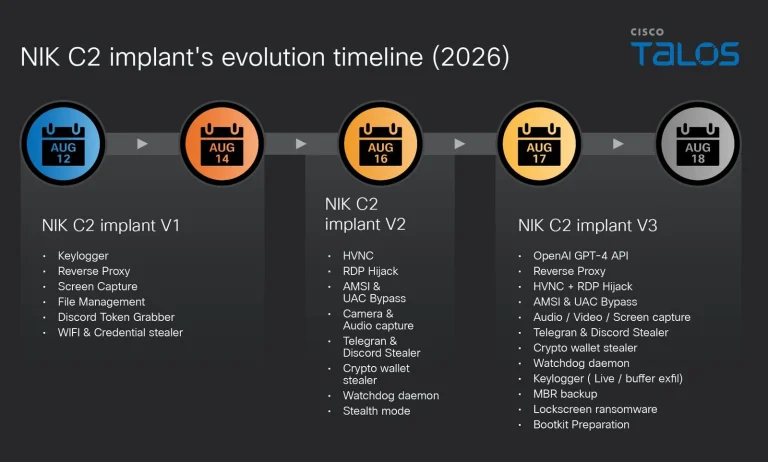
Cisco Talos uncovers the NIK C2 framework. This Windows NIK C2 framework abuses OpenAI APIs to analyze stolen victim data and deploy screen lockers.
C2 Framework

Cato CTRL intercepts "TencShell," a new stealth malware derived from open-source Rshell. Attackers use third-party access to breach networks!
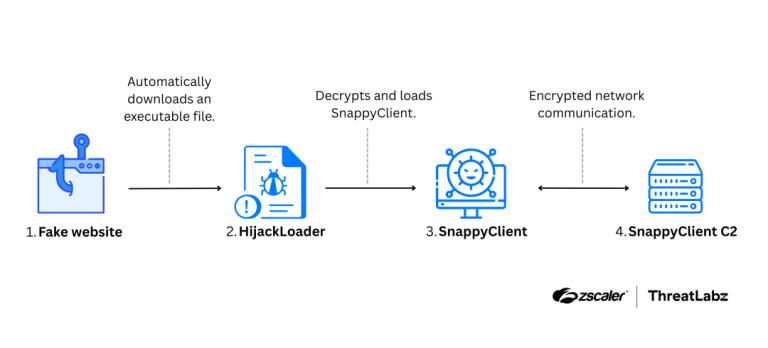
Zscaler ThreatLabz unmasks SnappyClient, a C++ C2 framework linked to HijackLoader. It uses AMSI bypass and Heaven’s Gate to steal crypto and gain remote access.

Check Point Research uncovers Storm-2603, a China-linked APT using a custom AK47C2 framework and BYOVD tactics to deploy multiple ransomware strains simultaneously.