 Do Son
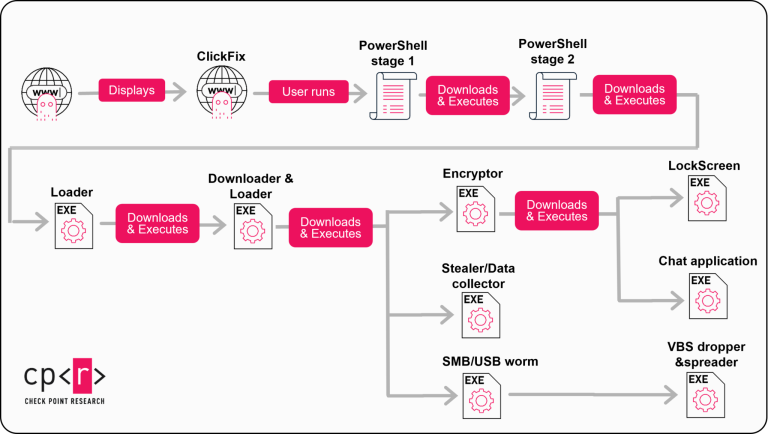
StopAndProtect malware turns hacked WordPress sites into a botnet for ransomware and data theft. Check Point exposed 5,000+ victims.
C2 Infrastructure
Sophos X-Ops uncovers a fake Claude AI site (claude-pro.com) distributing an undocumented backdoor via DonutLoader. Protect your team from AI-themed lures.

Socket identifies 108 malicious Chrome extensions stealing Telegram sessions and Google IDs. 20,000 installs hit—audit your browser extensions immediately!

Trellix ARC reveals Masjesu, a stealthy, professional IoT botnet operational since 2023. Targeted DDoS-for-hire with a low-profile strategy. Patch now!

ThreatLabz unmasks Xloader 8.7, the evolved successor to Formbook. Learn how its advanced obfuscation and decoy C2s bypass modern security defenses.
RedLine architect Hambardzum Minasyan is extradited to the U.S. to face 50 years in prison for his role in the global malware empire and Operation Magnus.
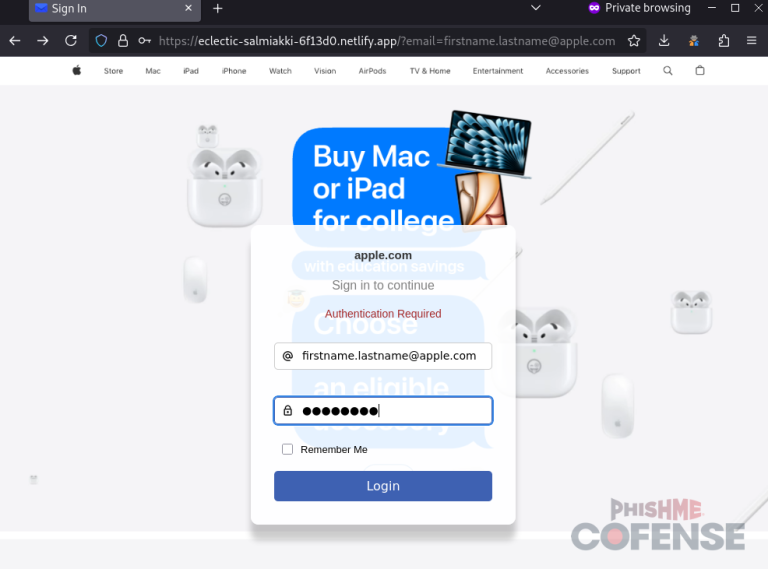
A new Cofense report reveals how hackers abuse legitimate Telegram Bot APIs to create stealthy Command and Control (C2) centers for data exfiltration.
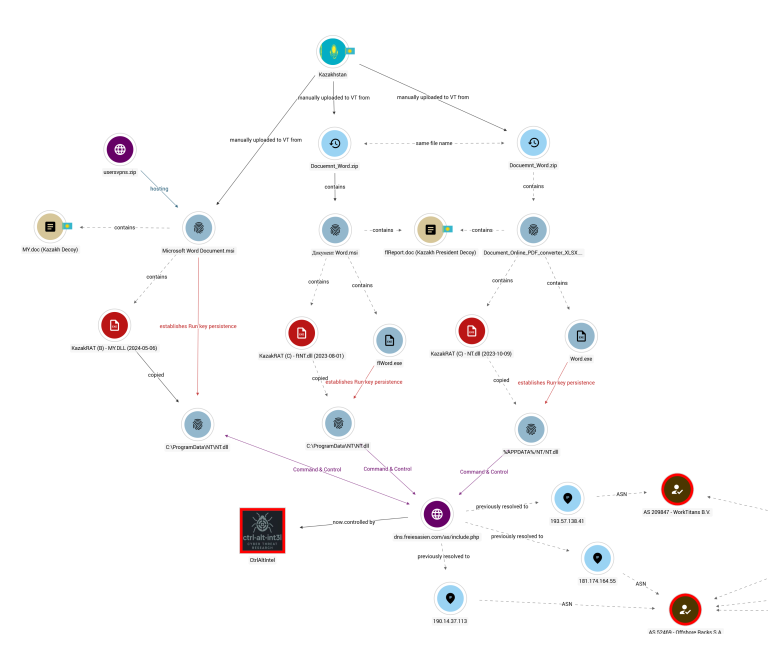
Researchers uncover "KazakRAT," a state-affiliated spyware targeting Kazakhstan & Afghanistan. A lapsed domain allowed experts to sinkhole the C2.

Group-IB uncovers DeadLock ransomware using Polygon smart contracts for resilient C2. This "EtherHiding" tactic signals a new era of blockchain abuse.