 Do Son
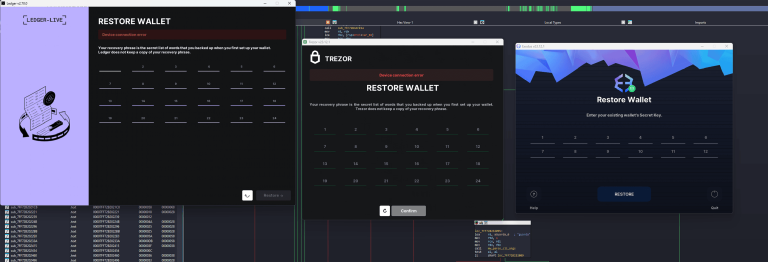
CastleLoader malware now delivers NeedleStealer, a Rust crypto wallet spoofer and Golang browser hijacker. Arctic Wolf tracks three new campaigns.
CastleLoader

LummaStealer is back, evading takedowns with "ClickFix" tactics. Bitdefender reveals how fake CAPTCHAs trick users into running malware. Stay alert.

Darktrace exposed TAG-150, a new MaaS operator compromising 469+ US devices in months. The group uses ClickFix to trick victims into running malicious PowerShell that deploys the CastleLoader/CastleRAT backdoor.