 Do Son
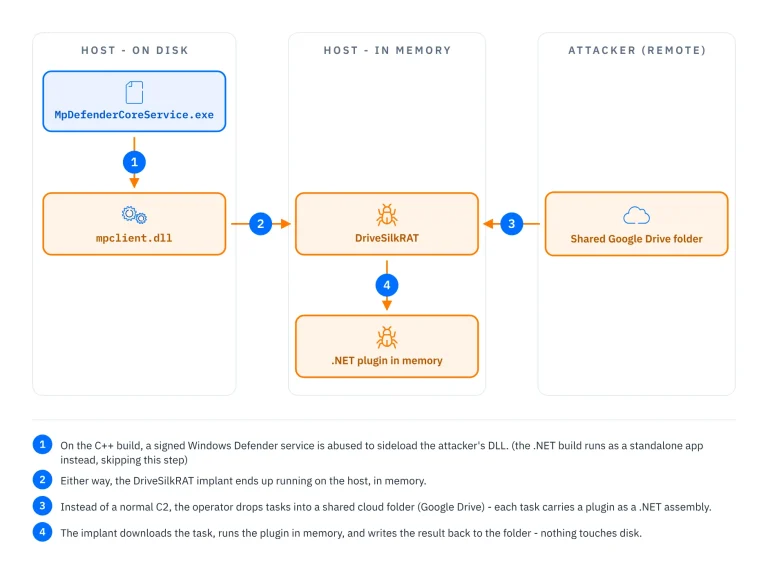
SilkParasite APT ran China-nexus cyberespionage across Central Asia, using 7 custom RATs, DLL sideloading, and AI-assisted malware.
Central Asia

Bloody Wolf APT is targeting Central Asia using custom Java droppers to deploy the NetSupport RAT. The group uses geo-fencing and fake Ministry of Justice lures to achieve stealthy, persistent access for espionage.

Seqrite exposed Silent Lynx APT targeting Central Asia and Russia with Operation Peek-A-Baku. The group uses LNK files and GitHub to deploy Laplas reverse shells and SilentSweeper for espionage intelligence.
A new Group-IB report reveals ShadowSilk, a hybrid Chinese and Russian-speaking threat cluster that uses Telegram bots for cyber espionage against Central Asian governments.