 Do Son
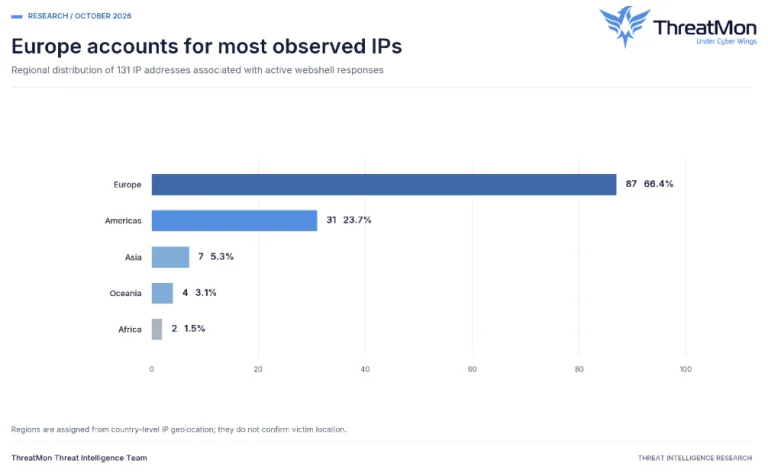
An exposed workspace shows AhsayCBS webshell access turned into SOCKS proxy tunnels with Chisel and GOST across 141 hosts, per the logs.
chisel

NightEagle APT (APT-Q-95) is exploiting an unknown Exchange zero-day to target China's strategic industries, using fileless malware and exfiltrating machineKey for remote email access.

Palo Alto Networks exposes CL-CRI-1014, an IAB targeting African financial institutions. They use open-source tools like PoshC2 and Classroom Spy, disguised with forged signatures for covert network access.

Discover the activities of the espionage cluster known as Paper Werewolf. From phishing emails to disruptive operations, learn about their tactics and targets.

Learn about a complex PowerShell campaign that employs advanced techniques to infiltrate networks, maintain persistence, and evade detection.
The CERT-UA has issued an urgent alert regarding escalated cyber activities by the notorious Russia-backed Sandworm APT group