
 Do Son
PHPUnit CVE-2026-41570 allows RCE via invisible newline injection in CI/CD pipelines. Secure your build servers—update to 12.5.22 or 13.1.6 today.
CI/CD security

Atlassian Bamboo Data Center hit by critical 9.4 RCE (CVE-2026-21571). Attackers can hijack your build pipeline. Secure your supply chain—patch now!

A massive supply-chain attack hit the European Commission via a compromised Trivy update. 340GB of data was leaked by ShinyHunters. Rotate your AWS keys!

Jenkins patches critical flaws (CVE-2026-33001 & CVE-2026-33002) allowing remote code execution and full CI/CD pipeline compromise. Update to 2.555 now.

Atlassian warns of a high-severity RCE vulnerability (CVE-2026-21570) in Bamboo Data Center. Patch now to secure your CI/CD pipelines from malicious code.
A critical 9.4 CVSS tag poisoning attack (CVE-2026-31976) hit the xygeni-action GitHub Action, injecting a C2 backdoor into CI/CD pipelines. Update now.

OpenSSF warns of "hackerbot-claw," an autonomous AI bot exploiting GitHub Actions to hijack repositories. Secure your CI/CD pipeline before it’s too late.
Jenkins patches a high-severity stored XSS flaw (CVE-2026-27099) and an info disclosure bug. Update to version 2.551 or LTS 2.541.2 to secure pipelines.
Critical PHPUnit flaw CVE-2026-24765 (CVSS 7.8) allows RCE via unsafe deserialization in coverage files. Vulnerability hits CI/CD pipelines. Update now.
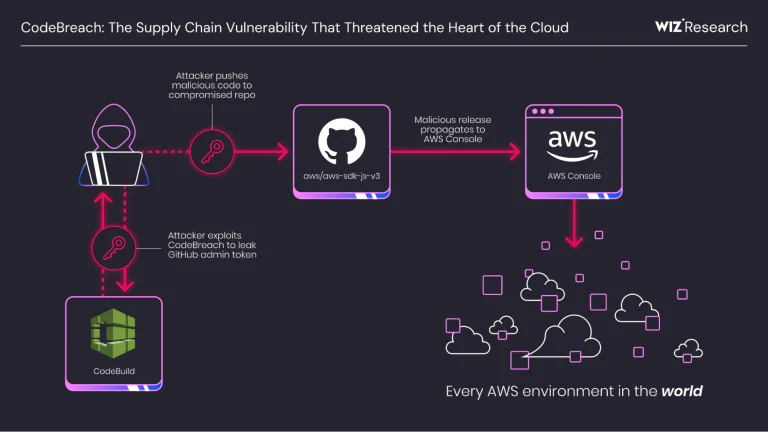
Wiz reveals "CodeBreach": A regex typo in AWS CodeBuild could have let hackers hijack the AWS Console via the JS SDK. Issue is now patched.

Critical GitLab updates (18.6.1/18.5.3) fix severe CI/CD credential theft (CVE-2024-9183) & unauthenticated DoS flaws. Upgrade immediately.

A path traversal flaw (CVE-2025-62725) in Docker Compose lets attackers overwrite host files via remote OCI artifact annotations, triggered by read-only commands.

GitLab patched a critical runner hijacking flaw (CVE-2025-11702) allowing authenticated users to compromise CI/CD pipelines, plus three unauthenticated DoS vulnerabilities.

CVE-2025-4318 (CVSS 9.5) hits AWS Amplify Codegen UI with PoC exploit. RCE flaw puts CI/CD pipelines and developer environments at high risk.
Jenkins plugins hit by CVE-2025-47884 (CVSS 9.1) and more—flaws enable impersonation, XSS, and authentication bypass. Patch now to secure pipelines.