 Do Son
Jenkins fixes 15 vulnerabilities, including remote code execution flaws CVE-2026-117612 and CVE-2026-117614. Upgrade to 2.588 or LTS 2.580.2 now.
CI/CD
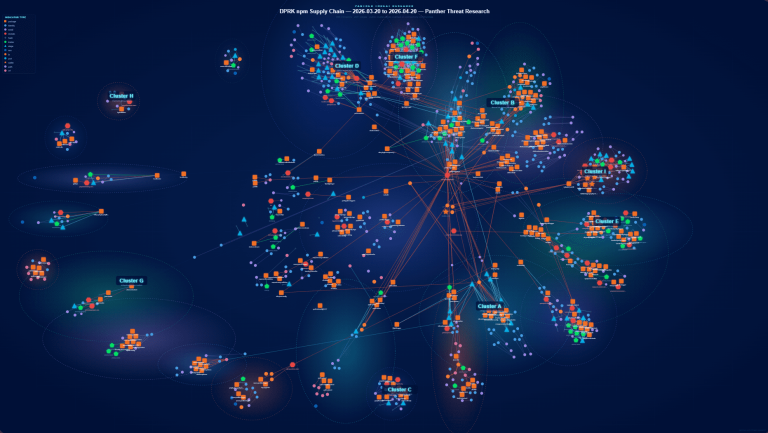
Panther Research exposes a massive 2026 DPRK npm campaign using blockchain dead-drops to steal crypto keys and AI secrets. Secure your CI/CD pipelines now.
Google launches the Android CLI for agent-centric workflows. Reduce LLM token usage by 70% and accelerate app development 3x with official AI-ready tools.

GitLab fixes critical CVE-2025-7659 (CVSS 8.0). Unauthenticated attackers can steal tokens via Web IDE. Update to v18.8.4 now to secure your code.

GitHub walks back its plan to charge $0.002/min for self-hosted runners, postponing the fee indefinitely following intense backlash from the community.

Jenkins patched nine flaws: a High-severity unauthenticated DoS (CVE-2025-67635) via HTTP CLI and XSS via Coverage Plugin. Build tokens are now encrypted. Update to v2.541 immediately.

GitLab patched a High-severity Stored XSS flaw (CVE-2025-11224, CVSS 7.7) in the Kubernetes proxy feature. The bug allows authenticated users to hijack administrator sessions. Update to v18.5.2+.
Jenkins warned of a Critical SAML Plugin flaw (CVE-2025-64131) that allows session replay/hijacking due to a missing cache. Multiple plugins also expose API tokens in plaintext.
Jenkins has patched multiple flaws, including a high-severity DoS vulnerability in its bundled Jetty server that could allow unauthenticated attackers to crash the service.

A critical vulnerability (CVE-2025-54594, CVSS 9.1) in React Native Bottom Tabs’ GitHub Actions allowed RCE and secret exfiltration. The flaw was patched, and no packages were affected.

North Korea's Lazarus Group is waging a covert cyberespionage campaign, poisoning 234+ open-source packages on npm/PyPI to steal secrets from CI/CD pipelines and developer environments.

A critical command injection flaw (CVE-2025-54416) in tj-actions/branch-names GitHub Action allows arbitrary code execution in workflows, affecting over 5,000 public repositories.

A critical CI/CD flaw in remote caches allows undetectable code injection and privilege escalation via cache poisoning, bypassing all security controls.

GitLab issues urgent updates for high-severity flaws in CE/EE, including HTML injection (account takeover) and CI/CD code injection. Upgrade to 18.0.2, 17.11.4, or 17.10.8 immediately.

A high-severity XSS flaw (CVE-2025-5806) in Jenkins Gatling Plugin bypasses CSP, risking session hijacking and credential theft. Downgrade to v1.3.0 immediately!

Socket uncovers malicious RubyGems impersonating Fastlane plugins, stealing sensitive CI/CD data by rerouting Telegram API calls. Beware of fastlane-plugin-telegram-proxy!