 Do Son
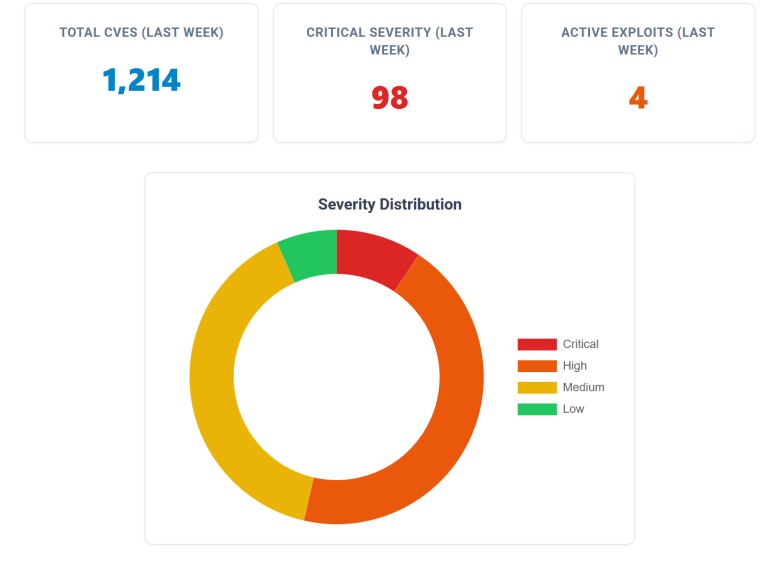
This week's digest: 1,214 new bugs, including active exploits on 2009 Excel fossils and critical 10.0 flaws in new AI/MCP infrastructure. Priority: Patch now.
CISA KEV

Faced with a massive surge in CVEs, NIST has overhauled the NVD. Starting April 2026, only high-risk flaws get full analysis. Check the new triage rules.
CISA adds Microsoft SharePoint spoofing (CVE-2026-32201) and legacy Office RCE (CVE-2009-0238) to its KEV Catalog. Remediation deadline: April 28, 2026.
Urgent Patch Alert: SharePoint Spoofing Under Active Attack as Microsoft Releases April 2026 Updates

Urgent Patch Alert: SharePoint Spoofing Under Active Attack as Microsoft Releases April 2026 Updates
Microsoft’s April 2026 Patch Tuesday fixes 163 flaws, including an exploited SharePoint spoofing bug (CVE-2026-32201). Patch by April 28 per CISA mandate.
CISA adds 7 active exploits to the KEV catalog, from legacy Office bugs to 2026 Fortinet zero-days. Patch these high-risk flaws now to secure your network.
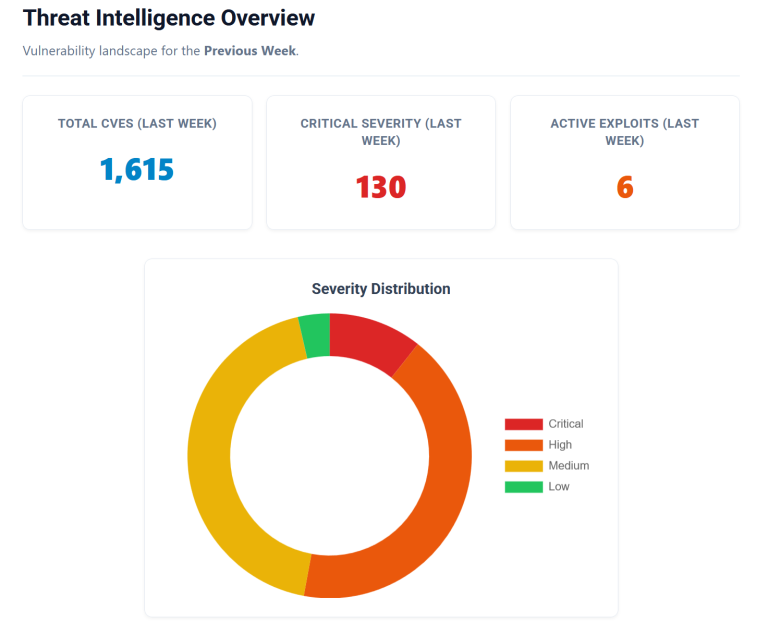
Weekly vulnerability digest (April 6-12, 2026): 1,615 new flaws, CISA KEV alerts for Ivanti and Fortinet, and critical RCE in AI tools like Flowise.

CISA adds critical Ivanti EPMM flaw (CVE-2026-1340) to KEV catalog. The 9.8 CVSS code injection allows unauthenticated RCE. Patch mandated by April 11!

1,361 vulnerabilities found this week: 129 are critical. Prioritize Chrome’s Dawn exploit, FortiClient EMS, and new AI pipeline attacks. Get the full list.
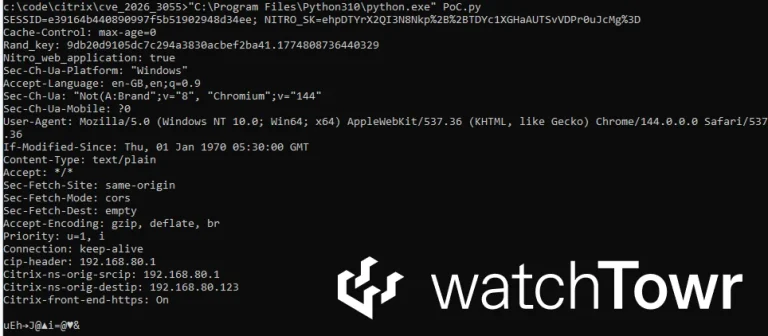
CISA adds Citrix NetScaler CVE-2026-3055 to KEV. This 9.3 CVSS flaw "bleeds" admin sessions via SAML. Federal agencies must patch by April 2, 2026.

1,740 new vulnerabilities, 147 critical. From F5 crashes to a Trivy supply chain attack, here’s your high-priority triage list for March 2026.
CISA adds F5 BIG-IP RCE (CVE-2025-53521) to its KEV Catalog. With a 9.8 CVSS score and active exploits, federal agencies must patch by March 30, 2026.
CISA adds 5 actively exploited flaws to its KEV catalog, including a critical 10.0 CVSS Craft CMS bug and Apple zero-days linked to DarkSword malware.
CISA adds actively exploited Microsoft SharePoint RCE (CVE-2026-20963) and Zimbra XSS (CVE-2025-66376) to its KEV catalog. Update your systems immediately.

CISA adds a Wing FTP Server flaw (CVE-2025-47813) to its KEV catalog. The actively exploited cookie vulnerability exposes internal server paths. Update now.
CISA warns of a critical 10.0 CVSS RCE flaw (CVE-2025-68613) in n8n workflow automation. Update to version 1.122.0 immediately to prevent server takeover.
CISA adds three actively exploited flaws in SolarWinds, Ivanti, and Omnissa to its KEV catalog. Patch these critical enterprise vulnerabilities immediately.
CISA adds actively exploited Qualcomm (CVE-2026-21385) and VMware (CVE-2026-22719) flaws to its KEV catalog. See the impact and patch deadlines inside.
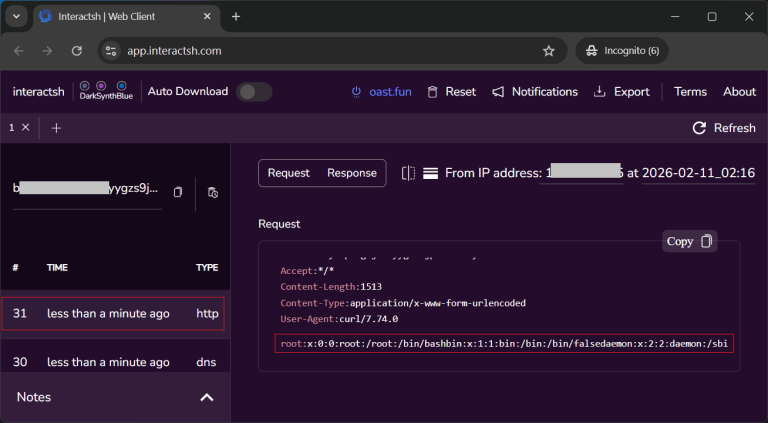
Arctic Wolf warns of CVE-2026-1731, a critical BeyondTrust flaw exploited in the wild. Attackers use it to deploy backdoors. Patch self-hosted instances now.

Public PoC released for critical Oracle E-Business Suite RCE (CVE-2025-61882). Ransomware gangs are actively exploiting this CVSS 9.8 flaw. Patch now.
CISA adds VMware vCenter flaw CVE-2024-37079 (CVSS 9.8) to KEV catalog. Hackers are actively exploiting this RCE bug. Patch immediately.

CISA adds MongoBleed (CVE-2025-14847) to its KEV Catalog after confirming active exploitation. 80,000+ MongoDB servers are at risk. Patch by Jan 19!